TGViewer
Channel Public Channel
Reverse Dungeon

Reverse Dungeon

@reverse_dungeon

Reverser's notes
The Mentor
1989
Subscribers
5.04K
Photos
746
Videos
59
Links
2.3K

Showing posts older than #3910 · Back to latest

Older Posts 19 shown
Post #3906 2.9K
Post #3905 4.84K
Vnutrennee_ustroistvo_Windows_Kliuchevye_komponenty_i_vozmozhnosti.pdf19.7 MB
Всем привет
Принёс вам интересную книжку
Это САКРАЛЬНАЯ вторая часть 7-го издания "Внутреннее устройство Windows"
Да, его нигде нет
Да, на русском
Да, оригинал от издателя!!!
Наслаждайтесь!

эксклюзивненько для @reverse_dungeon
реп и подписку друже можно оформить тут:
https://www.youtube.com/@Eagle_Fly_
@inf0_Trad3r
  • ❤ 43
  • 🐳 1
Post #3904 2.67K
  • ❤‍🔥 6
Post #3894 2.51K
https://malfunction.zip

MALfunction
What is the MALfunction Hackathon

Welcome to the MALfunction Hackathon! This event is designed to educate participants on the inner workings of malware in a controlled environment and give a chance to get into the head of a malware developer. At the start of the hackaton you will be given a theme, a target OS and “Actions on Objectives”. AOO is what we consider the attackers goals. What they want to acomplish with this malware, it could be to deploy ransomware, it could be exfiltrate a lot of data you wont know until the hackathon starts.

On the last day of the hackathon the malware samples will be submitted and ran on the victim VM. There WILL be security tools on the system, you might know what tools you are going against and you may not much like a real world attacker.
  • ❤ 5
Post #3893 1.65K
Post #3892 1.52K

Forwarded from 1N73LL1G3NC3

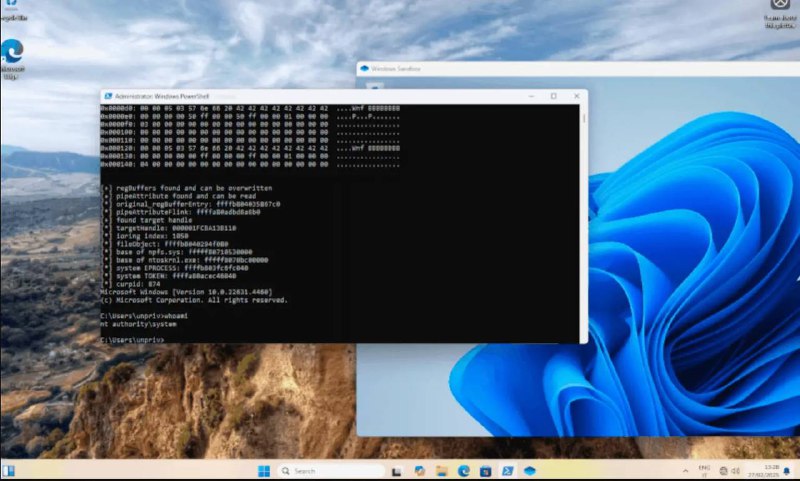
CVE-2025-21333 Windows Hyper-V LPE

Exploit for a zero-day vulnerability in Windows Hyper-V that enables attackers to gain SYSTEM privileges on affected Windows devices. The PoC demonstrates an attack targeting the vkrnlintvsp.sys driver, leveraging an overwrite in the I/O Ring buffer entry to gain arbitrary read/write capabilities in the Windows kernel.
  • ❤‍🔥 4
  • ❤ 2
Post #3891 1.86K
Post #3890 1.68K
Post #3887 2.01K

Forwarded from Security Harvester

x86-64 playground: an online assembly editor and GDB-like debugger
http://x64.halb.it:

1. The app is for anyone that wants to run amd64 assembly snippets or inspect the inner workings of simple Linux ELF files.
2. Combined with Compiler Explorer, this app provides a noise-free environment to learn the basics behind the inner workings of a Linux process.
3. The app places the mobile experience at the center of its design, and can be embedded in any web page to add interactivity to technical tutorials or documentations.

@secharvester
  • ❤ 6
  • ❤‍🔥 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →