TGViewer
Channel Public Channel
Proxy Bar

Proxy Bar

@proxy_bar

Exploits, Hacking and Leaks

Чат группы - https://t.me/

Связь с администрацией и реклама:
@NULL_vm

Поддержать проект:
BTC bc1qmrt229eghjyj9wqa7nmr9j8zuq6khz6km2pker
Subscribers
21.5K
Photos
1.7K
Videos
107
Links
1.8K

Showing posts older than #3304 · Back to latest

Older Posts 20 shown
Post #3303 9.4K
Burp Bounty Pro v3.1.0 supports 5 providers

пора выкачивать
  • 🔥 30
  • 😱 2
Post #3301 6.07K
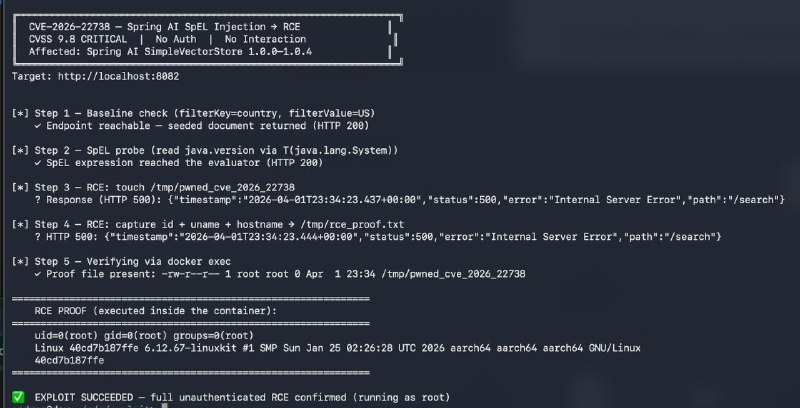
CVE-2026-22738 — SpEL Injection RCE in Spring AI SimpleVectorStore
*
PoC
  • 👍 10
Post #3300 6.05K

Forwarded from IT ARMY OF RUSSIA

Доброго времени!
Приглашаем хакеров и безопасников в IT ARMY OF RUSSIA

Здесь ты сможешь найти коллег по работе и обучиться новым знаниям!
Помогай Родине - вместе с нами!

У нас есть свой форум для общения - XSSF.NET / XSSF.RU
Обсуждайте/Помогайте друг-другу/Ведите деятельность вместе!

Присоединяйся к нам!

Телеграм канал:
https://t.me/itarmyofrussianews
Наш форум:
https://xssf.net / https://xssf.ru
  • 😱 19
  • 👍 17
Post #3299 5.97K
Breaking Process Protection: Exploiting CVE-2026-0828 in ProcessMonitorDriver.sys

Introduction

A recently disclosed vulnerability CVE-2026-0828 in the Windows kernel driver ProcessMonitorDriver.sys exposes a dangerous capability: any user-mode application that obtains a handle to the device can terminate arbitrary processes, including protected system processes, without proper access-control checks. This flaw effectively bypasses the normal Windows security model that protects critical system services and security components.…

https://core-jmp.org/2026/04/breaking-process-protection-exploiting-cve-2026-0828-in-processmonitordriver-sys/
  • 🔥 8
  • 👍 3
Post #3297 5.85K
Credential Dumping from LSASS (Windows Authentication Secrets)

Original text by Raj

The article explains how attackers extract authentication secrets from the Local Security Authority Subsystem Service (LSASS) process in Windows. LSASS is responsible for enforcing system security policies, handling logins, and storing authentication data such as NTLM password hashes, Kerberos tickets, and cached credentials in memory.

Because these credentials must remain in…

https://core-jmp.org/2026/04/credential-dumping-from-lsass-windows-authentication-secrets/
  • 👍 10
  • 🔥 2
Post #3296 9.03K
Hypervisor-Based Defense (Windows Kernel Protection)

Original text by Ido Veltzman

The article “Hypervisor-Based Defense” discusses how hypervisors can be used as a powerful defensive layer to protect Windows systems from kernel-level attacks. The author explains that modern attackers frequently target the kernel using techniques such as Bring Your Own Vulnerable Driver (BYOVD) or malicious kernel modules that bypass traditional security…

https://core-jmp.org/2026/04/hypervisor-based-defense-windows-kernel-protection/
  • 👍 7
Post #3295 5.2K
Reverse engineering Realtek RTL8761B* Bluetooth chips, to make better Bluetooth security tools & classes

Original text by Xeno Kovah

The article “Hardwear.io 2025 – Reverse Engineering Realtek Bluetooth Chips” from Dark Mentor describes research into undocumented Realtek Bluetooth chipsets commonly used in inexpensive USB adapters. The author investigated devices based on the RTL8761B chipset with the goal of enabling deeper Bluetooth security research without relying on expensive development boards.…

https://core-jmp.org/2026/04/reverse-engineering-realtek-rtl8761b-bluetooth-chips-to-make-better-bluetooth-security-tools-classes/
  • 👍 5
Post #3294 5.64K
RCE Vulnerability in Vim (CVE-2026-34714)

mcedit бы так не поступил

PoC
  • 😱 23
  • 👍 3
  • 🔥 2
Post #3293 5.11K
Understanding Out-Of-Bounds in Windows Kernel Driver

Original text by Jay Pandya

The article “Understanding Out-of-Bounds in Windows Kernel Driver” explains how out-of-bounds (OOB) vulnerabilities occur in Windows kernel drivers and why they are dangerous from a security perspective. Out-of-bounds bugs appear when code reads or writes memory outside the boundaries of a valid buffer or structure, often due to incorrect index…

https://core-jmp.org/2026/04/understanding-out-of-bounds-in-windows-kernel-driver/
  • 👍 8
Post #3292 5.16K
MAD Bugs: Claude Wrote a Full FreeBSD Remote Kernel RCE with Root Shell (CVE-2026-4747)

Original text by CALIF

The article “MAD Bugs: Claude Wrote a Full FreeBSD Remote Kernel RCE with Root Shell” describes an experiment demonstrating how a modern large language model can assist in advanced vulnerability research and exploit development. Researchers tested the AI model Claude against CVE-2026-4747, a vulnerability in FreeBSD’s RPCSEC_GSS implementation. Starting only with…

https://core-jmp.org/2026/04/mad-bugs-claude-wrote-a-full-freebsd-remote-kernel-rce-with-root-shell-cve-2026-4747/
  • 👍 7
  • 🔥 3
Post #3291
Channel photo updated
Post #3289 6K
CVE-2026-4747
*
Claude Wrote a Full FreeBSD Remote Kernel RCE with Root Shell
*
exploit.py
  • 👍 15
  • 🔥 14
  • 😱 3
Post #3288 5.62K
Unauthenticated MCP Endpoint Allows Remote Nginx Takeover
*
Detail and PoC
  • 🔥 10
  • 👍 7
Post #3287 5.52K
CVE-2026-1207
*
Django SQL Injection in RasterField lookup

Chain
  • 👍 11
  • 🔥 1
Post #3286 5.67K
Async Windows Gone Wrong: Exploiting a Win32k Type Confusion Bug

Original text by s4dbrd

The article analyzes a Windows kernel vulnerability in win32kfull.sys involving a type confusion bug in the asynchronous window action processing path. The vulnerability occurs in logic responsible for handling window-related operations when certain internal features are enabled through Microsoft’s feature-flag system. Because of inconsistent object handling, the kernel may treat one…

https://core-jmp.org/2026/03/async-windows-gone-wrong-exploiting-a-win32k-type-confusion-bug/
  • 🔥 11
  • 👍 3
Post #3285 4.86K
Breaking the JIT: Exploiting a SpiderMonkey Type Confusion Bug

Original text by @qriousec

The article analyzes CVE-2025-14325, a vulnerability in the SpiderMonkey JavaScript engine used by Mozilla Firefox. The bug originates in the Baseline JIT compiler, specifically in the implementation of inline caches (ICs) that optimize property access operations in JavaScript. Inline caches speed up execution by remembering object layouts and reusing cached assumptions…

https://core-jmp.org/2026/03/breaking-the-jit-exploiting-a-spidermonkey-type-confusion-bug/
  • 🔥 6
Post #3284 5.04K
Inside the Payload: Manual Shellcode Analysis with Ghidra

Original text by Matthew

The article explains a practical workflow for manually analyzing malicious Windows shellcode using Ghidra and a debugger such as x32dbg. Instead of relying on automated emulators, the author demonstrates how to perform manual reverse engineering to understand the behavior of shellcode used by frameworks like Cobalt Strike. The tutorial begins with…

https://core-jmp.org/2026/03/inside-the-payload-manual-shellcode-analysis-with-ghidra/
  • 🔥 6
  • 👍 5
Post #3283 5.09K
ыхых Claude Code Source Snapshot
*
for Security Research
- ну конечно, о чем речь вообще, брат)
  • 👍 14
  • 😱 7
  • 🔥 4
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →