TGViewer
Channel Public Channel
Proxy Bar

Proxy Bar

@proxy_bar

Exploits, Hacking and Leaks

Чат группы - https://t.me/

Связь с администрацией и реклама:
@NULL_vm

Поддержать проект:
BTC bc1qmrt229eghjyj9wqa7nmr9j8zuq6khz6km2pker
Subscribers
21.5K
Photos
1.7K
Videos
107
Links
1.8K

Showing posts older than #3242 · Back to latest

Older Posts 20 shown
Post #3241 4.38K
TP-Link Tapo C200: Hardcoded Keys, Buffer Overflows and Privacy in the Era of AI Assisted Reverse Engineering

Original textby Simone Margaritelli

The article describes a security research project analyzing the firmware of the TP-Link Tapo C200 IP camera, demonstrating how modern AI-assisted reverse engineering can significantly accelerate vulnerability discovery in IoT devices. The author extracts and studies the camera firmware, using tools such as binwalk, Android app decompilation, and AI assistance to…

https://core-jmp.org/2026/03/tp-link-tapo-c200-hardcoded-keys-buffer-overflows-and-privacy-in-the-era-of-ai-assisted-reverse-engineering/
  • 🔥 15
Post #3240 4.74K
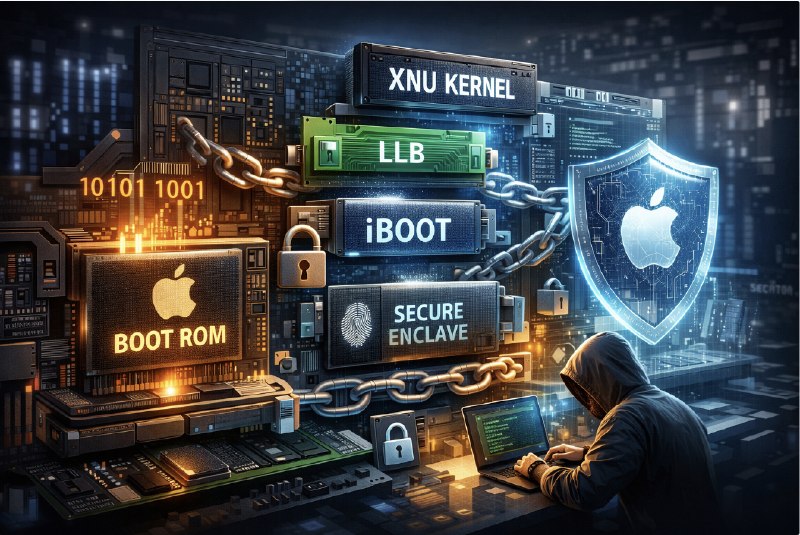
Booting into Trust: Reverse Engineering macOS Secure Boot Internals

Original textby int

The article provides a deep reverse-engineering oriented analysis of the macOS secure boot chain on Apple Silicon, explaining how Apple constructs a hardware-anchored security architecture that protects the system from the moment power is applied until userland starts. The security model begins with the Boot ROM (SecureROM) embedded directly into the SoC.…

https://core-jmp.org/2026/03/booting-into-trust-reverse-engineering-macos-secure-boot-internals/
  • 🔥 7
  • 👍 3
Post #3239 4.62K
Invisible Execution: Hiding Malware with Unwind Metadata Manipulation

Original text by klezVirus

The article introduces BYOUD (Bring Your Own Unwind Data), a novel stack-evasion technique designed to bypass modern endpoint detection and response (EDR) systems that rely on call-stack inspection to identify malicious execution. Traditional stack-spoofing techniques modify return addresses or construct synthetic stack frames to disguise the origin of a call. However,…

https://core-jmp.org/2026/03/invisible-execution-hiding-malware-with-unwind-metadata-manipulation/
  • 👍 10
Post #3238 5.6K
Ну во первых это красиво !
*
snap-confine + systemd-tmpfiles = root (CVE-2026-3888)
*
Дырка появляется когда два дурака (snap-confine и systemd-tmpfiles) жмут руки.
НО то ладно, дальше больше.
Нужно проломленным локальным юзером прождать 10 ДНЕЙ (на Ubuntu 24.04.х ) и 30 ДНЕЙ (на Ubuntu 24.10.х) пока systemd-tmpfiles удалит нужный подкаталог в /tmp, а потом ещё выиграть гонку в момент пересборки sandbox.
  • 🔥 22
  • 👍 10
Post #3237 5.1K
AV/EDR Lab Env Setup
*
LetsGO
  • 👍 9
  • 🔥 7
Post #3236 5.94K
ODR: Internals of Microsoft’s New Native MCP Registration

Original text by originhq

The article analyzes Microsoft’s new ODR mechanism related to MCP registration and explains how it integrates with the emerging Model Context Protocol (MCP) ecosystem. MCP is an open protocol designed to standardize how AI agents and applications interact with external tools, data sources, and services. Instead of building custom integrations for…

https://core-jmp.org/2026/03/odr-internals-of-microsofts-new-native-mcp-registration/
  • 👍 9
Post #3235 5K
NT AFD.SYS HTTP Downloader: From First Syscall to bypass the majority of usermode EDR hooks

Text and code by Eleven Red Pandas https://github.com/oxfemale · https://x.com/bytecodevm

The article explores a low-level networking technique on Windows that bypasses the traditional Winsock API layer by communicating directly with the kernel networking driver AFD (Ancillary Function Driver) through Native API calls such as NtCreateFile and NtDeviceIoControlFile. Instead of using standard functions from ws2_32.dll, the…

https://core-jmp.org/2026/03/nt-afd-sys-http-downloader-from-first-syscall-to-bypass-the-majority-of-usermode-edr-hooks/
  • 😱 8
  • 👍 4
  • 🔥 1
Post #3234 4.99K
Vulnerabilities in Broadcom VMware Aria Operations: Privilege Escalation (CVE-2025-41245 / CVE-2026-22721)

Original text by Lorin Lehawany

The article analyzes two security vulnerabilities discovered in Broadcom VMware Aria Operations, focusing on how weaknesses in privilege handling and credential management can lead to privilege escalation within virtualized infrastructure environments. The research examines CVE-2025-41245 and CVE-2026-22721, demonstrating how attackers with limited privileges can escalate their access and gain control…

https://core-jmp.org/2026/03/vulnerabilities-in-broadcom-vmware-aria-operations-privilege-escalation-cve-2025-41245-cve-2026-22721/
  • 👍 6
Post #3233 4.96K
A Deep Dive into the GetProcessHandleFromHwnd API

Original text by James Forshaw

The article provides a deep technical analysis of the Windows API GetProcessHandleFromHwnd, examining its historical evolution and the security implications of its implementation. The API is intended to return a handle to the process that owns a specified window handle (HWND), simplifying interactions with GUI processes. The research begins by…

https://core-jmp.org/2026/03/a-deep-dive-into-the-getprocesshandlefromhwnd-api/
  • 👍 5
Post #3231 6.63K
CVE-2026-25769 - RCE Wazuh Cluster
*
Exploit
  • 👍 15
  • 🔥 10
Post #3230 6.23K
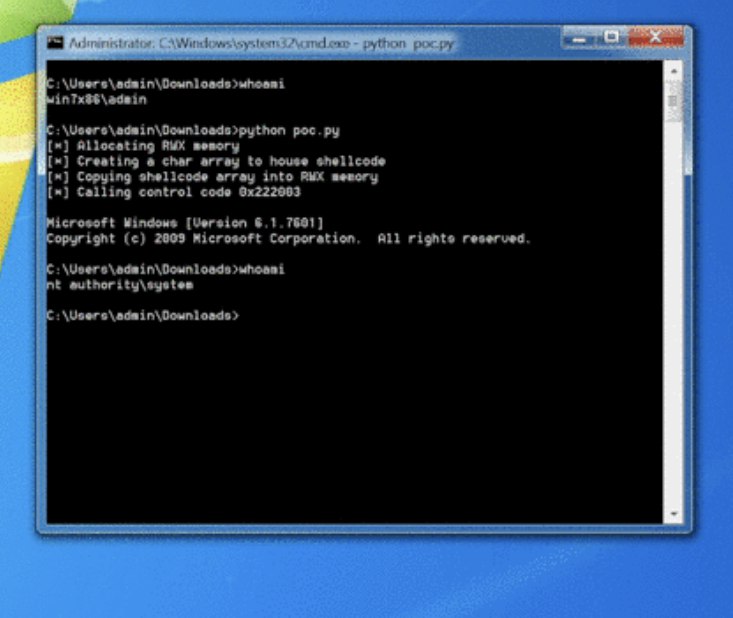
0x00 – Introduction to Windows Kernel Exploitation

Original text by wetw0rk

The article serves as the introductory part of a tutorial series on Windows kernel exploitation and focuses on preparing researchers for practical vulnerability research in the Windows kernel. The author explains the fundamental concepts required before attempting kernel exploitation, including the differences between user-mode and kernel-mode execution, privilege levels, and why…

https://core-jmp.org/2026/03/0x00-introduction-to-windows-kernel-exploitation/
  • 🔥 13
  • 😱 3
Post #3229 5.3K
Windows 0day (BSOD)
*
Won’t Fix: Kernel DoS in clfs.sys via NULL FastMutex Dereference

Original text by Baptiste Crépin

The article analyzes a Windows kernel vulnerability involving a NULL pointer dereference in the CLFS (Common Log File System) driver caused by misuse of a FAST_MUTEX structure. The research explains how Windows kernel synchronization primitives such as fast mutexes are used to enforce mutual exclusion in driver code. A fast…

https://core-jmp.org/2026/03/wont-fix-kernel-dos-in-clfs-sys-via-null-fastmutex-dereference/
  • 👍 7
  • 🔥 5
Post #3228 5.08K
WSL, COM Hooking, & RTTI

Original text by Jonathan Johnson

The article explores a technique for hooking COM methods inside Windows Subsystem for Linux (WSL) by leveraging C++ Runtime Type Information (RTTI). The research begins with the author’s attempt to instrument and log activity within WSL components that interact with Windows through COM interfaces. Instead of relying on traditional API-level…

https://core-jmp.org/2026/03/wsl-com-hooking-rtti/
  • 🔥 7
Post #3227 5.38K
Сквозь кротовую нору с Морганом Фрименом !
*
Червяч0к
  • 👍 10
  • 🔥 9
  • 😱 2
Post #3226 6.32K
VMkatz
*
Извлекем учетные данные Windows напрямую из снашотов памяти виртуальной машины и виртуальных дисков.

GET
  • 👍 13
  • 😱 8
Post #3225 5.05K
macOS cmd-obfuscation
*
В ArgFuscator добавили более чем 60 нативных бинарей macOS готовых к обфускации.
На видео EDR, пытающийся предотвратить дамп учеток.
  • 🔥 17
  • 👍 4
Post #3224 5.07K
EDR Internals for macOS and Linux

Original text by Kyle Avery

The article analyzes how Endpoint Detection and Response (EDR) systems operate internally on macOS and Linux, focusing on the telemetry sources and monitoring mechanisms these agents rely on. The research notes that most public discussions about EDR internals focus on Windows, while macOS and Linux implementations remain less documented despite…

https://core-jmp.org/2026/03/edr-internals-for-macos-and-linux/
  • 👍 11
Post #3223 4.61K
Peeling Back the Socket Layer: Reverse Engineering Windows AFD.sys

Original text by Mateusz Lewczak

Part 1: Investigating Undocumented Interfaces

The four-part research series explores the reverse engineering of the Windows AFD.sys (Ancillary Function Driver) to understand how networking operations work beneath the Winsock API. AFD.sys is a kernel driver that acts as a bridge between user-mode socket APIs and the lower networking stack, translating…

https://core-jmp.org/2026/03/peeling-back-the-socket-layer-reverse-engineering-windows-afd-sys/
  • 👍 9
Post #3222 4.43K
LOLExfil: Stealthy Data Exfiltration Using Living-Off-the-Land Techniques

LOLExfil, a concept and toolset for performing data exfiltration using “Living-Off-the-Land” (LOL) techniques that rely on legitimate system utilities, trusted services, and built-in operating-system functionality rather than custom malware. The research explores how attackers can abuse standard tools already present in enterprise environments—such as scripting engines, networking utilities, cloud APIs, and legitimate web services—to covertly…

https://core-jmp.org/2026/03/lolexfil-stealthy-data-exfiltration-using-living-off-the-land-techniques/
  • 🔥 11
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →