
Stealth Injection with ROP: Thread Hijacking Without Executable Memory
Original text by Umarex
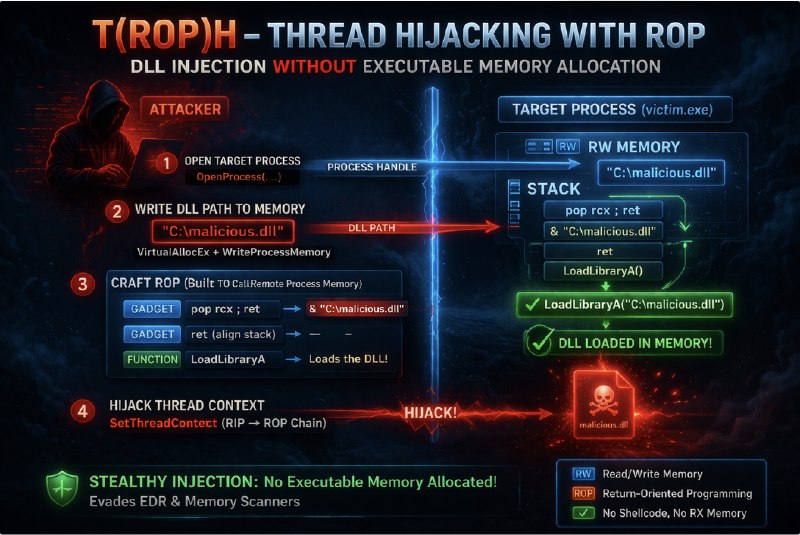
The article introduces a technique called T(ROP)H (Thread Hijacking with ROP), which enables DLL injection into a remote Windows process without allocating executable memory. Traditional thread hijacking typically allocates memory with execute permissions and places shellcode there before redirecting a thread’s instruction pointer to the payload. However, allocating executable memory is…
https://core-jmp.org/2026/03/stealth-injection-with-rop-thread-hijacking-without-executable-memory/
Post #3270
5.27K
- 👍 7
- 🔥 4