
❗ CVEAlertor keeps you ahead of newly disclosed vulnerabilities
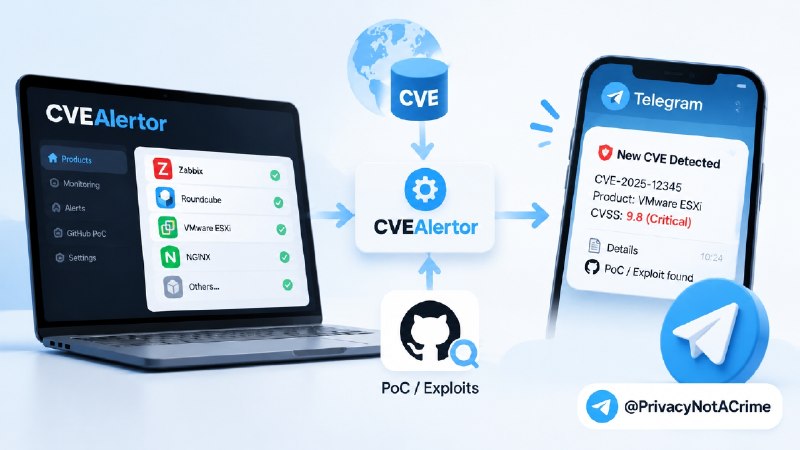
Monitoring security vulnerabilities no longer requires constant dashboard monitoring or scrolling through endless security bulletins. CVEAlertor, developed by RedSideSecurity, automates this entire process by sending instant Telegram notifications whenever a new CVE appears for software running in your infrastructure.
This lightweight solution filters out the noise of blanket security feeds and delivers only what matters to your specific tech stack.
🔩 Simple yet powerful workflow
Users specify which products belong to their environment, whether Zabbix for monitoring, Roundcube for email, VMware ESXi for virtualization, or any other supported software. The initial run pulls all existing CVEs and builds a baseline.
Subsequent checks compare fresh data against that baseline, triggering alerts exclusively for genuinely new vulnerabilities. Beyond CVE tracking, the tool actively scans GitHub daily for public proofs of concept and exploits related to your tracked vulnerabilities.
🕹 Flexible configuration options
Administrators control CVSS score thresholds to focus on critical threats, set checking intervals from thirty minutes to daily cycles, and choose between one time scans or continuous watch modes. Optional NVD API keys increase rate limits for larger product inventories. Telegram integration uses simple bot tokens and chat IDs, avoiding complex authentication requirements.
🐱 Check this tool at GitHub
😊 If you enjoyed the article share it with your friends and follow us.
#CVE #VulnerabilityManagement #CyberSecurity #OpenSource #ThreatIntelligence
@PrivacyNotACrime 🗽 ⌨️ Chat
Post #542
97
- ✍ 4
- 👌 2