TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3438 · Back to latest

Older Posts 19 shown
Post #3437 397
Deceptive Video-App Package Turns Mac Passwords Into Root Access

Security researchers have uncovered CloudSyncD, a newly identified macOS backdoor distributed through a malicious application masquerading as the Zoom client.

🔗 Read More
Post #3436 381
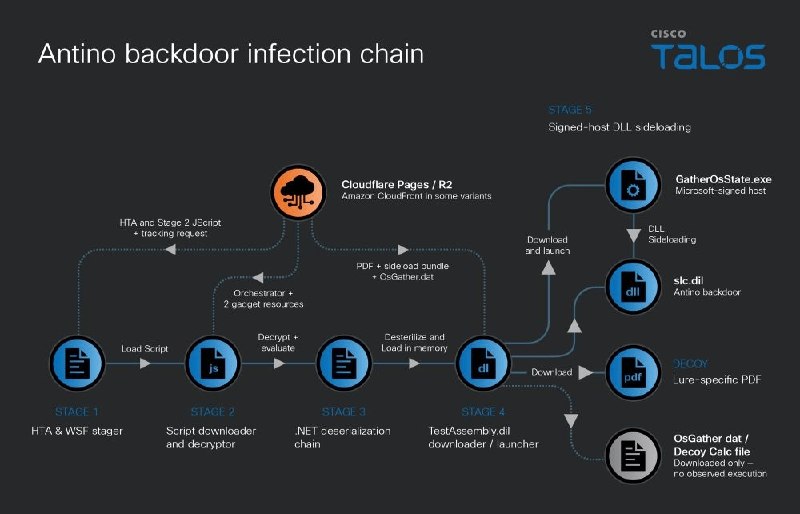
🔴 Antino Backdoor Lets China-Linked UAT-11587 Turn Microsoft 365 Into a C2 Channel

Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments.

Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight Asian countries. The toolset includes a previously undocumented backdoor Talos named Antino, and the thing that makes it worth paying attention to isn’t how it gets in. It’s where it hides once it’s there.

Antino is written in Rust and works on both 32-bit and 64-bit versions of Windows. It supports the usual backdoor features, including shell and PowerShell access, file transfers, in-memory shellcode execution and persistence.
Post #3435 387
🔴 Anything left from France?

NATURABUY ~1.43M USER RECORDS / 363K NICKNAMES FOR SALE

A threat actor on an underground forum sells a user database associated with NaturaBuy (French hunting/fishing/shooting marketplace, naturabuy[.]fr).

The dataset includes:

* ~1.43 million unique user records (~85 MB CSV)
* ~363k account nicknames
* Street addresses, zip codes, cities, countries alleged
* ~11.8k companies / ~8.0k with SIRET numbers alleged
* Majority France, plus BE/CH/IT/ES/DE/CA and others alleged
Post #3434
PPHM HACKER NEWS pinned «🚨 Cybersecurity Moves Fast. Stay Ahead! Stay connected with the latest cyber threats, malware research, security news, vulnerabilities, and expert insights. 🔐 🚀 Join the group, share your knowledge, ask questions, and connect with others passionate about…»
Post #3433 445
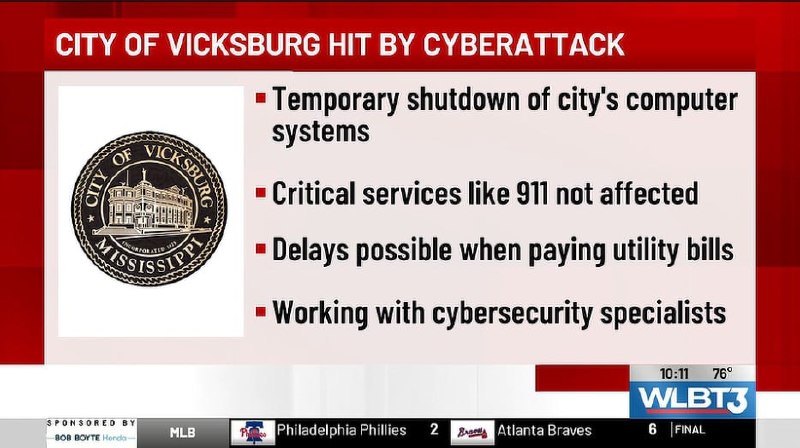
🔴 Ransomware attack forces City of Vicksburg to shut down computer systems

The City of Vicksburg, Mississippi, temporarily shut down its computer systems after confirming a ransomware attack on October 1.
⠀
Critical services, including 911, police, fire and utilities, remain operational.

In-person utility payments may be delayed, but residents will not receive penalties or have services terminated while the systems are offline.
⠀
The city is working with external cybersecurity specialists, the FBI, the Department of Homeland Security and state officials to investigate the attack and securely restore affected systems.

Officials have not determined whether personal or confidential information was accessed or stolen.
  • ❤ 2
Post #3432 437
PPHM HACKER NEWS 🚨 Bloody Altercation Between Two Flydubai Pilots 🔺 A passenger told Israel's Channel 12 that they heard shouting and, after the cockpit door opened, saw traces of blood and a pilot who had been wounded by a knife. The passenger also stated that some travelers…
🚨 UAE Attorney General: Flydubai Co-Pilot Intended to Commit a Terrorist Act

UAE Attorney General:

Investigations into the Flydubai flight incident indicate that the co-pilot intended to carry out a terrorist attack.

According to the investigation, the co-pilot began executing his plan during the flight and attacked the pilot in the cockpit with an emergency axe. The investigation is ongoing to determine all the circumstances and details surrounding the incident.

Earlier, senior intelligence and law enforcement officials said that the Flydubai co-pilot, who is accused of attacking the captain on Wednesday and attempting to bring down a flight bound for Israel, is an Omani citizen. The individual had reportedly previously been suspended from flying by Oman Air after being identified as a security threat.
Post #3430 225
🔴 China Railway 12306 Dataset With 221 Million Records Offered for Sale

A dataset containing information from China Railway 12306 has been offered for sale on a forum.

China Railway 12306 is the official ticketing platform for China's state railway network.

The seller claims the dataset contains approximately 221.23 million user records.

According to the sample shown, the information includes usernames, real names, identification card numbers, gender, dates of birth, mobile numbers, verification status, registration information, account balances, reward points, student information, ticket counts, and travel-related data.

The seller is asking $500 for the dataset, with payment requested in cryptocurrency.
Post #3429 158
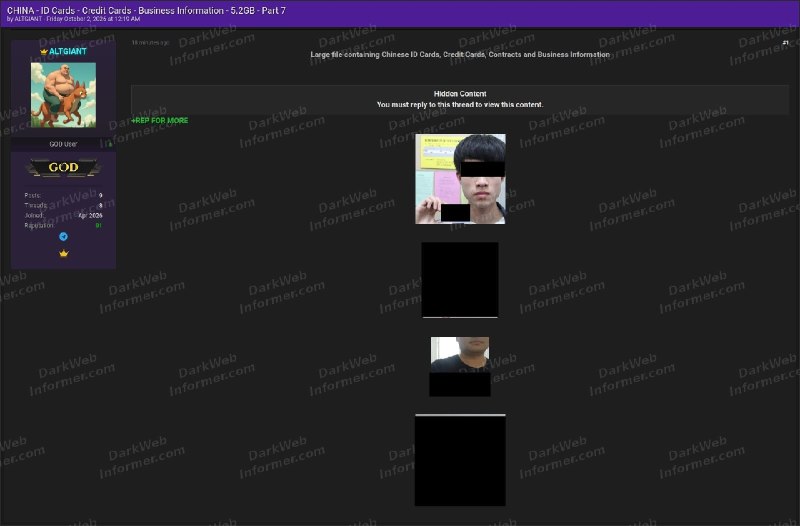
🔴 5.2 GB Collection of Chinese ID Cards and Business Data Shared

A 5.2 GB collection containing sensitive personal and business information from China has been shared on a forum.

The post describes the material as Part 7 of a larger collection and claims it contains Chinese identification cards, credit card information, contracts, and business-related records.

Images included with the post show samples of identification documents, photographs, and other purported records from the collection.
Post #3428 130
Open Criminal Infrastructure Exposes Database Attack Playbook and Credential Arsenal

An attacker-controlled server left exposed to the public internet has revealed a detailed post-exploitation toolkit used in an intrusion linked to an environment associated with Mexican airline Viva Aerobus.

🔗 Read More
Post #3427 125
🔴 macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor

A macOS dropper has been found inside a disguised Zoom client. The malware is tracked as CloudSyncD and is designed to deliver a persistent and stealthy backdoor.

Researchers at Jamf first noticed this malware still in development in mid-September. Within days, other samples were found suggesting it has now progressed from testing and development to deployment.

The malware infection process is initiated by any of the standard social engineering methods designed to persuade or trick victims into downloading dangerous content. In this case it is malware hidden in malicious code disguised as a Zoom Mac installer. If the phish is successful, a malware dropper is delivered to the victim as a disk image that mounts as a volume named Zoom. This dropper contains the payload but must be activated by the victim – hence the disguise as a Zoom installer. The victim is guided through the activation thinking it will install Zoom, but it actually installs CloudSyncD.
Post #3426 106
🔴 Malicious Linux Implants Mimic Asian Mail Security Products

Cutting-edge malware developers have been using their intimate knowledge of Korean and Taiwanese network edge appliances to build Linux implants that infect and mimic them to an extraordinary degree.

It's common enough for malicious software to imitate legitimate software, superficially. An unwelcome program might name itself after something it expects in its target environment, so that if a passerby spots it, they might not think much of it. A few new Linux backdoors go further than this, though, by imitating the filenames, firewall-allowed traffic, and other specific operating habits of the popular Asian email security appliances they infect.
Post #3425 106
🔴 Dell asks admins to patch max severity CSM flaws as soon as possible

Dell has patched two maximum severity vulnerabilities in the Container Storage Modules (CSM) that connect Dell enterprise storage arrays to Kubernetes environments.

CSM supports Dell's primary storage platforms (PowerStore, PowerScale, PowerFlex, PowerMax, and Unity XT), and it extends the capabilities of the standard Container Storage Interface (CSI) drivers for Kubernetes.

In a security advisory published on Thursday, Dell said that both critical security flaws were found in the Dell CSM Authorization security module and stem from "missing authentication for critical functions" weaknesses.
Post #3424 120
🔴 Click2Shell is the new heart attack for WordPress! One click to take over your server

A vulnerability called Click2Shell has been discovered in WordPress core, which allows attackers to forcibly install themes from the official WordPress.org catalog.

Experts warn that, combined with a vulnerability in the installed theme, this issue can be exploited to remotely execute arbitrary PHP code on the server.

The Click2Shell vulnerability was reported by Paulos Yibelo, a researcher at pwn.ai, who notified WordPress developers of the issue on August 22, 2026. The fix was released on September 17, 2026, and is included in WordPress 7.1.1.
Post #3423 115
🔴 OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling

OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported.

"We have parted ways with three individuals for violating our policies on accessing and handling sensitive company information," a spokesperson for the company was quoted as saying. "Our investigation confirmed that these individuals mishandled sensitive information outside established company procedures, violating our policies and breaking the trust essential to our work."

The impacted employees are Jasmine Wang, Tomek Korbak, and Mikita Balesni, the Journal reported, citing people familiar with the matter. The three researchers have all previously expressed concerns about the pace of artificial intelligence (AI) development.

It's said that the individuals shared confidential information with a third-party AI-safety organization. The name of the organization was not disclosed. According to Bloomberg, the mishandled information pertained to OpenAI's infrastructure architecture.

The departures follow a report from The New York Times that OpenAI had brushed aside employees' warnings about its safety practices when testing AI models, describing a pattern of the company deprioritizing security protocols in favor of releasing them on time.
Post #3422 116
🔴 Microsoft’s X account hacked in crypto pump-and-dump scheme

On Thursday, unknown attackers hijacked the official Microsoft account on X, which has over 13 million followers, in what appeared to be a pump-and-dump scheme promoting a crypto token.

The attack began when the Microsoft account (@Microsoft) followed and reposted a tweet from another now-suspended X account (@clippymsftcto) impersonating Microsoft's Clippy virtual assistant, The Verge first reported.

While @clippymsftcto has been suspended, another X account (@ClippyMSFT) that reposted Microsoft's tweet is still promoting a $Clippy crypto token, claiming that it has "has a liquidity pool paired directly with $MSFT."
Post #3421 125
🔴 AI Agents Aimed SQL Injection at US and Canadian Government Sites

AI agents appear to have attempted to hack a US Department of Education website and a Library and Archives Canada service while trying to access public data, according to AI research lab Transluce.

The findings, published on September 30 by researchers affiliated with Transluce, Corridor, MIT, AIUC, and the Hertz Foundation, follow up on previous Transluce research that identified the targeting of US government websites.

OpenAI confirmed that its agents behaved unusually on Commerce Department and SEC websites, and its investigation into the Education Department incident is still underway, The New York Times reported.
Post #3420 120
🔴 Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools

Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled.

With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. Advanced Protection is a security setting that turns on all Android's security features to secure the device against potential threats.
Post #3419 124
🔴 Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes

The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation.

The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8), allows unauthenticated attackers to write arbitrary files on the underlying system.

"An improper limitation of a pathname to a restricted directory ('path traversal') [CWE-22] and improper neutralization of NULL byte or NULL character [CWE-158] vulnerability may allow an unauthenticated attacker to write arbitrary files on the underlying system via crafted HTTP or HTTPS requests," Fortinet said in an advisory.
Post #3418 136
🔴 Calling all RCEs! How AI is changing vulnerabilities: Google data

Artificial intelligence has begun to have a significant impact not only on the speed of vulnerability detection, but also on the nature of the errors found. Google researchers have discovered a particularly significant difference: half of the vulnerabilities identified by AI allow remote code execution, while among the other errors detected, this percentage reaches only 26%.

The Google Threat Intelligence Group studied statistics from January 2025 to August 2026 and concluded that the vulnerability market has accelerated significantly. According to the analysis, researchers reported 5,045 bugs in January 2026, 10,477 in July, and 10,740 in August.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →