TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3378 · Back to latest

Older Posts 20 shown
Post #3377 136
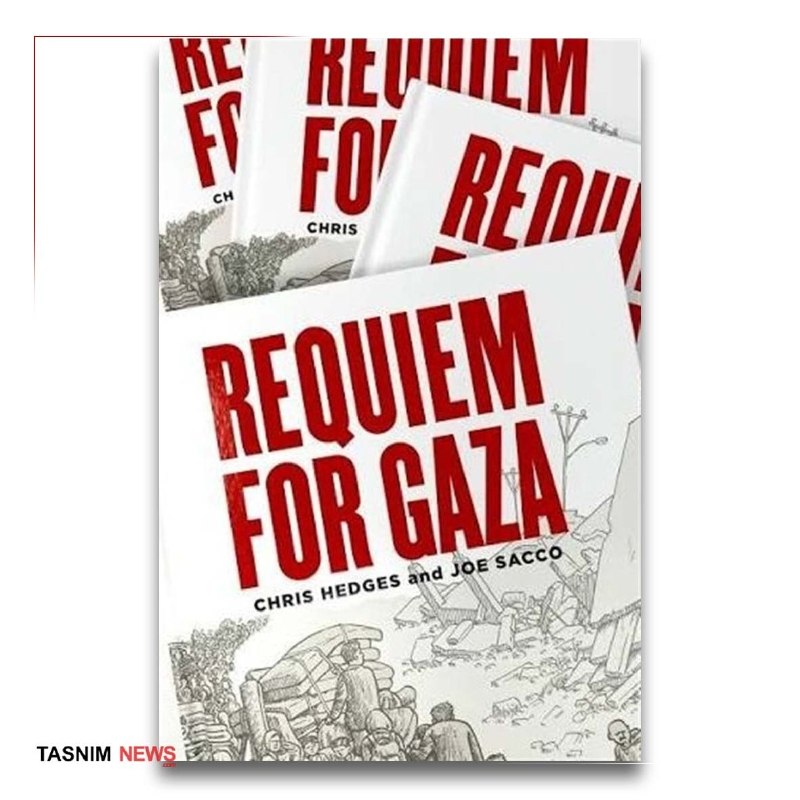
🚨 Two American Journalists Deliver a Blow to Israel

One of the Year’s Most Harrowing Illustrated Documentaries Unveiled

🔹 Bookstores in New York, London, and Paris witnessed an unusual trend after 2024: works centered on Palestine climbed the bestseller lists, reflecting growing public interest worldwide in historical accounts of Palestinian suffering and resistance.

🔹 The involvement of prominent figures in international documentary journalism marked another step in documenting alleged war crimes. That effort is now continuing with the upcoming release of one of the year’s most harrowing works of illustrated nonfiction.

🔹 A Requiem for Gaza is a major recent work of investigative journalism and illustrated documentary literature. It examines the human toll, wartime devastation, and destruction in Gaza following the October 7 attacks—known by Hamas as Operation Al-Aqsa Flood—and Israel’s subsequent military campaign. The book is expected to be unveiled soon.

🔹 In spring 2025, cartoonist Joe Sacco and Chris Hedges, a former Middle East bureau chief for The New York Times, traveled to Cairo, where they interviewed members of 29 Palestinian families who had recently left Gaza.

📝 The book brings together Hedges’ accounts of those conversations with Sacco’s illustrations and comics, creating a visual and written record of their experiences.
Post #3375 134
PPHM HACKER NEWS 🚨 Bloody Altercation Between Two Flydubai Pilots 🔺 A passenger told Israel's Channel 12 that they heard shouting and, after the cockpit door opened, saw traces of blood and a pilot who had been wounded by a knife. The passenger also stated that some travelers…
🎥 Video of the moment of the emergency landing of the Fly Dubai plane after the fight in the cabin
Post #3374 133
PPHM HACKER NEWS 🚨 Amit Segal, a reporter for Hebrew Channel 12: Officials are investigating whether one pilot stabbed the other. 🔺 Another plane is scheduled to be dispatched from Dubai to Saudi Arabia to pick up the passengers and then continue the flight to Israel.
🚨 Bloody Altercation Between Two Flydubai Pilots

🔺 A passenger told Israel's Channel 12 that they heard shouting and, after the cockpit door opened, saw traces of blood and a pilot who had been wounded by a knife. The passenger also stated that some travelers intervened to bring the situation under control.

🔺 However, claims that one of the pilots deliberately intended to commit suicide and crash the plane have not yet been officially confirmed.
Post #3373 127
PPHM HACKER NEWS 🚨 Flights at Ben Gurion Airport have been suspended. 🔺 A Flydubai flight en route from Dubai to Israel has landed at Tabuk Airport in Saudi Arabia. 🔺 Israeli media report that the request for assistance was prompted by an altercation and fight among passengers…
🚨 Amit Segal, a reporter for Hebrew Channel 12: Officials are investigating whether one pilot stabbed the other.

🔺 Another plane is scheduled to be dispatched from Dubai to Saudi Arabia to pick up the passengers and then continue the flight to Israel.
Post #3372 142
🚨 Pentagon Officially Announces Withdrawal from Iraq

Senior Pentagon Spokesperson:

🔹 Today, the United States and our coalition partners—in accordance with the September 2024 joint statement between the U.S. and Iraq, as well as U.S. national interests—have officially concluded "Operation Inherent Resolve" in Iraq.
Post #3371 133
PPHM HACKER NEWS 🚨 The media of Israel, quoting informed sources, revealed that Benjamin Netanyahu, during his secret trip to the UAE and meeting with Mohammed bin Zayed, asked him to deny the Haaretz newspaper's report about the explicit warning before the October 7, 2023…
🚨 All about the secret meeting between Netanyahu and the UAE President; new intelligence on Iran's nuclear activities

🔹 A meeting never intended for public disclosure came to light due to the Iran dossier; in Abu Dhabi, Netanyahu presented Israel's latest intelligence regarding Iran's nuclear program to the UAE President and warned of upcoming security developments in the region.
Post #3370 130
PPHM HACKER NEWS 🚨 Israel's Channel 12 on the Flydubai Boeing 737: A number of Israelis are on board the flight. 🔺 The aircraft is no longer appearing on the flight tracking app Flightradar.
🚨 Flights at Ben Gurion Airport have been suspended.

🔺 A Flydubai flight en route from Dubai to Israel has landed at Tabuk Airport in Saudi Arabia.

🔺 Israeli media report that the request for assistance was prompted by an altercation and fight among passengers on board.
Post #3369 140
PPHM HACKER NEWS 🚨 Israel Channel 12: Israeli authorities have lost contact with a Boeing 737 Fly Dubai and Israel is investigating the possibility of hijacking this plane. 🔺 Israeli Air Force fighters have flown to intercept this plane.
🚨 Israel's Channel 12 on the Flydubai Boeing 737: A number of Israelis are on board the flight.

🔺 The aircraft is no longer appearing on the flight tracking app Flightradar.
Post #3368 150
PPHM HACKER NEWS 🚨 A Flydubai Boeing 737 passenger plane, which was flying from Dubai to Tel Aviv, after briefly transmitting the emergency code 7700 and then the code 7500 related to the possibility of hijacking, is now returning and changing its route to Dubai.
🚨 Israel Channel 12: Israeli authorities have lost contact with a Boeing 737 Fly Dubai and Israel is investigating the possibility of hijacking this plane.

🔺 Israeli Air Force fighters have flown to intercept this plane
.
Post #3367 190
🚨 A Flydubai Boeing 737 passenger plane, which was flying from Dubai to Tel Aviv, after briefly transmitting the emergency code 7700 and then the code 7500 related to the possibility of hijacking, is now returning and changing its route to Dubai.
Post #3366 602
🔴 Leak of Argentine Police Database 'EDDI-Capacitaciones'

A threat actor operating under the alias "zfo$" has posted a claim on an underground forum alleging the theft and extraction of databases from the EDDI-Capacitaciones system, a platform used by Argentine law enforcement. The post, dated September 29, 2026, asserts that the leaked data spans records from 2022 to 2026 and contains sensitive information related to police complaints, administrative procedures, and internal case management.

According to the listing, the compromised database includes extensive personally identifiable information (PII) and operational details. The actor enumerates specific data fields exposed in the dump, which include:

- Full names, document numbers (DNI/CUIL), and dates of birth for individuals involved in cases.
- Contact details such as phone numbers, mobile numbers, and email addresses.
- Detailed residential addresses, including street, number, neighborhood, city, and province.
- Internal case metadata such as case numbers, status codes, assigned officers, and final comments.
- User account information for system administrators or officers, including names, emails, and DNI numbers.

The actor, who identifies as the same individual behind previous aliases "M1sery157" and "zfo," stated that their previous Telegram channels were banned by the group SoulhemTeam. Consequently, the post directs users to a SimpleX channel for the download of the alleged database set.
Post #3365 186
🔴 26M bol.com Customer Records for Sale on Darkweb

A listing on an underground forum alleges the theft of a massive database containing personal and financial data of 26 million customers from bol.com, the Netherlands' largest online marketplace. The hacker, operating under the username 'chara', claims to possess a dataset that includes full names, email addresses, phone numbers, home addresses, and detailed purchase history for users in the Netherlands and Belgium. The actor is offering the data for $500 via cryptocurrency.

According to the sample records provided in the forum post, the leak contains highly sensitive Personally Identifiable Information (PII) and financial metadata. The exposed fields include:

- Full names, email addresses, and phone numbers
- Complete residential addresses including street names, house numbers, and postal codes
- Account creation dates and last login timestamps
- Order history details such as total spent, recent order IDs, categories, and payment methods (e.g., iDEAL, Creditcard)
- Delivery information including carriers and delivery types

🔺 bol.com is a major e-commerce platform in Europe, serving millions of customers across the Benelux region. The company is part of the Bol Group, which also operates in Germany and other European markets. A breach of this magnitude would expose customers to significant risks of targeted phishing, identity theft, and physical security threats due to the inclusion of home addresses.
Post #3364 147
Stolen Sessions Turn Generative Platforms Into Corporate Breach Gateways

Information-stealing malware is increasingly harvesting corporate AI credentials, active sessions and API keys, creating a new route into sensitive business data and expensive computing resources.

🔗 Read More
Post #3363 118
🔴 Domain Admin Access to Australian Insurance Company Advertised

Access to an Australian insurance company is being advertised on a forum.

The post claims the seller has Exchange OWA access with Domain Admin privileges. Sophos Endpoint is listed as the organization’s security product.

According to the listing, the company has estimated annual revenue between $100 million and $250 million and a network of roughly 100 hosts.

The asking price for the access is $1,380.

These claims have not been independently verified.
Post #3362 111
🔴 Fake iPhone Duo preorder scam triggers DarkSword attack

Apple announced its first foldable iPhone on September 9, and scammers were ready to ‘deliver’ one before anyone could buy it.

Most of what we found around the launch of the iPhone Duo and iPhone 18 Pro was familiar fraud.

But one fake preorder page was different.

Behind its Apple-style design and $500 voucher, the page uses the leaked DarkSword exploit chain to try to break into vulnerable iPhones. If it succeeds, a separate payload attempts to steal saved credentials, cryptocurrency wallet data, and notes.

You don’t have to fill in the form, tap a download, or approve anything. Opening the page is enough to start the attempt.
Post #3361 97
🔴 Daemon Tools Hackers’ NeedyMantis Malware Dissected by Microsoft

Microsoft has analyzed a malware framework used by a China-based threat actor in attacks against telecommunications and governmental organizations.

Dubbed NeedyMantis, the framework was discovered during the follow-on analysis of indicators of compromise (IoCs) associated with the May 2026 Daemon Tools supply chain attack.

Thousands of computers were infected through poisoned Daemon Tools iterations distributed through the official website, and a backdoor was deployed on roughly a dozen of them. Government, scientific, manufacturing, and retail organizations in Belarus, Russia, and Thailand were hit.
Post #3360 86
🔴 Two Delaware men sentenced to a combined 189 months for international cyber intrusion scheme

Chijioke Timothy Odimegwu, 25, and Harafat Mogaji, 26, used phishing campaigns to steal employee email credentials and redirect business payments, according to the Justice Department.

Both men were members of the U.S. Air Force at the time of the scheme.
⠀
The actors and their co-conspirators diverted a $1.68 million payment from an Iowa City victim and more than $720,000 from an Ohio victim.

They also harvested financial account information, PINs and payment card details to conduct unauthorized transactions.
⠀
Odimegwu received 111 months in prison and was ordered to pay $366,617.59 in restitution.

Mogaji received 78 months and was ordered to pay $995,680.45.
Post #3359 363
🔴 Humans are reviewing Copilot users’ bizarre and abusive image-editing requests

A reminder for anyone who thinks their AI chats are private: A human may see what they upload. A report from 404 Media this week describes contractors reviewing Copilot users’ photos, editing requests, and the images Copilot produces. Some of what they see is disturbing.

The third-party companies hired to conduct these reviews present their workers with an original photo and a user’s request for an edit. They are also shown two potential AI edits and asked to judge each on technical merit. Because this is the internet, this goes well beyond requests to put your cat in a Halloween costume. Many of the requests are sexual in nature and some involve children, the report said. The faces in the original photos are not censored, meaning reviewers can see who the subjects are.
Post #3358 99
🔴 Kiteworks patches critical flaw, brings customer systems online

American tech company Kiteworks has lifted a precautionary advisory asking customers to shut down systems after patching a critical vulnerability.

Formerly known as Accellion, it operates a Private Content Network (PCN) that integrates enterprise email, file sharing, Managed File Transfer (MFT), APIs, and web forms into a single platform.

Kiteworks provides services to thousands of global corporations and government agencies, and its Private Data Network has over 100 million end-users.
Post #3357 100
🔴 They stole two Nvidia trucks believing they contained valuable GPUs, but found themselves with 10 tons of sand

It's no secret that GPUs are worth their weight in gold these days. Furthermore, with the ongoing RAM crisis driving prices skyrocketing, GPUs have become both rare and incredibly expensive. That's probably what some thieves thought, too. They stole two Nvidia-branded trailers, thinking they were getting a shipment of expensive GPUs. But they ended up with nothing (10 tons of sand).

According to Wired, thieves stole two trailers bearing Nvidia and PlusAI logos in Newark, California, last week, but instead of expensive hardware, they were each loaded with 20,000 pounds of sand. It's unusual for a tech company to load a trailer, but Nvidia and PlusAI have teamed up to test autonomous trucks and trailers filled with sand to simulate heavy loads.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →