Post #51
2.28K
Channel Public Channel
 P.
- Subscribers
- 1.12K
- Photos
- 3
- Videos
- 1
- Links
- 48
Showing posts older than #52 · Back to latest
Older Posts 20 shown

Post #50
2.49K
lazyParam
A simple automation tool with the implementation of multi-threading to check for hidden parameters. This tool is still in testing phase and more implementations are soon to be made. note: Works with python3
Features:
▫️ Fuzz parameters for both GET and POST method
▫️ Multi-threaded (Default: 4)
▫️ Use intensive mode with characters bypassing techniques (beta)
▫️ Check for LFI, RCE and SSTI
https://github.com/aniqfakhrul/lazyParam
@pfk_0day
GitHub GitHub - aniqfakhrul/lazyParam: A simple automation tool to detect lfi, rce and ssti vulnerability A simple automation tool to detect lfi, rce and ssti vulnerability - aniqfakhrul/lazyParam A simple automation tool with the implementation of multi-threading to check for hidden parameters. This tool is still in testing phase and more implementations are soon to be made. note: Works with python3
Features:
▫️ Fuzz parameters for both GET and POST method
▫️ Multi-threaded (Default: 4)
▫️ Use intensive mode with characters bypassing techniques (beta)
▫️ Check for LFI, RCE and SSTI
https://github.com/aniqfakhrul/lazyParam
@pfk_0day
- ❤ 2
- 👎 1
Post #49
1.89K
ExportDumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
https://github.com/iilegacyyii/ExportDumper
@Pfk_0day
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
https://github.com/iilegacyyii/ExportDumper
@Pfk_0day

Post #48
1.88K
W0wS3cur1tyEDR
Project for people who want to know more about edr's.
W0wS3cur1tyEDR consists from 2 projects :
▫️ W0wS3cur1ty, which is the dll file that will get injected to a target process
▫️ WSEdr, the enjector that will inject W0wS3cur1ty.dll into the target process
the dll file, create a new console, and write data to it, it hooks (using minhook library):
▫️ NtCreateThreadEx
▫️ NtWriteVirtualMemory
▫️ NtAllocateVirtualMemory
▫️ NtProtectVirtualMemory
NtProtectVirtualMemory hook can even dump the RWX sections
i added a 'payload.dll' file that can be used as a test, it runs all the 4 hooked api's and can be injected automatically by the juicy edr, it runs metasploit's calc shellcode so it may be detected by your av before the demo...
https://github.com/ORCx41/W0wS3cur1tyEDR
#edr
@pfk_0day
- 👍 3
Post #47
1.61K
Pitraix
Modern Cross-Platform HTTP-Based P2P Botnet over #TOR that cannot be traced.
Design is based off "zero-trust" even malicious peers cannot do any damage while protecting operator identity. for more techincal information check spec.txt
Pitraix is able to handle millions of hosts, the limit is TOR network capacity
You can run Pitraix on a toaster and it will still work just as good with said millions of hosts, as the operative is one who sending requests, not recieving it and because there is no #C2.
https://github.com/ThrillQuks/Pitraix
@pfk_0Day
Post #46
1.51K
EDRSandBlast
EDRSandBlast is a tool written in C that weaponize a vulnerable signed driver to bypass EDR detections (Kernel callbacks and ETW TI provider) and LSASS protections. Multiple userland unhooking techniques are also implemented to evade userland monitoring.
As of release, combination of userland (--usermode) and Kernel-land (--kernelmode) techniques were used to dump LSASS memory under EDR scrutiny, without being blocked nor generating "OS Credential Dumping"-related events in the product (cloud) console. The tests were performed on 3 distinct EDR products and were successful in each case.
https://github.com/wavestone-cdt/EDRSandblast/tree/DefCon30Release
@pfk_0day

- 👍 1
Post #44
1.68K
secureCodeBox
A kubernetes based, modularized toolchain for continuous security scans of your software project. Its goal is to orchestrate and easily automate a bunch of security-testing tools out of the box.
https://github.com/secureCodeBox/secureCodeBox
@pfk_0day
A kubernetes based, modularized toolchain for continuous security scans of your software project. Its goal is to orchestrate and easily automate a bunch of security-testing tools out of the box.
https://github.com/secureCodeBox/secureCodeBox
@pfk_0day

- 👍 2
Post #43
1.55K
WpCrack Tool
A tool used to force login into the WordPress CMS web application and is built in the Python programming language.
Features:
▫️ Very fast login
▫️ Use of HTTP proxies
▫️ Multithreading or Multiprocessor
https://github.com/22XploiterCrew-Team/WpCrack
@pfk_0day
A tool used to force login into the WordPress CMS web application and is built in the Python programming language.
Features:
▫️ Very fast login
▫️ Use of HTTP proxies
▫️ Multithreading or Multiprocessor
https://github.com/22XploiterCrew-Team/WpCrack
@pfk_0day
- ❤ 1
Post #42
1.27K
Matos
An open-source cloud security tool for analyzing multi-cloud infrastructure security.
▫️ Discover cloud assets (e.g. virtual machines, storage, databases, disks, and containers), and gather configuration and metadata of all the assets in the cloud environment.
▫️ Assess the configurations of your cloud assets to help identify misconfiguration, non-conformance to best practices and compliance standards.
▫️ Provides out-of-the-box Ansible scripts to remediate problems efficiently.
▫️ Support multi-cloud environment - Amazon Web Services (AWS), Google Cloud Platform (GCP) and Microsoft Azure cloud service providers.
https://github.com/cloudmatos/Matos
@pfk_0day
GitHub GitHub - cloudmatos/matos: Matos is an open-source cloud security tool for analyzing multi-cloud infrastructure security. Matos is an open-source cloud security tool for analyzing multi-cloud infrastructure security. - cloudmatos/matos An open-source cloud security tool for analyzing multi-cloud infrastructure security.
▫️ Discover cloud assets (e.g. virtual machines, storage, databases, disks, and containers), and gather configuration and metadata of all the assets in the cloud environment.
▫️ Assess the configurations of your cloud assets to help identify misconfiguration, non-conformance to best practices and compliance standards.
▫️ Provides out-of-the-box Ansible scripts to remediate problems efficiently.
▫️ Support multi-cloud environment - Amazon Web Services (AWS), Google Cloud Platform (GCP) and Microsoft Azure cloud service providers.
https://github.com/cloudmatos/Matos
@pfk_0day
Post #41
1.11K
ScanReflectedXSS - Nuclei
This script allows to find XSS vulnerabilities with nuclei, taking advantage of this resource in its maximum analysis capacity.
In the community I have not seen XSS Fuzzing with nuclei in general, only focused on exploitations by CVE
https://github.com/HernanRodriguez1/ScanReflectedXSS
@pfk_0day
This script allows to find XSS vulnerabilities with nuclei, taking advantage of this resource in its maximum analysis capacity.
In the community I have not seen XSS Fuzzing with nuclei in general, only focused on exploitations by CVE
https://github.com/HernanRodriguez1/ScanReflectedXSS
@pfk_0day

- 🔥 2
Post #40
1.1K
Save the Environment
Many applications appear to rely on Environment Variables such as %SYSTEMROOT% to load DLLs from protected locations.
By changing these variables on process level, it is possible to let a legitimate program load arbitrary DLLs.
https://github.com/wietze/windows-dll-env-hijacking
Research:
https://www.wietzebeukema.nl/blog/save-the-environment-variables
#maldev #dll #hijacking #environment
@pfk_0day
GitHub GitHub - wietze/windows-dll-env-hijacking: Project for identifying executables and DLLs vulnerable to environment-variable based… Project for identifying executables and DLLs vulnerable to environment-variable based DLL hijacking. - wietze/windows-dll-env-hijacking Many applications appear to rely on Environment Variables such as %SYSTEMROOT% to load DLLs from protected locations.
By changing these variables on process level, it is possible to let a legitimate program load arbitrary DLLs.
https://github.com/wietze/windows-dll-env-hijacking
Research:
https://www.wietzebeukema.nl/blog/save-the-environment-variables
#maldev #dll #hijacking #environment
@pfk_0day
Post #39
1.11K
DoLTEst
A negative testing framework to uncover the non-standard-compliant behaviors in LTE implementations of end-user devices.
Despite numerous implementation vulnerabilities reported, a lack of negative testing in specification still leaves other implementation vulnerabilities unchecked.
It is an abbreviation for "Downlink LTE Test" or "(Let's) Do LTE Test" 😉.
https://github.com/SysSec-KAIST/DoLTEst
@pfk_0day
GitHub GitHub - SysSec-KAIST/DoLTEst: A negative testing framework, DoLTEst, for finding non-standard-compliant bugs in LTE protocol implementations… A negative testing framework, DoLTEst, for finding non-standard-compliant bugs in LTE protocol implementations of UEs - SysSec-KAIST/DoLTEst A negative testing framework to uncover the non-standard-compliant behaviors in LTE implementations of end-user devices.
Despite numerous implementation vulnerabilities reported, a lack of negative testing in specification still leaves other implementation vulnerabilities unchecked.
It is an abbreviation for "Downlink LTE Test" or "(Let's) Do LTE Test" 😉.
https://github.com/SysSec-KAIST/DoLTEst
@pfk_0day
- ❤ 1
Post #35
1.92K
❤️🔥Bug Bounty Guide 2022❤️🔥
Bug Bounty is based on finding vulnerabilities in certain software.To claim the bounty, bugs must be original and previously unreported
❇️Bug Bounty Platforms❇️
🍎HackerOne
https://www.hackerone.com
🍎Bugcrowd
https://www.bugcrowd.com
🍎Synack
https://www.synack.com
🍎Detectify
https://cs.detectify.com
🍎Cobalt
https://cobalt.io
🍎Open Bug Bounty
https://www.openbugbounty.org
🍎Zero Copter
https://www.zerocopter.com
🍎Yes We Hack
https://www.yeswehack.com
🍎Hacken Proof
https://hackenproof.com
🍎Vulnerability Lab
https://www.vulnerability-lab.com
🍎Fire Bounty
https://firebounty.com
🍎Bug Bounty
https://bugbounty.jp/
🍎Anti Hack
https://antihack.me
🍎Intigrity
https://intigrity.com/
🍎Safe Hats
https://safehats.com
🍎Red Storm
https://www.redstorm.io/
🍎Cyber Army
https://www.cyberarmy.id
🍎Yogosha
https://yogosha.com
#bugbounty
@Pfk_0Day
HackerOne HackerOne | Leader in Continuous Threat Exposure Management | Security for AI HackerOne combines AI with the ingenuity of the largest community of security researchers to find and fix security, privacy, and AI vulnerabilities across the SDLC. HackerOne offers AI red teaming, crowdsourced security, bug bounty, vulnerability disclosure… Bug Bounty is based on finding vulnerabilities in certain software.To claim the bounty, bugs must be original and previously unreported
❇️Bug Bounty Platforms❇️
🍎HackerOne
https://www.hackerone.com
🍎Bugcrowd
https://www.bugcrowd.com
🍎Synack
https://www.synack.com
🍎Detectify
https://cs.detectify.com
🍎Cobalt
https://cobalt.io
🍎Open Bug Bounty
https://www.openbugbounty.org
🍎Zero Copter
https://www.zerocopter.com
🍎Yes We Hack
https://www.yeswehack.com
🍎Hacken Proof
https://hackenproof.com
🍎Vulnerability Lab
https://www.vulnerability-lab.com
🍎Fire Bounty
https://firebounty.com
🍎Bug Bounty
https://bugbounty.jp/
🍎Anti Hack
https://antihack.me
🍎Intigrity
https://intigrity.com/
🍎Safe Hats
https://safehats.com
🍎Red Storm
https://www.redstorm.io/
🍎Cyber Army
https://www.cyberarmy.id
🍎Yogosha
https://yogosha.com
#bugbounty
@Pfk_0Day
- 👍 4
Post #34
1.56K
SharpEfsPotato
Local privilege escalation from SeImpersonatePrivilege using EfsRpc.
https://github.com/bugch3ck/SharpEfsPotato
#windows #lpe #dotnet #SeImpersonatePrivilege #EfsRpc
@Pfk_0Day
Local privilege escalation from SeImpersonatePrivilege using EfsRpc.
https://github.com/bugch3ck/SharpEfsPotato
#windows #lpe #dotnet #SeImpersonatePrivilege #EfsRpc
@Pfk_0Day

- 👍 3
Post #32
1.71K
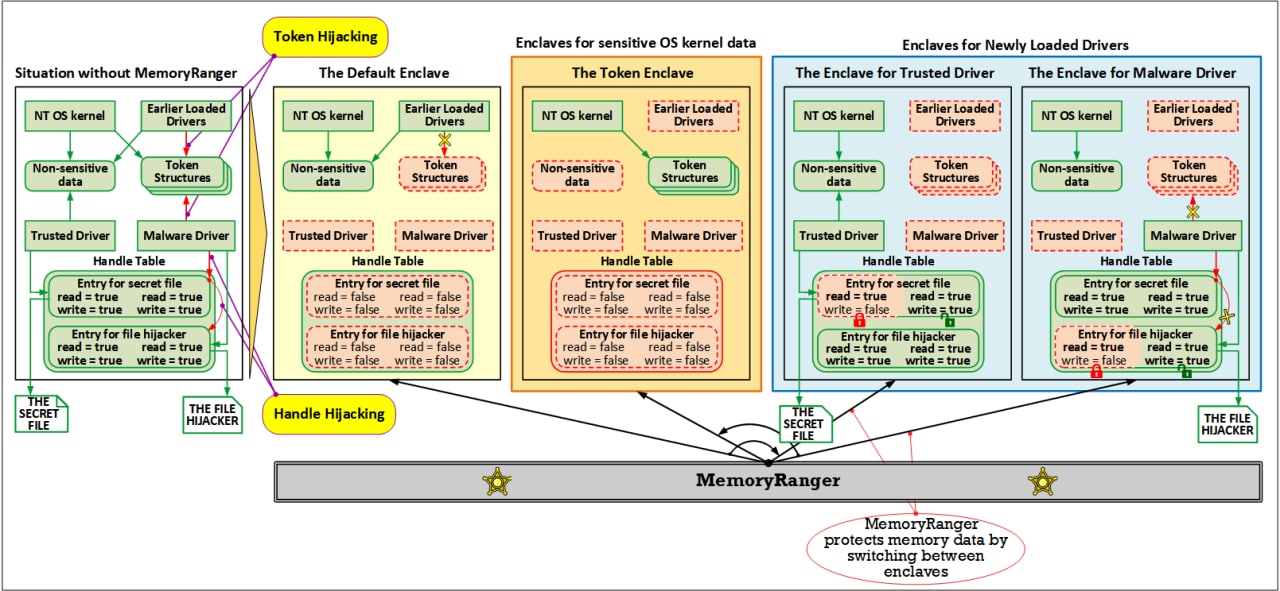
MemoryRanger
Updated MemoryRanger: Hijacking Is Not An Option
Blasting Event-Driven Cornucopia: WMI-based User-Space Attacks Blind SIEMs and EDRs
MemoryRanger protects kernel data and code by running drivers and hosting data in isolated kernel enclaves using VT-x/EPT features:
▫️ Hijacking of NTFS structures gains an unauthorized access to files opened without shared access by patching Stream Control Block structures;
▫️ Handle Hijacking Attack provides illegal access to exclusively open files via patching handle table entries;
▫️ Token Hijacking Attack is designed to elevate the process privileges without using token-swapping technique;
https://github.com/IgorKorkin/MemoryRanger
@Pfk_0Day
Post #31
1.32K
Forwarded from PFK Git [ international ]
DirtyCred
Linux Kernel Exploitation: write DirtyPipe exploit that works on different kernels and ARCHs without code changes.
https://github.com/Markakd/DirtyCred
@PfkGit
Linux Kernel Exploitation: write DirtyPipe exploit that works on different kernels and ARCHs without code changes.
https://github.com/Markakd/DirtyCred
@PfkGit

Post #30
1.29K

Post #27
1.3K
OffensiveVBA
In preparation for a VBS AV Evasion Stream/Video I was doing some research for Office Macro code execution methods and evasion techniques.
The list got longer and longer and I found no central place for offensive VBA templates - so this repo can be used for such. It is very far away from being complete. If you know any other cool technique or useful template feel free to contribute and create a pull request!
Most of the templates in this repo were already published somewhere. I just copy pasted most templates from ms-docs sites, blog posts or from other tools.
https://github.com/S3cur3Th1sSh1t/OffensiveVBA
@Pfk_0Day
GitHub GitHub - S3cur3Th1sSh1t/OffensiveVBA: This repo covers some code execution and AV Evasion methods for Macros in Office documents This repo covers some code execution and AV Evasion methods for Macros in Office documents - S3cur3Th1sSh1t/OffensiveVBA In preparation for a VBS AV Evasion Stream/Video I was doing some research for Office Macro code execution methods and evasion techniques.
The list got longer and longer and I found no central place for offensive VBA templates - so this repo can be used for such. It is very far away from being complete. If you know any other cool technique or useful template feel free to contribute and create a pull request!
Most of the templates in this repo were already published somewhere. I just copy pasted most templates from ms-docs sites, blog posts or from other tools.
https://github.com/S3cur3Th1sSh1t/OffensiveVBA
@Pfk_0Day
- 👍 3
Post #26
1.08K
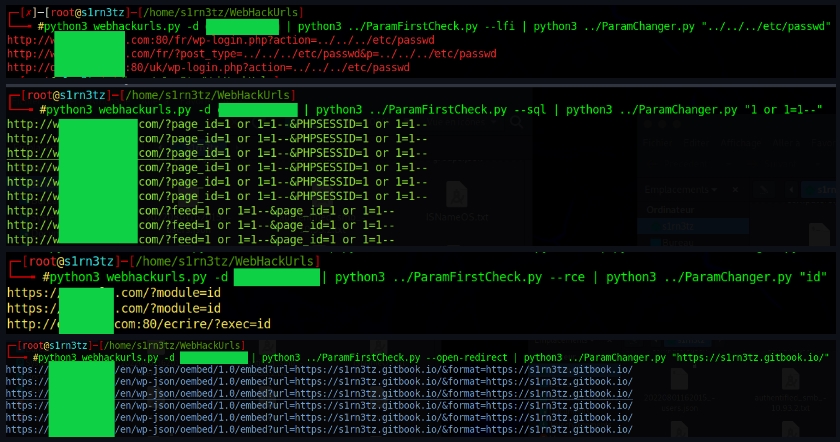
ParamChanger
A tool allowing you to replace the parameters of a list of urls by a payload entered as an argument.
https://github.com/mathis2001/ParamChanger
@Pfk_0day
A tool allowing you to replace the parameters of a list of urls by a payload entered as an argument.
https://github.com/mathis2001/ParamChanger
@Pfk_0day
- 👍 1
Post #25
1.04K
LibAFL
A Framework for Modular and Reusable Fuzzers
The fuzzers/ folder contains the variants created for the paper and fuzzers/LibAFL contains the code of LibAFL. The neodiff folder contains the NeoDiff code with the libafl-based implementation. The fuzzbench/ folder contains a snapsot of the fuzzbench repository used in the evaluations with all the variants. Each dockerfile must be adapted by hand to point to a git repository serving the fuzzers/ folder as repository. The original links were removed for the double blind.
https://github.com/AFLplusplus/libafl_paper_artifacts
Individual experiments can then be runned using the local experiments: https://google.github.io/fuzzbench/running-a-local-experiment
@Pfk_0Day