

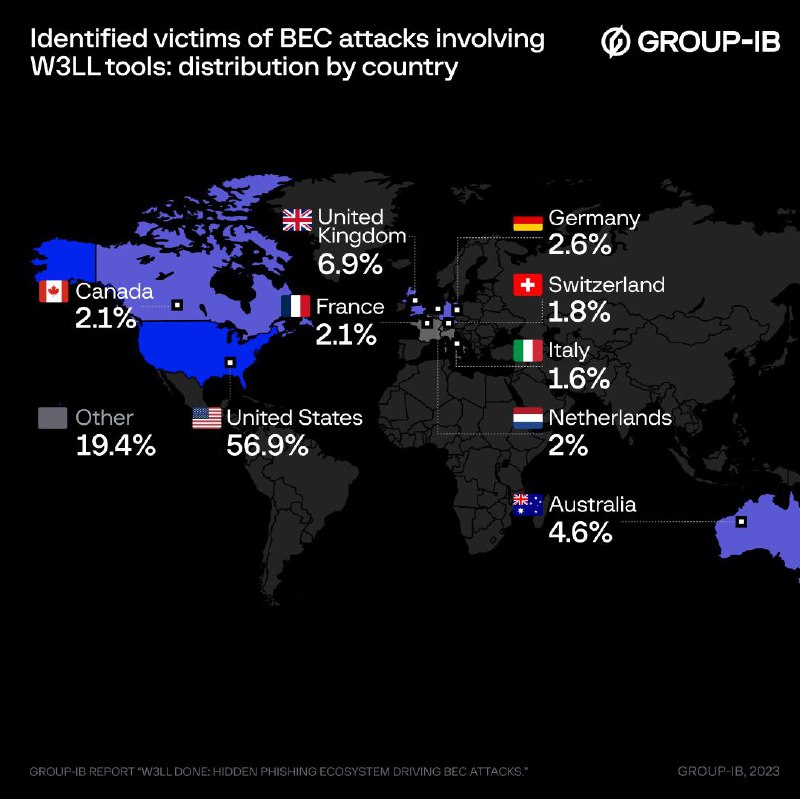
W3LL oiled machine: Group-IB uncovers covert BEC phishing empire targeting Microsoft 365
Group-IB’s newest threat report is now live! Meet W3LL — a threat actor behind a phishing empire that has remained largely unknown until now.
What’s inside the report?
📌W3LL’s history since 2017
📌Examination of W3LL Store, a hidden underground market that serves a closed community of threat actors
📌Analysis of W3LL’s major weapon, W3LL Panel, one of the most advanced phishing kits in its class, along with a rundown of the threat actor’s 16 other fully customized tools for BEC attacks
📌W3LL Store’s estimated turnover for the last 10 months amounted to at least $500,000
Download the report “W3LL done: Hidden Phishing Ecosystem Driving BEC Attacks” for more insights into W3LL’s business, a list of Indicators of Compromise as well as YARA rules that can be used to hunt and detect W3LL Panel phishing pages.
#FightAgainstCybercrime #Phishing #W3LL
Post #227
1.95K