Post #919
66
Channel Public Channel
 AL
Alaid TechThread
@offensive_thread
Vulnerability discovery, threat intelligence, reverse engineering, AppSec
- Subscribers
- 1.14K
- Photos
- 7
- Videos
- 2
- Links
- 1.4K
Showing posts older than #920 · Back to latest
Older Posts 20 shown
Post #918
74
Securing Active Directory: Performing an Active Directory Security Review
https://www.hub.trimarcsecurity.com/post/securing-active-directory-performing-an-active-directory-security-review
Trimarc Content Hub Securing Active Directory: Performing an Active Directory Security Review During the Trimarc Webcast on June 17, 2020, Sean Metcalf covered a number of Active Directory (AD) components and areas that should be reviewed for potential security issues. The presentation included PowerShell code in the presentation and that code is… https://www.hub.trimarcsecurity.com/post/securing-active-directory-performing-an-active-directory-security-review
Post #917
61

Post #916
50
Exploiting Bitdefender Antivirus: RCE from any website
https://palant.info/2020/06/22/exploiting-bitdefender-antivirus-rce-from-any-website/
https://palant.info/2020/06/22/exploiting-bitdefender-antivirus-rce-from-any-website/

Post #915
46
Post #914
46
CVE-2020-1170. Microsoft Windows Defender Elevation of Privilege
https://itm4n.github.io/cve-2020-1170-windows-defender-eop/
itm4n’s blog CVE-2020-1170 - Microsoft Windows Defender Elevation of Privilege Vulnerability Here is my writeup about CVE-2020-1170, an elevation of privilege bug in Windows Defender. Finding a vulnerability in a security-oriented product is quite satisfying. Though, there was nothing groundbreaking. It’s quite the opposite actually and I’m surprised… https://itm4n.github.io/cve-2020-1170-windows-defender-eop/
Post #913
45
Post #912
45
List of Microsoft-signed files with functionality that would be useful for attacks
https://lolbas-project.github.io
https://lolbas-project.github.io
Post #911
50
Further Evasion in the Forgotten Corners of MS-XLS
https://malware.pizza/2020/06/19/further-evasion-in-the-forgotten-corners-of-ms-xls/
https://malware.pizza/2020/06/19/further-evasion-in-the-forgotten-corners-of-ms-xls/

Post #910
46
SMBleedingGhost Writeup Part II: Unauthenticated Memory Read – Preparing the Ground for an RCE
https://blog.zecops.com/vulnerabilities/smbleedingghost-writeup-part-ii-unauthenticated-memory-read-preparing-the-ground-for-an-rce/
Jamf Jamf Threat Labs | Blog https://blog.zecops.com/vulnerabilities/smbleedingghost-writeup-part-ii-unauthenticated-memory-read-preparing-the-ground-for-an-rce/
Post #909
65
Attacking FreeIPA — Part IV: CVE-2020–10747
https://posts.specterops.io/attacking-freeipa-part-iv-cve-2020-10747-7c373a1bf66b
https://posts.specterops.io/attacking-freeipa-part-iv-cve-2020-10747-7c373a1bf66b

Post #908
58
ntlm_theft: A file payload generator for forced ntlm hash disclosure
https://medium.com/greenwolf-security/ntlm-theft-a-file-payload-generator-for-forced-ntlm-hash-disclosure-2d5f1fe5b964
https://medium.com/greenwolf-security/ntlm-theft-a-file-payload-generator-for-forced-ntlm-hash-disclosure-2d5f1fe5b964

Post #907
49
SMBleedingGhost Writeup: Chaining SMBleed (CVE-2020-1206) with SMBGhost
https://blog.zecops.com/vulnerabilities/smbleedingghost-writeup-chaining-smbleed-cve-2020-1206-with-smbghost/
Jamf Jamf Threat Labs | Blog https://blog.zecops.com/vulnerabilities/smbleedingghost-writeup-chaining-smbleed-cve-2020-1206-with-smbghost/
Post #906
61
CVE-2020-1301 | Windows SMB Remote Code Execution Vulnerability
- all Windows versions affected
https://portal.msrc.microsoft.com/en-US/security-guidance/advisory/CVE-2020-1301
- all Windows versions affected
https://portal.msrc.microsoft.com/en-US/security-guidance/advisory/CVE-2020-1301
Post #905
56
Abusing Windows telemetry for persistence
https://www.trustedsec.com/blog/abusing-windows-telemetry-for-persistence/
https://www.trustedsec.com/blog/abusing-windows-telemetry-for-persistence/

Post #904
61
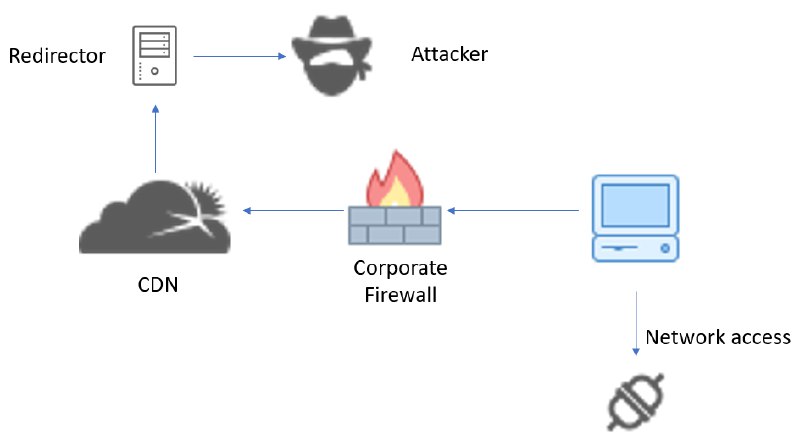
Red Team: Using SharpChisel to exfil internal network
https://medium.com/@shantanukhande/red-team-using-sharpchisel-to-exfil-internal-network-e1b07ed9b49
https://medium.com/@shantanukhande/red-team-using-sharpchisel-to-exfil-internal-network-e1b07ed9b49
Post #903
47
Automating the provisioning of Active Directory labs in Azure
https://blog.christophetd.fr/automating-the-provisioning-of-active-directory-labs-in-azure/
https://blog.christophetd.fr/automating-the-provisioning-of-active-directory-labs-in-azure/

Post #902
54
PoC exploiting Aligned Chunk Confusion on Windows kernel Segment Heap
https://github.com/synacktiv/Windows-kernel-SegmentHeap-Aligned-Chunk-Confusion
https://github.com/synacktiv/Windows-kernel-SegmentHeap-Aligned-Chunk-Confusion

Post #901
47
Post #900
48
Apache Tomcat RCE by deserialization (CVE-2020-9484) – write-up and exploit
https://www.redtimmy.com/java-hacking/apache-tomcat-rce-by-deserialization-cve-2020-9484-write-up-and-exploit/
https://www.redtimmy.com/java-hacking/apache-tomcat-rce-by-deserialization-cve-2020-9484-write-up-and-exploit/