Post #598
41
Channel Public Channel
 AL
Alaid TechThread
@offensive_thread
Vulnerability discovery, threat intelligence, reverse engineering, AppSec
- Subscribers
- 1.14K
- Photos
- 7
- Videos
- 2
- Links
- 1.4K
Showing posts older than #599 · Back to latest
Older Posts 20 shown
Post #597
56
How I Hacked the Microsoft Outlook Android App and Found CVE-2019-1105
https://www.f5.com/labs/articles/threat-intelligence/how-i-hacked-the-microsoft-outlook-android-app-and-found-cve-2019-1105#.XRCqdjj5OfA.twitter
https://www.f5.com/labs/articles/threat-intelligence/how-i-hacked-the-microsoft-outlook-android-app-and-found-cve-2019-1105#.XRCqdjj5OfA.twitter

Post #596
53
Реализация файловой системы поверх системных артефактов (Windows и macOS)
https://github.com/SafeBreach-Labs/AltFS
GitHub GitHub - SafeBreach-Labs/AltFS: The Alternative Fileless File System The Alternative Fileless File System. Contribute to SafeBreach-Labs/AltFS development by creating an account on GitHub. https://github.com/SafeBreach-Labs/AltFS
Post #595
61

Post #594
62

Post #593
57
AESDDoS Botnet Malware Infiltrates Containers via Exposed Docker APIs
https://blog.trendmicro.com/trendlabs-security-intelligence/aesddos-botnet-malware-infiltrates-containers-via-exposed-docker-apis/
https://blog.trendmicro.com/trendlabs-security-intelligence/aesddos-botnet-malware-infiltrates-containers-via-exposed-docker-apis/

Post #592
55
Exploiting CVE-2019-1040 - Combining relay vulnerabilities for RCE and Domain Admin
https://dirkjanm.io/exploiting-CVE-2019-1040-relay-vulnerabilities-for-rce-and-domain-admin/
dirkjanm.io Exploiting CVE-2019-1040 - Combining relay vulnerabilities for RCE and Domain Admin Earlier this week, Microsoft issued patches for CVE-2019-1040, which is a vulnerability that allows for bypassing of NTLM relay mitigations. The vulnerability was discovered by Marina Simakov and Yaron Zinar (as well as several others credited in the Microsoft… https://dirkjanm.io/exploiting-CVE-2019-1040-relay-vulnerabilities-for-rce-and-domain-admin/
Post #591
51
Post #590
46
Digging up the Past: OS X File Versioning
https://versprite.com/blog/security-research/file-versioning-mac-os-x/
https://versprite.com/blog/security-research/file-versioning-mac-os-x/

Forwarded from r0 Crew (Channel)
Heap Overflow Exploitation on Windows 10 Explained https://blog.rapid7.com/2019/06/12/heap-overflow-exploitation-on-windows-10-explained/ #exploitation #dukeBarman
Post #588
36
Post #587
41
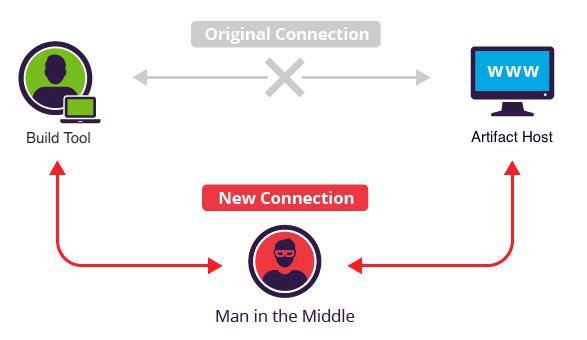
Want to take over the Java ecosystem? All you need is a MITM!
https://medium.com/@jonathan.leitschuh/want-to-take-over-the-java-ecosystem-all-you-need-is-a-mitm-1fc329d898fb
https://medium.com/@jonathan.leitschuh/want-to-take-over-the-java-ecosystem-all-you-need-is-a-mitm-1fc329d898fb
Post #586
36
Bypass XSS filters using JavaScript global variables
https://www.secjuice.com/bypass-xss-filters-using-javascript-global-variables/
https://www.secjuice.com/bypass-xss-filters-using-javascript-global-variables/

Post #585
43
Post #584
60
Post #583
63

Post #582
40
Анализ недавнего 0day в Windows
Another Task Scheduler 0day, Another Task Scheduler Micropatch (The SandboxEscaper Saga)
https://blog.0patch.com/2019/06/another-task-scheduler-0day-another.html
0Patch Another Task Scheduler 0day, Another Task Scheduler Micropatch (The SandboxEscaper Saga) Backward Compatibility is Hard, and so is Stacked Impersonation by Simon Raner and Mitja Kolsek, the 0patch Team [Update 6/12/201... Another Task Scheduler 0day, Another Task Scheduler Micropatch (The SandboxEscaper Saga)
https://blog.0patch.com/2019/06/another-task-scheduler-0day-another.html
Post #581
40
macOS 0-Day Flaw Lets Hackers Bypass Security Features With Synthetic Clicks
https://thehackernews.com/2019/06/macOS-synthetic-click.html
https://thehackernews.com/2019/06/macOS-synthetic-click.html
Post #580
38

Post #579
36
Разбор уязвимости command injection в Nvidia GeForce Experience
https://rhinosecuritylabs.com/application-security/nvidia-rce-cve-2019-5678/
https://rhinosecuritylabs.com/application-security/nvidia-rce-cve-2019-5678/
