Post #1286
326
Channel Public Channel
 AL
Alaid TechThread
@offensive_thread
Vulnerability discovery, threat intelligence, reverse engineering, AppSec
- Subscribers
- 1.13K
- Photos
- 7
- Videos
- 2
- Links
- 1.4K
Showing posts older than #1287 · Back to latest
Older Posts 20 shown
Post #1285
142
Fine-Grained Coverage-Based Fuzzing
https://binsec.github.io/assets/publications/slides/2023-tosem.pdf
https://binsec.github.io/assets/publications/slides/2023-tosem.pdf
- 👍 1
Post #1284
151
Forwarded from Т-Образование

Если вы знаете основы информационной безопасности, умеете искать уязвимости в системах и уважаете конфиденциальность — вам определенно может быть интересна эта стажировка 🔒
Три команды — AppSec, DevSecOps и Security Research — готовы взять стажеров на лето на полный рабочий день с возможностью в дальнейшем перейти в штат. Работать можно удаленно или в одном из офисов в России, Беларуси или Казахстане по договоренности с командой.
Отбор будет в два этапа: онлайн-экзамен (плюс анкета) и интервью. Подробности о командах и задачах, ссылки на материалы для подготовки, а также форма для заявки — по ссылке: https://l.tinkoff.ru/information_security2023
- 👍 3
- 🔥 2
- 👎 1
Post #1283
130
OffensiveCon23 - Stacksmashing- Inside Apple’s Lightning: JTAGging the iPhone for Fuzzing and Profit
https://www.youtube.com/watch?v=-nFWcKHIUN4
YouTube OffensiveCon23 - Stacksmashing- Inside Apple’s Lightning: JTAGging the iPhone for Fuzzing and Profit https://www.offensivecon.org/speakers/2023/ghidraninja.html https://www.youtube.com/watch?v=-nFWcKHIUN4
Post #1282
113
OffensiveCon23 - Samuel Groß & Carl Smith - Advancements in JavaScript Engine Fuzzing
https://www.youtube.com/watch?v=Yd9m7e9-pG0
YouTube OffensiveCon23 - Samuel Groß & Carl Smith - Advancements in JavaScript Engine Fuzzing https://www.offensivecon.org/speakers/2023/samuel-gross-and-carl-smith.html https://www.youtube.com/watch?v=Yd9m7e9-pG0
Post #1281
127
- 🔥 1
Post #1280
136
Post #1279
267
s10515-022-00374-6.pdf2 MB
BCGen: a comment generation method for bytecode
Post #1278
116
CustomProcessingUnit:
Reverse Engineering and Customization of Intel Microcode
https://pietroborrello.com/talk/custom-processing-unit-offensivecon/offensivecon_ucode.pdf
https://github.com/pietroborrello/CustomProcessingUnit
Reverse Engineering and Customization of Intel Microcode
https://pietroborrello.com/talk/custom-processing-unit-offensivecon/offensivecon_ucode.pdf
https://github.com/pietroborrello/CustomProcessingUnit
- 🔥 3
- 👍 1
- 👎 1
Post #1277
133
Unearthing Vulnerabilities in the Apple Ecosystem The Art of KidFuzzerV2.0
OffensiveCon 2023
https://github.com/star-sg/Presentations/blob/main/Offensivecon%202023/Unearthing%20Vulnerabilities%20in%20the%20Apple%20Ecosystem%20The%20Art%20of%20KidFuzzerV2.0.pdf
OffensiveCon 2023
https://github.com/star-sg/Presentations/blob/main/Offensivecon%202023/Unearthing%20Vulnerabilities%20in%20the%20Apple%20Ecosystem%20The%20Art%20of%20KidFuzzerV2.0.pdf

- 🔥 1
Post #1276
143
PASTIS For The Win!
PASTIS is an open-source fuzzing framework that aims at combining various software testing techniques within the same workflow to perform collaborative fuzzing, also known as ensemble fuzzing. At the moment it supports Honggfuzz and AFL++ for grey-box fuzzers and TritonDSE for white-box fuzzers.
https://blog.quarkslab.com/pastis-for-the-win.html
Quarkslab PASTIS For The Win! - Quarkslab's blog In this blog post we present PASTIS, a Python framework for ensemble fuzzing, developed at Quarkslab. PASTIS is an open-source fuzzing framework that aims at combining various software testing techniques within the same workflow to perform collaborative fuzzing, also known as ensemble fuzzing. At the moment it supports Honggfuzz and AFL++ for grey-box fuzzers and TritonDSE for white-box fuzzers.
https://blog.quarkslab.com/pastis-for-the-win.html
- 👍 1
- 🔥 1
Post #1275
134
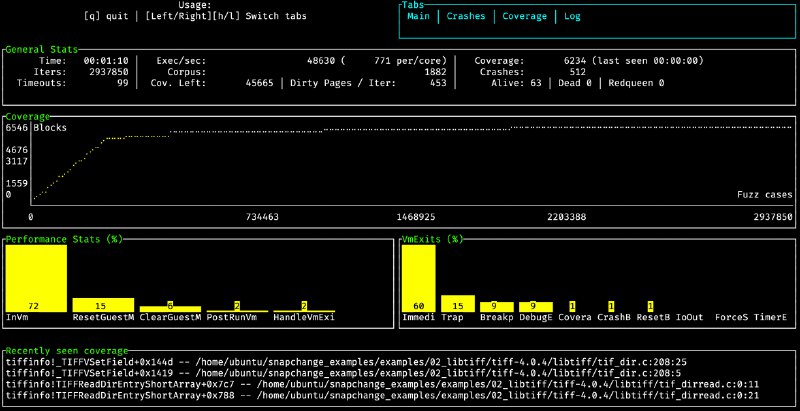
Announcing Snapchange: An Open Source KVM-backed Snapshot Fuzzing Framework
https://aws.amazon.com/blogs/opensource/announcing-snapchange-an-open-source-kvm-backed-snapshot-fuzzing-framework/
https://aws.amazon.com/blogs/opensource/announcing-snapchange-an-open-source-kvm-backed-snapshot-fuzzing-framework/
- 🔥 1
Post #1274
494
Using AI to find software vulnerabilities in XNU
https://www.inulledmyself.com/2023/05/using-ai-to-find-software.html
Inulledmyself Using AI to find software vulnerabilities in XNU Note : This work took place in May-Aug of 2022. It just took me this long to finally finish writing this (Too busy playing with my SRD 😅) L... https://www.inulledmyself.com/2023/05/using-ai-to-find-software.html
Post #1273
151

Post #1272
119
eBPF Observability Tools Are Not Security Tools
https://www.brendangregg.com/blog/2023-04-28/ebpf-security-issues.html
Brendangregg eBPF Observability Tools Are Not Security Tools eBPF Observability Tools Are Not Have Security Tools https://www.brendangregg.com/blog/2023-04-28/ebpf-security-issues.html
Post #1271
129
The Art of Information Disclosure: A Deep Dive into CVE-2022-37985, a Unique Information Disclosure Vulnerability in Windows Graphics Component
https://www.trellix.com/en-us/about/newsroom/stories/research/the-art-of-information-disclosure.html
Trellix Uncovering CVE-2022-37985: A Unique Information Disclosure Vulnerability in Windows Graphics Component Get a comprehensive understanding of CVE-2022-37985, a unique information disclosure vulnerability in Windows Graphics Component. Our blog post covers the technical details of the vulnerability, how it can be exploited, and advice on mitigating the risks. https://www.trellix.com/en-us/about/newsroom/stories/research/the-art-of-information-disclosure.html
Post #1270
122
Microsoft Exchange Powershell Remoting Deserialization leading to RCE (CVE-2023-21707)
https://starlabs.sg/blog/2023/04-microsoft-exchange-powershell-remoting-deserialization-leading-to-rce-cve-2023-21707/
STAR Labs Microsoft Exchange Powershell Remoting Deserialization leading to RCE (CVE-2023-21707) Introduction
While analyzing CVE-2022-41082, also known as ProxyNotShell, we discovered this vulnerability which we have detailed in this blog. However, for a comprehensive understanding, we highly recommend reading the thorough analysis written by team ZDI.… https://starlabs.sg/blog/2023/04-microsoft-exchange-powershell-remoting-deserialization-leading-to-rce-cve-2023-21707/
Post #1269
127
Post #1268
126
Introducing VirusTotal Code Insight: Empowering threat analysis with generative AI
https://blog.virustotal.com/2023/04/introducing-virustotal-code-insight.html
Virustotal Introducing VirusTotal Code Insight: Empowering threat analysis with generative AI At the RSA Conference 2023 today, we are excited to unveil VirusTotal Code Insight, a cutting-edge feature that leverages artificial intelli... https://blog.virustotal.com/2023/04/introducing-virustotal-code-insight.html
- 🔥 1
Post #1267
238
How AI helps keeping Gmail inboxes malware free
https://elie.net/static/files/how-ai-helps-keeping-gmail-inboxes-malware-free/how-ai-helps-keeping-gmail-inboxes-malware-free-slides.pdf
https://elie.net/static/files/how-ai-helps-keeping-gmail-inboxes-malware-free/how-ai-helps-keeping-gmail-inboxes-malware-free-slides.pdf
- 👍 1