Post #1120
94
Channel Public Channel
 AL
Alaid TechThread
@offensive_thread
Vulnerability discovery, threat intelligence, reverse engineering, AppSec
- Subscribers
- 1.14K
- Photos
- 7
- Videos
- 2
- Links
- 1.4K
Showing posts older than #1121 · Back to latest
Older Posts 20 shown
Post #1119
111
Detection Lab
Collection of Packer & Vagrant scripts that quickly bring a Windows AD online, complete with a collection of endpoint security tooling & logging best practices
https://medium.com/@clong/introducing-detection-lab-61db34bed6ae
Collection of Packer & Vagrant scripts that quickly bring a Windows AD online, complete with a collection of endpoint security tooling & logging best practices
https://medium.com/@clong/introducing-detection-lab-61db34bed6ae

Post #1118
96
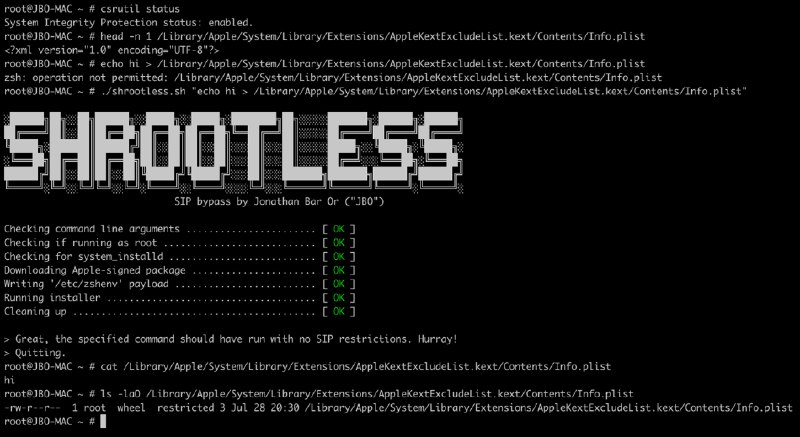
Microsoft finds new macOS vulnerability, Shrootless, that could bypass System Integrity Protection
https://www.microsoft.com/security/blog/2021/10/28/microsoft-finds-new-macos-vulnerability-shrootless-that-could-bypass-system-integrity-protection/
https://www.microsoft.com/security/blog/2021/10/28/microsoft-finds-new-macos-vulnerability-shrootless-that-could-bypass-system-integrity-protection/
Post #1117
103
Monitor creation, deletion and changes to LDAP objects live during your pentest or system administration
https://github.com/p0dalirius/LDAPmonitor
https://github.com/p0dalirius/LDAPmonitor

Post #1116
76
A plugin to introduce a generic API for Decompiler support in GEF
https://github.com/mahaloz/decomp2gef
GitHub GitHub - mahaloz/decomp2dbg: A plugin to introduce interactive symbols into your debugger from your decompiler A plugin to introduce interactive symbols into your debugger from your decompiler - mahaloz/decomp2dbg https://github.com/mahaloz/decomp2gef
Post #1115
68
Skrull is a malware DRM, that prevents Automatic Sample Submission by AV/EDR and Signature Scanning from Kernel. It generates launchers that can run malware on the victim using the Process Ghosting technique. Also, launchers are totally anti-copy and naturally broken when got submitted.
https://github.com/aaaddress1/Skrull
https://github.com/aaaddress1/Skrull

Post #1114
73
A Closer Look at NSA/CISA Kubernetes Hardening Guidance
https://kubernetes.io/blog/2021/10/05/nsa-cisa-kubernetes-hardening-guidance/
Kubernetes A Closer Look at NSA/CISA Kubernetes Hardening Guidance Disclaimer The open source tools listed in this article are to serve as examples only and are in no way a direct recommendation from the Kubernetes community or authors. BackgroundUSA's National Security Agency (NSA) and the Cybersecurity and Infrastructure… https://kubernetes.io/blog/2021/10/05/nsa-cisa-kubernetes-hardening-guidance/
Post #1113
92
Chrome in-the-wild bug analysis: CVE-2021-30632
https://securitylab.github.com/research/in_the_wild_chrome_cve_2021_30632/
https://securitylab.github.com/research/in_the_wild_chrome_cve_2021_30632/
Post #1112
98
Post #1111
83
Do you like to read? I can take over your Kindle with an e-book
https://research.checkpoint.com/2021/i-can-take-over-your-kindle/
https://research.checkpoint.com/2021/i-can-take-over-your-kindle/
Post #1110
87
iOS Wi-Fi Demon: From iOS Format String to Zero-Click RCE
https://ictexpertsluxembourg.lu/technical-corner/ios-wi-fi-demon-from-ios-format-string-to-zero-click-rce/
https://ictexpertsluxembourg.lu/technical-corner/ios-wi-fi-demon-from-ios-format-string-to-zero-click-rce/

Post #1109
72
Use NtCreateProcessEx to spawn a child process, and create the main thread manually.
miniCreateProcessEx
https://github.com/aaaddress1/PR0CESS/tree/main/miniCreateProcessEx
miniCreateProcessEx
https://github.com/aaaddress1/PR0CESS/tree/main/miniCreateProcessEx

Post #1108
73
Now Patched Vulnerability in WhatsApp could have led to data exposure of users
https://research.checkpoint.com/2021/now-patched-vulnerability-in-whatsapp-could-have-led-to-data-exposure-of-users/
https://research.checkpoint.com/2021/now-patched-vulnerability-in-whatsapp-could-have-led-to-data-exposure-of-users/
Post #1107
92
CVE-2021-26084 Remote Code Execution on Confluence Servers
https://github.com/httpvoid/writeups/blob/main/Confluence-RCE.md
https://github.com/httpvoid/writeups/blob/main/Confluence-RCE.md

Post #1106
87
2101.05102.pdf428.5 KB
ProFuzzBench: A Benchmark for Stateful Protocol Fuzzing
Post #1105
83
banks2006.pdf331.4 KB
SNOOZE: Toward a Stateful NetwOrk prOtocol fuzZEr
Post #1104
71
secml-malware: Pentesting Windows Malware Classifiers with Adversarial EXEmples in Python
https://arxiv.org/pdf/2104.12848v2.pdf
https://arxiv.org/pdf/2104.12848v2.pdf
Post #1103
86
corCTF 2021 Fire of Salvation Writeup: Utilizing msg_msg Objects for Arbitrary Read and Arbitrary Write in the Linux Kernel
https://www.willsroot.io/2021/08/corctf-2021-fire-of-salvation-writeup.html?m=1
www.willsroot.io corCTF 2021 Fire of Salvation Writeup: Utilizing msg_msg Objects for Arbitrary Read and Arbitrary Write in the Linux Kernel Vulnerability Research on Low-Level Systems https://www.willsroot.io/2021/08/corctf-2021-fire-of-salvation-writeup.html?m=1
Post #1102
97
FROM PWN2OWN 2021: A NEW ATTACK SURFACE ON MICROSOFT EXCHANGE - PROXYSHELL
https://www.zerodayinitiative.com/blog/2021/8/17/from-pwn2own-2021-a-new-attack-surface-on-microsoft-exchange-proxyshell
Zero Day Initiative Zero Day Initiative — From Pwn2Own 2021: A New Attack Surface on Microsoft Exchange - ProxyShell! In April 2021, Orange Tsai from DEVCORE Research Team demonstrated a remote code execution vulnerability in Microsoft Exchange during the Pwn2Own Vancouver 2021 contest. In doing so, he earned himself $200,000. Since then, he has disclosed several other… https://www.zerodayinitiative.com/blog/2021/8/17/from-pwn2own-2021-a-new-attack-surface-on-microsoft-exchange-proxyshell
Post #1101
84
A Primer On Event Tracing For Windows (ETW)
https://nasbench.medium.com/a-primer-on-event-tracing-for-windows-etw-997725c082bf
https://nasbench.medium.com/a-primer-on-event-tracing-for-windows-etw-997725c082bf
