
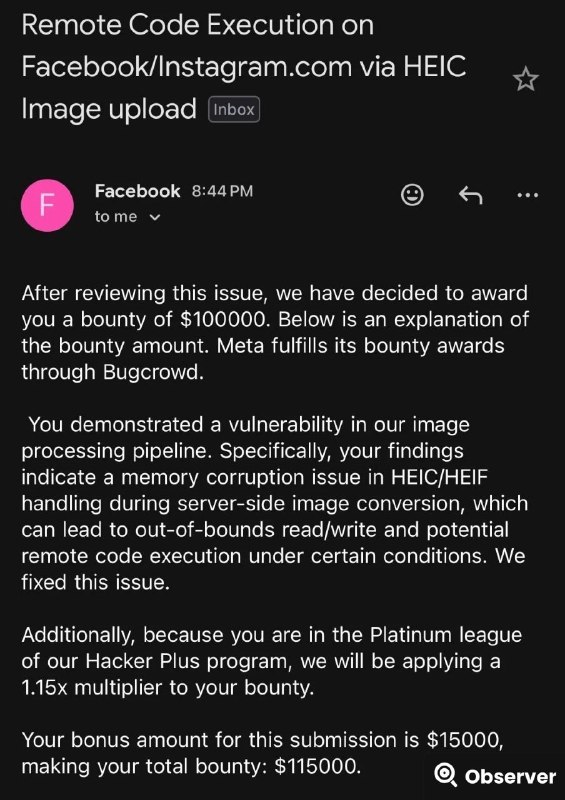
A security researcher was paid a $115,000 bug bounty by Meta after discovering a critical vulnerability in how iOS processes HEIF image files. The attack required no user interaction, just being near a malicious image file was enough to trigger remote code execution on an iPhone. Meta patched it silently before paying out.
One of the largest iOS bug bounties ever paid through a third-party report. 👇
🎰 @Shuffle #1 VIP Crypto Casino & Sportsbook Shuffle.com
🔔 @Observer • 💬 Join community • 🎁 Weekly Giveaway