
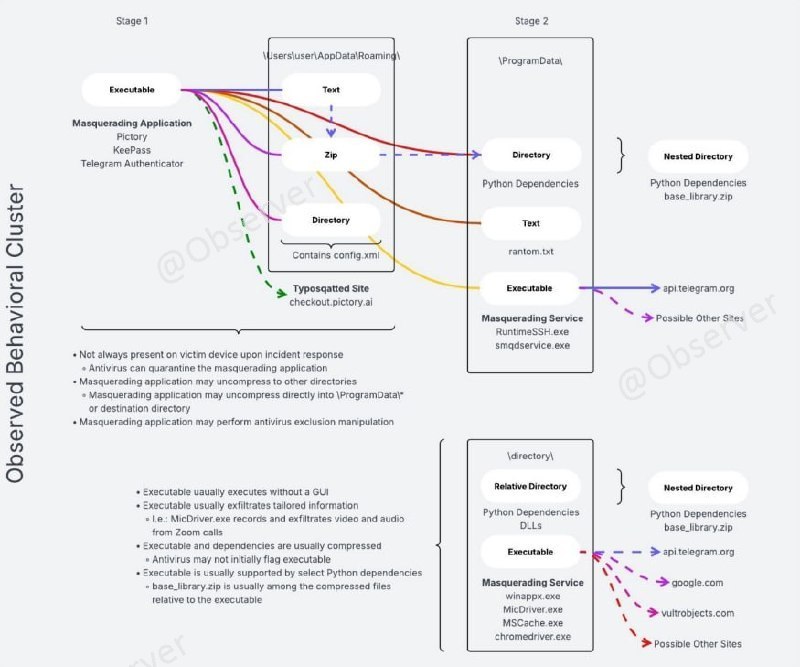
The FBI issued a FLASH alert warning that Iranian cyber actors are using Telegram as command-and-control (C2) infrastructure to deliver malware to targeted victims.
The campaign targets dissidents, journalists, and opposition groups, enabling data theft, surveillance, and remote access to infected devices.
🤖 Indicators
KeePass.exe 7402F2F9263782A4C469570035843510
MicDriver.dll F8B5554808428291ACC65D1FD2EFE01C
MicDriver.exe D70EBF20E3D697897BAD5BEBF72EA271
MsCache.exe 3E7A2FCEF1D038D05B20148C573A6499
Pictory_premium_ver9.0.4.exe 1E6B601F733BC40EAA58916986BFC5B9
rantom.txt A3394EF7FFA7E88B2E7EFAEE4617FE04
rantom.txt 2965817D063F1E8F9889F9126443D631
RuntimeSSH.exe EBDD9595B79B39F53909D862499DBC94
RuntimeSSH.exe E51FF37FB431767DCDEC0B5E6D2A786A
smqdservice.exe 7E23FFADB664B0E53D821478A249D84C
Telegram_Authenticator.exe B9086413E7B6A0C6A11C25D14C22615F
winappx.exe 481C5B5E69A08C3DF206C59FD8DDC0DC
🔔 @observer • 💬 Join community