TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.33K
Photos
438
Videos
3
Links
580

Showing posts older than #94 · Back to latest

Older Posts 20 shown
Post #91 468
CVE-2023-36764: Elevation of Privilege in Microsoft SharePoint Server, 8.8 rating 🔥

Attacker could gain administrator privileges by creating an ASP.NET page with specially-crafted declarative markup. Only authorization at the Site Member level is required.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/BBPrT
👉🏻 Dork: http.headers.microsoftsharepointteamservices:*

Vendor's advisory: https://msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36764
  • 🔥 2
  • 👾 2
  • 👍 1
Post #90 518
CVE-2023-39361, -31132, -39359 and other: Multiple vuln (17 CVE's!) in Cacti, from 3.5 to 9.8 rating 🔥

Stored XSS, SQL injection, RCE, Privilege Escalation... Vulnerabilities for every taste!

Search at Netlas.io:
👉🏻 Link: https://nt.ls/tTozX
👉🏻 Dork: http.title:"Login to Cacti"

Read more: https://github.com/Cacti/cacti/security
  • 👾 4
  • 🤯 1
Post #89 485
CVE-2023-4596: RCE in Forminator plugin for WordPress, 9.8 rating 🔥

The Forminator plugin in WP is vulnerable to arbitraty file upload for unauthenticated users, which may make RCE possible. PoC is available❗️

Search at Netlas.io:
👉🏻 Link: https://nt.ls/3Tgzc
👉🏻 Dork: http.body:"/wp-content/plugins/forminator"

PoC is here: https://github.com/E1A/CVE-2023-4596
  • 🔥 3
  • 👾 3
  • 👍 1
Post #88 531
CVE-2023-40176, -40177, -40572, -40573: Multiple vuln in XWiki, 9.0-9.9 rating 🔥

Fresh RCE, Privelege Escalation and stored XSS in XWiki Platform.

Search at Netlas.io:
👉 Link: https://nt.ls/SSzCU
👉 Dork: http.title:"XWiki" OR http.favicon.hash_sha256:6f0fdef9a229150fbc7183a1bbb136d7b44b6df7c34369c14bebb6adae8aaf20
  • 👾 3
  • 👍 2
  • ❤ 1
Post #86 462
CVE-2023-39143: RCE in PaperCut MF/NG, 8.4 rating 🔥

Vuln enables unauthenticated attackers to potentially work with arbitrary files to the PaperCut MF/NG application server (< 21.2.3 version), resulting in RCE in certain configurations.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/ZGjrR
👉🏻 Dork: (http.title:"PaperCut Login" AND (http.description:"PaperCut NG" OR http.description:"PaperCut MF")) OR (http.favicon.perceptual_hash:3e7e66667e7c6000)

Vendor's advisory: https://www.papercut.com/kb/Main/securitybulletinjuly2023/
  • 👾 3
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #85 546
There have been many requests to make CVE information available through a Freelancer subscription.

It's DONE! We hope this will make Netlas.io more useful to a wider range of users.

Sincerely yours, the Netlas.io Team
  • ❤ 7
  • 👾 4
Post #84 429
☝🏻 Another one for the same product published today: CVE-2023-35082, CVSS 10.0

A second vulnerability affecting Ivanti EPMM (formerly MobileIron Core) API has been discovered today.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/QdWH7
👉🏻 Dork: http.headers.set_cookie:("JSESSIONID" "Path" "/mifs")

Vendor’s advisory: https://forums.ivanti.com/s/article/CVE-2023-35082-Remote-Unauthenticated-API-Access-Vulnerability-in-MobileIron-Core-11-2-and-older
  • 👾 3
  • 🔥 2
  • 🤔 1
Post #83 397
CVE-2023-35078: Ivanti EPMM Remote Unauthenticated API Access Vulnerability

🚨 PoC is already available for Ivanti Endpoint Manager Mobile API vuln CVE-2023-35078 (❗️CVSS 10.0❗️)
A limited number of customers have been impacted already 😖

Search at Netlas.io:
👉🏻 Link: https://nt.ls/QdWH7
👉🏻 Dork: http.headers.set_cookie:("JSESSIONID" "Path" "/mifs")

Vendor’s advisory: https://forums.ivanti.com/s/article/CVE-2023-35078-Remote-unauthenticated-API-access-vulnerability
  • 👾 3
  • 🔥 2
Post #78 385
The end of Beta Presale II is very close!

Hurry up to get Netlas.io subscription with a 50% discount, after 6 days the discount will be reduced ❗️

👉🏻 Buy a subscription: https://app.netlas.io/plans/

In the near future, we'll also publish new features of Netlas.io (like in GIF). Sure you'll like them!
  • 👾 4
  • 👨‍💻 1
Post #77 429
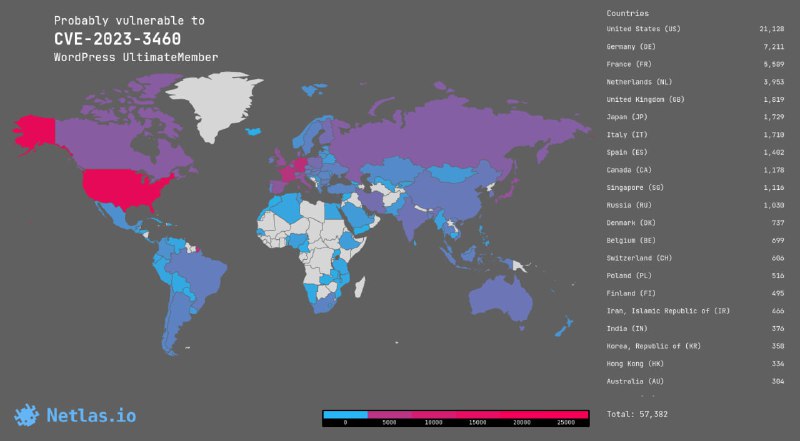
CVE-2023-3460: Privilege Escalation in UltimateMember WordPress plugin, 9.8 rating! 🔥

A vulnerability has been observed for several versions of the plugin and is actively exploited by hackers.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/S9Skz
👉🏻 Dork: http.body:"wp-content/plugins/ultimate-member"

Vendor's comments: https://wordpress.org/support/topic/cve-2023-3460/
  • 👾 4
  • 🔥 1
Post #76 402
CVE-2023-36630: Privilege Escalation and Authentication Bypass in CloudPanel, critical rating 🔥

Fresh vulnerability based on insecure file uploads.

Search at Netlas.io:
👉🏻 Link: nt.ls/V3hEn
👉🏻 Dork: http.title:"cloudpanel" NOT http.body:"2.3.1"

Read vendor's changelog: https://www.cloudpanel.io/docs/v2/changelog/
  • 👾 5
  • 🔥 1
Post #75 416
CVE-2023-3128: Authentication Bypass in Grafana, 9.4 rating ❗️
CVE vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:L

During Grafana's Azure AD account validation, an attacker can spoof the profile email field and hijack the account.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/iqMVz
👉🏻 Dork: http.favicon.hash_sha256:80a7f87a79169cf0ac1ed3250d7c509368190a97bc7182cd4705deb8f8c70174 AND http.title:"Grafana"
  • 👾 4
  • 🔥 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →