TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.32K
Photos
434
Videos
3
Links
575

Showing posts older than #395 · Back to latest

Older Posts 20 shown
Post #393 603
CVE-2025-20188: Use of Hard-coded Credentials in Cisco IOS XE, 10.0 rating 🔥🔥🔥

Due to hard-coded JWT, Cisco IOS XE instances may be vulnerable to arbitrary file uploads, path traversal, and arbitrary command execution. Catalyst controllers are primarily affected.

Search at Netlas.io:
👉 Link: https://nt.ls/BKkJI
👉 Dork: certificate.issuer_dn:"IOS-Self-Signed-Certificate"

Vendor's advisory: https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-wlc-file-uplpd-rHZG9UfC
  • 🔥 3
  • 👏 2
  • 👾 2
Post #392 654
CVE-2025-27007: Privilege Escalation in OttoKit WordPress Plugin, 9.8 rating 🔥

Errors in the logic of the plugin's API could potentially lead to an attacker gaining access to the administrator account. According to Patchstack, exploitation of the vulnerability began just an hour after public disclosure!

Search at Netlas.io:
👉 Link: https://nt.ls/y4FXX
👉 Dork: http.body:"plugins/suretriggers"

Read more: https://patchstack.com/database/wordpress/plugin/suretriggers/vulnerability/wordpress-suretriggers-1-0-82-privilege-escalation-vulnerability?_s_id=cve
  • 🔥 3
  • 👾 2
Post #391 630
CVE-2023-44221 and CVE-2024-38475: Admin Hijack Exploit in SonicWall 🔥

In a recent research, watchTowr Labs demonstrated a working exploit chain that leverages two old vulnerabilities and allows a remote attacker to take control of a SonicWall instance.

Search at Netlas.io:
👉 Link: https://nt.ls/5973o
👉 Dork: http.favicon.hash_sha256:6bb6f64adaa6a7ed4da10a2fe4edf4cb4d9914aa742c7ad607ca4ca678dcd3f1

Read more: https://labs.watchtowr.com/sonicboom-from-stolen-tokens-to-remote-shells-sonicwall-sma100-cve-2023-44221-cve-2024-38475/
  • 🔥 4
  • 👾 2
Post #390 683
CVE-2025-31324: Unrestricted Upload of File in SAP NetWeaver, 10.0 rating 🔥🔥🔥

A vulnerability in SAP NetWeaver Visual Composer Metadata Uploader allows an attacker to perform unauthenticated file uploads, including malicious ones.

Search at Netlas.io:
👉 Link: https://nt.ls/nCgfN
👉 Dork: http.body:"This error page was generated by SAP Web Dispatcher!"

Read more: https://www.bleepingcomputer.com/news/security/sap-fixes-suspected-netweaver-zero-day-exploited-in-attacks/
  • 🔥 5
  • 👾 2
Post #388 660
📢 Incident update: Due to an issue reported yesterday, the most recent data was temporarily unavailable in search. The issue has been fixed, and all data is now up to date. Sorry for the inconvenience!
  • ❤ 4
Post #387 704
CVE-2025-1763, -2443 and other: Multiple vulns in GitLab, 4.3 - 8.7 rating❗️

In a recent advisory, GitLab shared information about several fixed vulnerabilities, including XSS, DoS, and Header Injection.

Search at Netlas.io:
👉 Link: https://nt.ls/XxMjv
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/04/23/patch-release-gitlab-17-11-1-released/
  • 🔥 3
  • 👾 2
Post #386 585
✅ Service Restored 🛠

The restoration is nearly complete, and all tools are now back online. You can safely resume your work!

Thanks for bearing with us 🙌
  • 🦄 3
  • 🔥 2
Post #385 621
❗️Technical Issue Alert❗️

We're currently experiencing issues with data backups, which has temporarily taken the IP/Domain Info and Responses Search tools offline. We expect to have everything back up and running within the next 1–2 hours.

Our team is working hard to resolve the issue as quickly as possible.

👉 You can also follow the Netlas status on the corresponding page: https://status.netlas.io/

We sincerely apologize for the inconvenience and appreciate your patience 🙏
  • 😭 2
  • 💊 2
Post #384 597
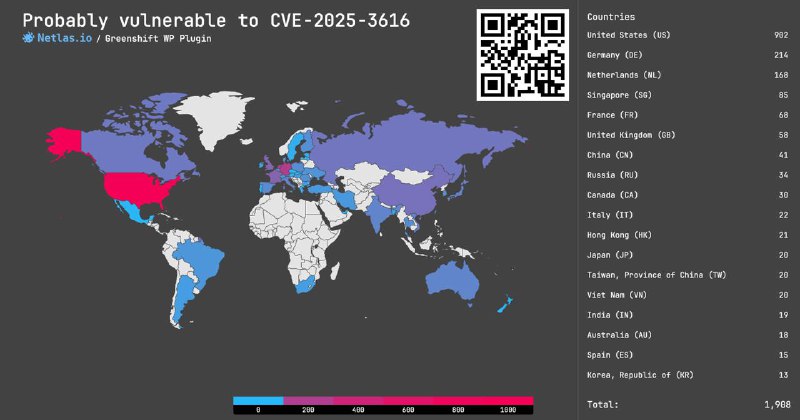
CVE-2025-3616: File Upload in Greenshift WordPress Plugin, 8.8 rating❗️

A vulnerability discovered by Wordfence researchers allows attackers to upload arbitrary files and execute them remotely.

Search at Netlas.io:
👉 Link: https://nt.ls/meWm0
👉 Dork: http.body:"plugins/greenshift-animation-and-page-builder-blocks"

Read more: https://www.wordfence.com/blog/2025/04/50000-wordpress-sites-affected-by-arbitrary-file-upload-vulnerability-in-greenshift-wordpress-plugin/
  • 🔥 4
  • 👾 1
Post #383 691
Netlas.io 🔐 Track Adversary Infrastructure Challenge Join the challenge by Netlas and RST Cloud to improve your threat-hunting skills. - Learn to detect C2 servers and investigate real threats. - Compete for prizes: 🏆 $1000, 🥈 $500, 🥉 $250. - Top 10 winners receive…
👾 Friendly Reminder 👾

The Track Adversary Infrastructure Challenge is starting in two weeks! If you want to take part but haven't registered yet, do it ASAP❗️

👉 Read more about the competition: https://netlas.io/promo/ti-challenge/
  • 👾 2
  • 🥰 1
Post #382 673
CVE-2025-24970: Improper Input Validation in Confluence Data Center & Server, 7.5 rating❗️

A vulnerability in the Netty framework could cause a server to crash if an attacker sends a special crafted packet.

Search at Netlas.io:
👉 Link: https://nt.ls/jcVrv
👉 Dork: http.meta:"confluence-base-url"

Vendor's advisory: https://jira.atlassian.com/browse/CONFSERVER-99540
  • ❤ 2
  • 🔥 2
  • 👍 1
  • 👾 1
Post #381 605
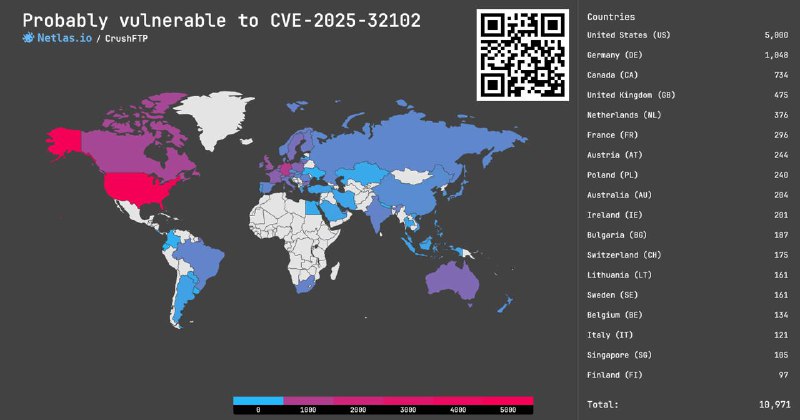
CVE-2025-32102, -32103: Multiple vulnerabilitites in CrushFTP❗️

The vulnerabilities disclosed for the popular file transfer web service include Directory Traversal and SSRF. A PoC has also been published for these vulns.

Search at Netlas.io:
👉 Link: https://nt.ls/NStLF
👉 Dork: http.headers.server:"CrushFTP"

Read more: https://seclists.org/fulldisclosure/2025/Apr/17
  • 🔥 3
  • 👾 2
Post #380 541
CVE-2025-3439: Deserialization of Untrusted Data in Everest Forms WordPress plugin, 9.8 rating 🔥

A vulnerability in the 'field_value' parameter allows a remote unauthenticated attacker to perform PHP object injection. This in turn allows the attacker to achieve RCE, retrieve sensitive data and the ability to delete arbitrary files.

Search at Netlas.io:
👉 Link: https://nt.ls/CoAb6
👉 Dork: http.body:"plugins/everest-forms"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/everest-forms/everest-forms-contact-form-quiz-survey-newsletter-payment-form-builder-for-wordpress-311-unauthenticated-php-object-injection
  • 🔥 3
  • 👾 3
Post #379 617
CVE-2025-25226, -25227: SQL Injection and Improper Authentication in Joomla, 7.5 - 9.8 rating 🔥

Vulnerabilities in Joomla CMS and Joomla's Database package allow an attacker to bypass the 2FA or perform SQLi.

Search at Netlas.io:
👉 Link: https://nt.ls/nxRtD
👉 Dork: http.meta:"Joomla!"

Vendor's advisory: https://developer.joomla.org/security-centre/963-20250401-framework-sql-injection-vulnerability-in-quotenamestr-method-of-database-package.html
  • 👍 2
  • 🔥 2
  • 👾 1
Post #377 571
CVE-2025-24446 and other: Multiple vulnerabilitites in Adobe ColdFusion, 7.5 - 9.1 rating 🔥

In a recent advisory, Adobe disclosed 11 vulnerabilities that could lead to arbitrary file system read, code execution, and a security feature bypass.

Search at Netlas.io:
👉 Link: https://nt.ls/tDhgz
👉 Dork: http.headers.set_cookie:"CFID="

Vendor's advisory: https://helpx.adobe.com/security.html
  • 🔥 5
  • 👾 4
Post #376 1.05K
CVE-2025-31489: Improper Verification of Cryptographic Signature in MinIO, 8.7 rating❗️

The vulnerability is in incomplete signature verification for unregistered downloads, which could allow an attacker to download objects using any arbitrary secret.

Search at Netlas.io:
👉 Link: https://nt.ls/TEvNJ
👉 Dork: http.favicon.hash_sha256:7a2d79d4a5801b848bf2d577c6c3d16598d69fd78bc9d2399dcc4ac2497b0759 OR http.headers.server:"MinIO" OR http.meta:"MinIO" OR http.favicon.hash_sha256:052d1670e36345713bd69e405403034f69b3a0adab8fa7d6f178faac4406199a

Vendor's advisory: https://github.com/minio/minio/security/advisories/GHSA-wg47-6jq2-q2hh
  • 👾 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →