TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.33K
Photos
435
Videos
3
Links
576

Showing posts older than #294 · Back to latest

Older Posts 20 shown
Post #293 514
Private Scanner API Documentation 📑

We’ve updated the Netlas documentation with a significant addition: a detailed guide on using the Private Scanner API.

👉 Read the docs: https://docs.netlas.io/automation/scanner_api/
  • 👍 4
  • 👾 3
Post #291 634
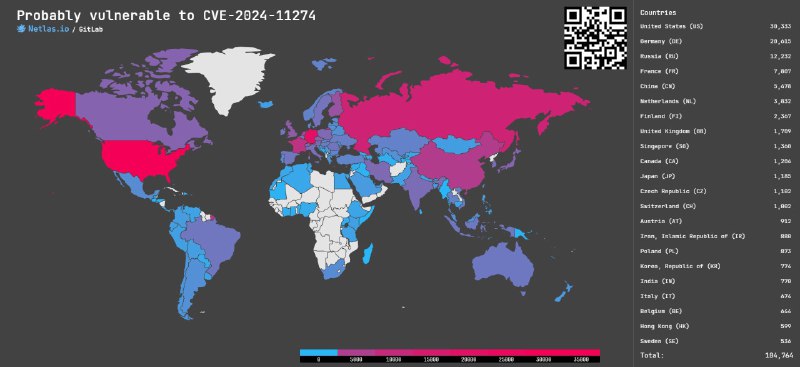
CVE-2024-11274, -8233, other: Multiple vulnerabilities in GitLab, 7.5 - 8.7 rating❗

In a new release, GitLab talked about two important vulnerabilities. One of them allows attacker to carry out DoS, the second allows to steal session data and potentially gain unauthorized access to accounts. Several smaller vulnerabilities are also mentioned.

Search at Netlas.io:
👉 Link: https://nt.ls/xM1vs
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2024/12/11/patch-release-gitlab-17-6-2-released/
  • 👍 3
  • 🔥 3
  • 👾 3
Post #289 566
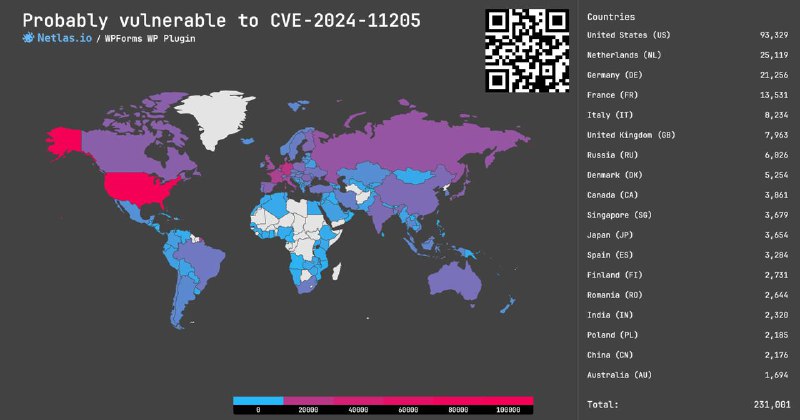
CVE-2024-11205: Missing Authorization in WPForms WordPress Plugin, 8.5 rating❗️

A vulnerability affecting several functions allows attackers to return payments made through the Stripe system.

Search at Netlas.io:
👉 Link: https://nt.ls/tFWxo
👉 Dork: http.body:"plugins/wpforms-lite"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/wpforms-lite/wpforms-184-1921-missing-authorization-to-authenticated-subscriber-payment-refund-and-subscription-cancellation
  • 👍 3
  • 👾 3
  • 🔥 2
Post #288 540
✅ Private Scanner Restored

We’re happy to share that the Private Scanner feature is now fully restored and operational.

Thank you for your patience and understanding. All systems are working fine—happy scanning!
  • 🔥 3
  • 👍 2
Post #287 591
CVE-2024-55579, -55580: RCE and Broken Access Control in Qlik Sense, 7.5 - 8.8 rating❗️

Vulnerabilities discovered in Qlik Sense allow attackers to run EXE files on the server, as well as remotely execute commands, potentially affecting confidentiality and integrity.

Search at Netlas.io:
👉 Link: https://nt.ls/9ok2E
👉 Dork: http.title:"Qlik Sense"

Vendor's advisory: https://community.qlik.com/t5/Official-Support-Articles/High-Security-fixes-for-Qlik-Sense-Enterprise-for-Windows-CVEs/tac-p/2496004
  • 🔥 3
  • 👾 3
Post #284 598
⚠️ Private Scanner Temporarily Unavailable

Since yesterday, we’ve been addressing technical issues affecting parts of our infrastructure. Most Netlas App features were fully restored within an hour after an incident and are now working smoothly. However, the Private Scanner feature remains temporarily disabled.

Our team is working diligently to fully restore our scanning infrastructure and will update you as soon as the feature is back online. We sincerely apologize for the inconvenience this has caused and deeply appreciate your patience and understanding.
  • 💊 5
  • 🙈 2
  • 👍 1
Post #283 566
✅ Netlas is back online, and all services are operational.

However, our team is continuing to monitor the system and address any lingering issues to ensure full stability. We apologize for the disruption and thank you for your patience and understanding.
  • ❤ 2
  • 👍 2
Post #282 580
🚨 Netlas is down due to issues with a planned update. We’re rolling back and working to restore service ASAP. Apologies for the inconvenience—updates to follow.
  • 💔 2
Post #281 704
CVE-2024-8672: Code Injection in Widget Options WordPress Plugin, 9.9 rating 🔥

The vulnerability allows an attacker to enter data that is transmitted without proper filtering. This could potentially lead to remote code execution.

Search at Netlas.io:
👉 Link: https://nt.ls/xOEZp
👉 Dork: http.body:"plugins/widget-options"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/widget-options/widget-options-the-1-wordpress-widget-block-control-plugin-407-authenticated-contributor-remote-code-execution
  • 🔥 5
  • 👾 4
Post #280 670
CVE-2024-11667: Directory Traversal in Zyxel Firewalls, 7.3 rating❗️

A vulnerability in the web interface of some firewalls allows an attacker to download or upload files using a special URL.

Search at Netlas.io:
👉 Link: https://nt.ls/agozE
👉 Dork: http.favicon.hash_sha256:9a02f3cf948f9409c25070f2f057b69dda5d0aaf7fa8d056552e8bda8295ca1f

Vendor's advisory: https://www.zyxel.com/global/en/support/security-advisories/zyxel-security-advisory-protecting-against-recent-firewall-threats-11-27-2024
  • 👾 4
  • 👍 3
  • 🔥 2
Post #279 649
CVE-2024-42327: SQL Injection in Zabbix, 9.9 rating 🔥

The discovered vulnerability allows any Zabbix user to perform Privilege Escalation via SQL injection.

Search at Netlas.io:
👉 Link: https://nt.ls/qH7Ao
👉 Dork: http.favicon.hash_sha256:22b06a141c425c92951056805f46691c4cd8e7547ed90b8836a282950d4b4be2

Vendor's advisory: https://support.zabbix.com/browse/ZBX-25623
  • 🔥 4
  • 👾 4
  • 👏 1
Post #277 700
CVE-2024-8114, -8177, -11669, -11668: Multiple vulnerabilities in GitLab, 4.2 - 8.2 rating❗️

GitLab has posted an advisory about several vulnerabilities. These include Privilege Escalation, DoS, Authentication Bypass, and others.

Search at Netlas.io:
👉 Link: https://nt.ls/xgD6x
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2024/11/26/patch-release-gitlab-17-6-1-released/
  • 👍 4
  • 👾 3
Post #276 632
Black Friday & Cyber Monday Discount at Netlas 🎉

Take advantage of our exclusive Black Friday & Cyber Monday deal: 20% off Freelancer and Business subscriptions for both monthly and annual billing cycles!

The best part? This isn’t just a one-time discount – it’s your forever price as long as your subscription remains active or until base prices are reconsidered 🔥

All you need to claim your forever discount is the code: BFCM2024.

👉 Learn more here: https://nt.ls/2WiQ0
  • 🔥 4
  • 👾 3
  • 👍 2
Post #275 657
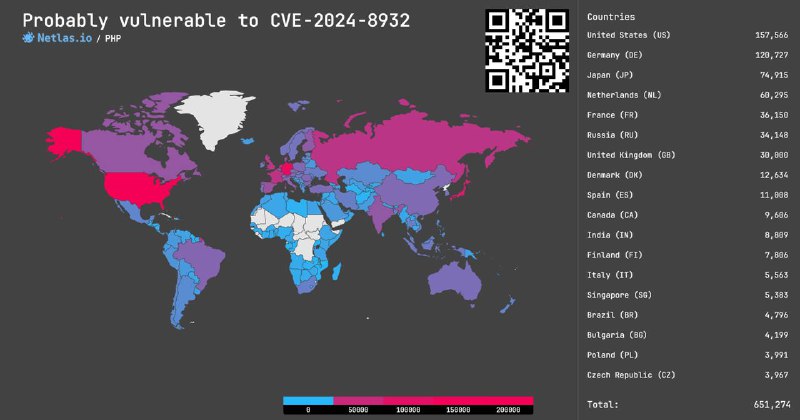
CVE-2024-8932, -8929, -11233, -11236, -11234: Multiple vulnerabilities in PHP, 4.8 - 9.8 rating 🔥

Five vulnerabilities in some PHP versions, which allowing attackers to leak sensitive information, execute arbitrary code, or launch DoS attacks.

More then 700k instances at Netlas.io:
👉 Link 1 (tag, more precisely): https://nt.ls/yIHH8
👉 Dork: tag.php.version:(>=8.1.0 AND <8.1.31) OR tag.php.version:(>=8.2.0 AND <8.2.26) OR tag.php.version:(>=8.3.0 AND <8.3.14)

👉 Link 2 (not tag, all PHP instances): https://nt.ls/9GJlg
👉 Dork: http.headers.x_powered_by:"php" OR http.headers.set_cookie:"PHPSESSID" OR http.headers.server:"PHP"

Vendor's advisories: https://github.com/php/php-src/security
  • 🔥 4
  • 👾 4
Post #274 627
CVE-2024-52052, -053, -054, -055, -056: Multiple vulnerabilitites in Wowza Streaming Engine, 5.1 - 9.4 rating 🔥

Five recent vulnerabilities we almost missed. RCE, stored XSS, file read, file write, and folder deletion - vulnerabilities for every taste!

Search at Netlas.io:
👉 Link: https://nt.ls/8BudC
👉 Dork: http.favicon.hash_sha256:3641ed4d68a0362f1ef45069584a71b0940acfcdb6abf8c13b8fc29837160a81 OR http.headers.server:"WowzaStreamingEngine"

Read more: https://www.rapid7.com/blog/post/2024/11/20/multiple-vulnerabilities-in-wowza-streaming-engine-fixed/
  • 👾 4
  • 👍 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →