
CVE-2026-75650: Adobe Commerce and Magento Open Source RCE vulnerability (StyleSmuggler) exploited in the wild, 10.0 rating 🔥
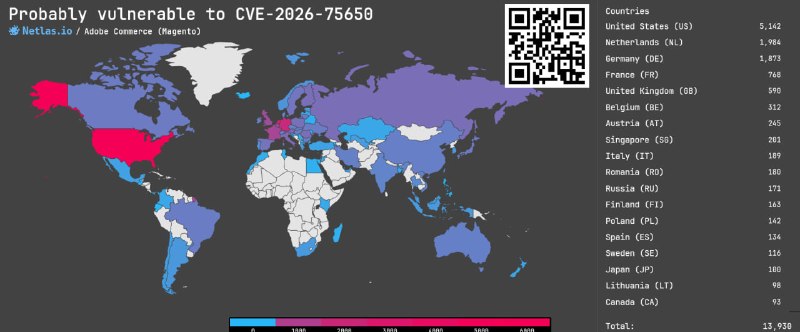
Recently disclosed vulnerability in Adobe Commerce and Magento Open Source allows an unauthenticated attacker to execute arbitrary code. This vulnerability is being actively exploited in the wild!
Search at Netlas.io:
👉 Link: https://nt.ls/bX5dx
👉 Dork: tag.name:"magento"
Read more :
https://sansec.io/research/stylesmuggler-0day
Post #627
368
- ❤ 1
- 🔥 1