
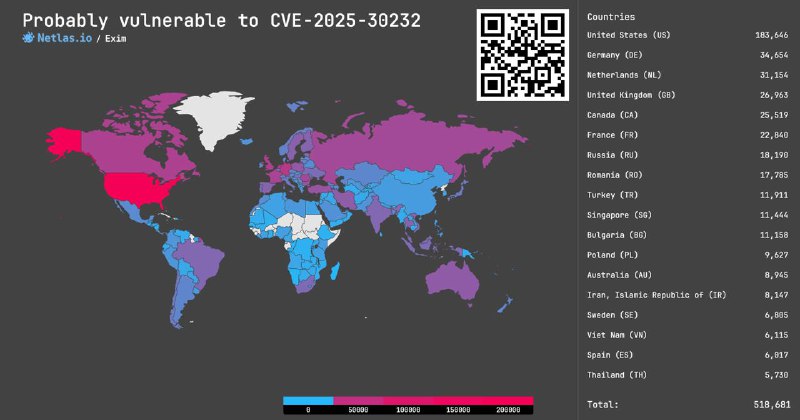
CVE-2025-30232: Use-after-free in Exim, "medium" rating❗️
A vulnerability in some versions of Exim potentially allows an attacker to perform Privilege Escalation, if he has command line access.
Search at Netlas.io:
👉 Link: https://nt.ls/mtDNc
👉 Dork: smtp.banner:"Exim 4.96" OR smtp.banner:"Exim 4.97" OR smtp.banner:"Exim 4.98" OR smtp.banner:"Exim 4.98.1"
Vendor's advisory: https://exim.org/static/doc/security/CVE-2025-30232.txt
Post #371
589
- 👾 4
- 🔥 2