
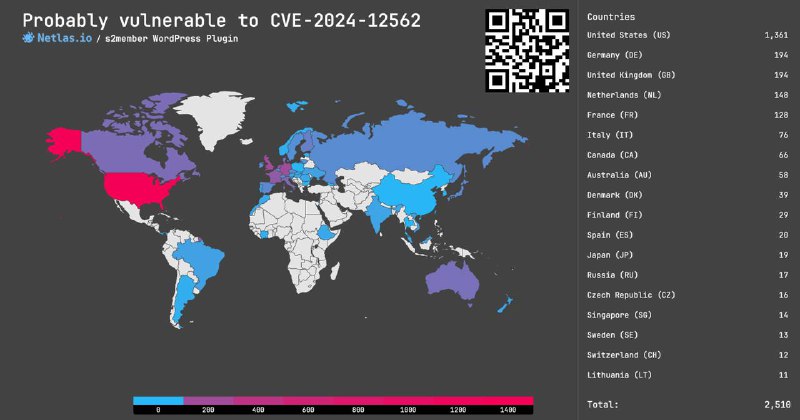
CVE-2024-12562: Deserialization of Untrusted Data in s2member Pro WordPress Plugin, 9.8 rating 🔥
The vulnerability allows attackers to inject PHP Object on all versions of the plugin, except the latest.
Search at Netlas.io:
👉 Link: https://nt.ls/GqND6
👉 Dork: http.body:"plugins/s2member"
Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/s2member-pro/s2member-pro-241216-unauthenticated-php-object-injection
Post #341
562
- 👍 2
- 🔥 2
- 👾 1