
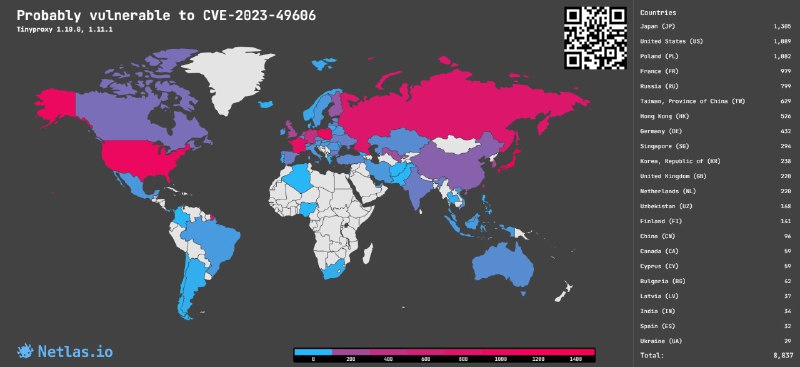
CVE-2023-49606: RCE in Tinyproxy 1.10.0, 1.11.1, 9.8 rating 🔥
A use-after-free vulnerability in Tinyproxy allows an attacker to perform RCE via a specially crafted HTTP header.
Search at Netlas.io:
👉 Link: https://nt.ls/vWqHD
👉 Dork: http.headers.server:"tinyproxy/1.11.1" OR http.headers.server:"tinyproxy/1.10.0"
Read more: https://talosintelligence.com/vulnerability_reports/TALOS-2023-1889
Post #183
1.41K
- 👍 5
- 👾 3
- 🔥 1