TGViewer
Channel Public Channel
Subscribers
2.49K
Photos
7.3K
Videos
37
Links
6.9K

Showing posts older than #30478 · Back to latest

Older Posts 20 shown
Post #30476 809
Post #30475 638

Forwarded from Curve Finance

Late last night, the curve [.] fi domain was compromised at the DNS level. This exploit redirected traffic to a malicious IP not associated with Curve Finance. No smart contracts or internal systems were breached—the protocol itself remains fully operational and secure.User — Curve Finance (@CurveFinance) May 13, 2025

https://twitter.com/CurveFinance/status/1922199907269501130
X (formerly Twitter) Curve Finance (@CurveFinance) on X Late last night, the curve [.] fi domain was compromised at the DNS level. This exploit redirected traffic to a malicious IP not associated with Curve Finance. No smart contracts or internal systems were breached—the protocol itself remains fully operational…
Post #30473 912
DO NOT VISIT CURVE FINANCE SITE! DNS HIJACK!

This has been confirmed by the team in a post on their X account here: https://x.com/curvefinance/status/1922040492121829678

The team stating their project's entire (root) domain has been "hijacked" means theytire (root) domain has been "hijacked" means the It's unknown how this attack was pulled off or exactly how their DNS was "hijacked".

1. In this scenario, the site you visit may look exactly like the normal Curve Fi site you're used to. However, you're actually getting redirected to an attacker's IP instead. This would allow them to siphon & steal any and all funds transacted or perhaps even accessed (via Metamask modal) on site.

2. Anything that is "[subdomain].curve . fi" should also be considered compromised. Any and all entities that load up assets or other resources online from that root (or sub-) domain should be considered compromised.
Post #30471 577
All Those That Contacted about the App Portal. Rolling through the queue. Got you.
  • ❤ 2
Post #30469 628
$30. One-time. Lifetime access to Quant Scanner, App Portal + Discord + 10 custom indicators.

First 20 folks. Then we're going back to subscription-based. Doing this as a "welcome back" special & a thank you reward to any who support.

I set the price this low to be fair to everyone. I know a lot of firms in blockchain that provide some great services, but what they offer isn't really affordable for the average investor just getting to understand crypto. Or hell - maybe an avid crypto fanatic that just isn't sitting on $200/month or 50 Solana tokens. Or maybe money isn’t a factor, but you’re a financially prudent individual that doesn’t want to spend bank on something without really getting to ascertain the value directly.

So $30 felt more than fair. It’s actually one hell of a deal. Deal of a lifetime to be entirely honest when considering what comes with it. Indicators alone would’ve more than covered that $30. But the Quant Scanner with it? I don’t want to call it charity, but it’s damn near. The $30 is almost like the monetary version of an “are you human” captcha.

Instructions


Once Again - Librehash Membership Open Briefly ; 20 Slots Total

$30; one-time payment.

A) Message @librehashcrypto stating your intention to join

B) I'll confirm you've reached the right person then ask which crypto you prefer to make a payment with

C) You'll respond w your preference

D) I provide an address and tell you send me your TX ID when finished

E) You send me your TX ID, then I send you the license key (for CoinQuanta) + your app portal invite (the portal itself includes all the info necessary to join the Discord etc.)

F) I get your TradingView username as well (so you can be added to the custom indicators that have been created
Post #30466 600
Here's the Quant scanner in action:

1. https://t.me/librehash/29083
2. https://t.me/librehash/29082
3. https://t.me/librehash/26099 (published results from the scanner in live time in this Telegram & then doubled back later to see price change in selected picks - went 14/15)

Proof is in the pudding here and it spans back years. Not just today.
Telegram Libre Blockchain Of course, we're only taking looks at that after we get some feedback from our Quant Algorithmic Scanner; ever used one of these? Members get to all the time.
Post #30465 558
Pi Network is a Complete Fucking Scam

There is no proof Pi Coin is running an actual blockchain at all. There's no open source code for the blockchain. The most recent repo they ever linked appeared to be some generic fork of Stellar Lumens that hasn't had a commit pushed to it in >6 years.

Pi Coin is the definition of a soft pyramid. It ain't a full blown ponzi, but it's a soft pyramid. They suckered people into signing up years ago, with the promise that if they simply logged in by opening the app up on a daily basis and performing some activities then they would be effectively "mining" tokens.

Now the project has finally "deployed" and thousands were left without their supposed mined funds that were to be granted after "migrating to the mainnet". Most of those that did manage to gain confirmation they could gain access to their funds, found out at the last minute that they would not actually become transferable on-chain for 2-3 years or more.

Some folks couldn't gain access because of the Pi Network has no consensus. There is no blockchain. There's nobody even transacting on said network apart from the team & whatever exchanges they parked that garbage on for the sake of generating enough liquidity for them to calmly exit.

Some folks couldn't verify their KYC at all (which was in part contingent on some cohort / group of lab partners that needed to KYC alongside your KYC to validate your stake ; as if this makes any fucking sense at all). KYC also should've been taken before accepting money not dishing it out - wtf? Lol.

No clue how Pi Network isn't at $0 yet. That shit is a matter of time though.
  • 👍 6
  • 👏 1
Post #30464 461
App portal will have subsidized LLM access (trial basis; figuring out the best way to implement without writing a check I can’t cash on it). Don’t expect unlimited GPT-4.5.

Other things:

1. Remote Desktop access (if needed; on demand). That’s from the server. Throwaway.

1a. Virtual Desktop (this shit is awesome - demo here: https://puter.com/)

2. Access to hosted version of AllHands (look it up if you haven’t heard of it - this is dope): https://app.all-hands.dev

3. Wireguard / proxy / Shadowsocks (many more network-based options at your disposal if you need that).

4. Smart contract storage / inspection web app (worth it; not Etherscan - respectfully - modified version of “smartmuv”)

5. Firecrawler (very good; cool)

6. Windmill (UI / app creator ; deploy on the spot)

Those are some of the top app options.
Puter
  • 🔥 1
Post #30463 360
Lifetime CoinQuanta + Indicator Access + App Portal for $30

Only extending this offer for the first 10-20 folks. You know we have to pay bills to continue executing. But $30 once in your life feels like a phenomenal offer. If interested, message @librehashcrypto (that is the account to message - definitively).

Here are the custom indicators (working on a couple new ones as well; these work phenomenally for me): https://www.tradingview.com/u/librehash/#published-scripts

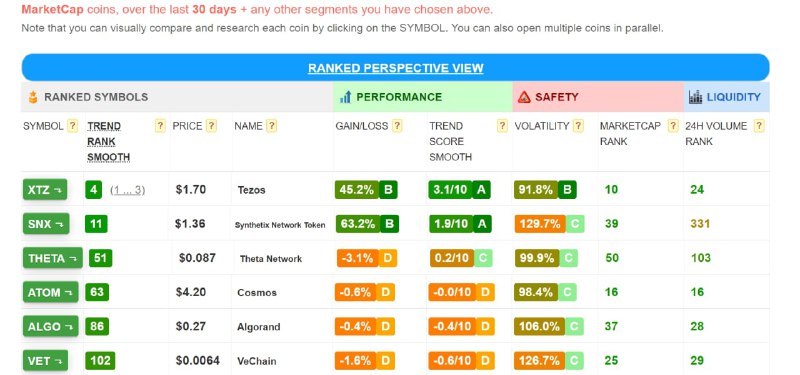
CoinQuanta is NOT a trading bot. I don’t sell or make those. The platform was designed by a brilliant former tech lead at Google (really) several years back & I’ve teamed up with him ever since to combine that offering with the app portal. What it does is use a unique “trend score” tool to help us algorithmically sift projects based on (a) correlation to Bitcoin as an anchor and (b) strength of trend. That last part is potent. If a coin has been up 20% one day, down 15% the next, then up 30% for a net change of 13% on the week you might be inclined to just look at the 13% for the week and think “looks good!”.

In reality that’s a horrible pick. We want stable performers with a demonstrable trend that somewhat bucks the industry lead (or moves similar to it at least). So maybe 6%, then +5%, then +7% on consecutive days. If the market consolidates, we factor in how much it depreciates vs reference asset with a lot of liquidity & lower volatility (comparatively) like Bitcoin or Ethereum (we don’t want to be whipsawed out of positions). Altogether this, among other metrics, allow us to very quickly identify truly good entry positions in a way you’ll never get from some volume bot that alerts you during a surge of activity or a major shift in price over some insignificant time frame.

You’re also able to control for other factors like market cap, volume, time frame (numerous ones too) etc. The platform is transparent. We don’t work on magic - it’s market logic. No, this isn’t for people that want a magical tool that tells you what to invest in and you magically get rich because it’s never wrong. This tool cuts down on your “search time” considerably and gives you a meaningful lens to identify safe (as one can get) investment opportunities.

Why So Cheap?
- I don’t have full documentation out at this moment. Still crafting it while working on a few other things on the side as well. Busy time of year right now. What I can say is whatever I just wrote doesn’t even really cover a fraction of total benefits provided.
TradingView librehash — Trading Ideas and Scripts — TradingView Follow librehash on TradingView for unique chart analysis, custom indicators, and market view. Join our global community of traders and investors.
  • 😁 3
Post #30462 426
“Jessica? Yeah I saw her last night. She was soaked when I came. I didn’t expect her to tell me to come inside this time but I’m glad I did. Things are going great now. Me & her just been working on our baby - all or nothing. No more pulling out.”

^ You have no clue what I’m talking about do you? Let’s assume something benign. It was raining last night. Jessica is one of my co-founders. I had a great idea that came to mind after we left from the co-working space. It was pouring down raining though. So we were drenched. After I texted her the idea she told me come over & I was already on the way. She was still soaked from the rain when I came over. Usually she hates company, but she invited me inside. Then we got to work on the project (our baby) after we brainstormed a bit. There were some times I thought about leaving my role as co-founder due to scheduling constraints but now I’m committed to see this through. So no more pulling out.

See How Much Context Matters? That’s What it Means to Safe Contracts


Notice how we could’ve interpreted that statement I wrote ENTIRELY different if we didn’t have that background I just gave. As a professional and colleague of Jessica’s, I’d be mortified if someone interpreted that statement as me retelling some salacious, sex filled night of passion rather than two minds coming together for a project.

That’s what we mean by context in Safe & why it’s important.
  • 👍 2
Post #30461 436
Markets are Going Absolutely Crazy Right Now

Best way that I can put it. Enjoy it if you're out here making money. You've put up with a lot of bullshit, hacks, FUD, trade war talks / tariffs, meme coins, presidential election hype & otherwise to get to this point.

Lot of folks said that Bitcoin was never going to get back here. Alas, we are are only $4k away from the previous ATH. We'll get into some market strategies very soon #neversleep
Post #30460 512
Libre Blockchain Bitcoin racing back toward $100k. Remember the potential feedback loop created by the ETF options market which occurs when market makers are forced to buy the underlying security (Bitcoin ETF in this case) in order to cover the ever increasing call options…
Bitcoin starting to go crazy. To understand what I was referring to in that previous post about the 'price feedback loop', check out this message here: https://t.me/librehash/30290

The scenario laid out in that message describes what's likely propelling Bitcoin's price at this very second.
Telegram Libre Blockchain Bitcoin Racing Toward $95k / Notes on Options ETF With the spot Bitcoin option ETF being granted, there’s now another vehicle to exert greater buy pressure on the spot Bitcoin ETF itself - which is the underlying ETF for the options vehicle. We know BlackRock…
  • 🔥 4
Post #30459 450
Bitcoin racing back toward $100k. Remember the potential feedback loop created by the ETF options market which occurs when market makers are forced to buy the underlying security (Bitcoin ETF in this case) in order to cover the ever increasing call options they’ve likely had to sell as the market momentum continues to pick up.

Said before Bitcoin wasn’t in a bear market. I’ve been here before. Lol.
Post #30458 528
Breakdown of the Economics, Resources and Straight Math For a Practical Attack

How practically? With real numbers? The computational effort required to find a suitable collision in this scenario is drastically reduced from the theoretical 2^256. A well-resourced attacker (*cough* Lazarus *cough*), targeting the lowest-entropy available signed hash(es) could feasibly obtain the necessary ~2^32 to ~2^40 uniquely 'mined' collision attempts in milliseconds to seconds.

Want some perspective? Let's take a top of the line Bitcoin miner (yes, I know they're ASICs) - Antminer SP19 (or w/e it's called). Let's say the latest model out can generate 140 TH/s (per unit). That's 140 trillion hashes per second btw (or 1.4 * 10^14). If some well resourced group repurposed an FPGA (or stack of them) to 'mine' candidate hack transactions and was able to generate the equivalent hash rate of just 3 bitcoin miners, they would bust through all 2^32 or 2^40 candidates in MICROseconds and MILLIseconds, respectively (if that's what our search space is constrained to).

Even if we up the search space to 2^60 (which is an exponentially exponential leap from 2^40), the hash rate of 3 Bitcoin miners is cracking that in under an hour (45 minutes approx.). Even at an upper bound of 2^70 (which would put us close to impractical / impossible territory), an equivalent hashrate of JUST THOSE 3 miners would find a collision in about 32 days.

Lazarus Group has made out with >$6 billion in this space over the last 3-4 years alone. You gotta be smoking crack if you don't think these dudes are probably operating in the nicest state-of-the-art Bruce Wayan style cave you can think of. North Korea has a great relationship w China.

Why wouldn't they be able to contract a little chip foundry out there, get some FPGAs rolled out for pennies on the dollar (when considering the take-home)? Well? Why wouldn't they employ it for this use?

They just made out with $1.5 billion. If these guys spent every second of their entire lives up to that point planning for that hack, you'd still have to consider that to be a profoundly wise investment of time (from a risk/reward ratio; not cheerleading antisocial behavior).
Ethereum (ETH) Blockchain Explorer Ethereum Transaction Hash: 0x5bd338eb78... | Etherscan Transfer 60,000 ETH to By bit: Hot Wallet Via Safe | Success | Feb-03-2025 04:40:59 PM (UTC)
  • 👏 1
Post #30457 386
Heard Back from Safe Team's Lead Dev: Reason to be Concerned

The Safe contracts are vulnerable. Undeniably. Hashing an EIP-712 hash into the EIP-191 standard clearly breaks the EIP-191 standard and violates every property of EIP-712 due to the simple fact we can convert it into an EIP-191.

The Safe EIP-191 implementation is not compliant with any wallet that's ever been made in mankind. Ever.

What determines whether an EIP-712 transaction hash is nested into an EIP-191 personal sign is the v byte of the r,s,v signature split (for each signature). If that value is > 30 (in hexadecimal), the contract takes the EIP-712 transaction hash the signatures would have otherwise been verified against and prefixes that with an EIP-191 prefix, then keccak256 hashes that result and verifies the signatures against that.

You know what's supposed to happen to the EIP-712 transaction hash? Nothing. This also violates an invariant in all versions of the Safe contract which dictates there shouldn't be any state changes during the checkSignatures function. However, with consumeHash = 1, and that hash mutating (bug), this constitutes as a state change in violation of the Safe contract's logic.

Attack Vector

Okay, I'm North Korea. I want to hack you Westerners. I focus on a very wealthy proxy that's deployed under Safe's buggy contracts (let's say, Bybit).

I don't need to get the owners to directly sign a malicious transaction. At all. If I can create a malicious transaction (H)M, that when erroneously double hashed and nested in the EIP-191 standard yields an output (H)M' that is equivalent to a real transaction hash (H)R, then I'm in there like swim wear.

So (H)M' = (H)R is the goal for an attacker.

At first glance, this seems impossible right? But not really.

I showed the calldata for the execTransaction function call a few posts back. You probably noticed huge blocks of repetitious zeroes. That's how most of those function calls look. The only real difference from call to call might be the to, value and the data parameters - that's it. Rest of the values will pretty much be the same.

Why's that relevant? That limits the "wiggle room" there is for variability in these transactions (entropy) - which, effectively, reduces the collision space an attacker needs to search. Exponentially (literally). Further consider that Ethereum addresses themselves are already truncated to a 20-byte keccak256 hash of their public key (keccak256 hash function spits out 32-byte outputs).

Addresses are also encoded (restricting character choice to certain letters and all numbers that must adhere to a unique sub-grammar). The operation parameter is just a uint8. The nested transfer has an identical prefix (`0xa9059cbb`), different "token address" with no token amount (effectively more null bytes).

Here's one instance on the blockchain where the only difference between these two (legitimate) transactions (besides the fact one failed & the other didn't) was the nonce value:

1. 0x5bd338eb788898addcbd079cac3e661ae139f0b3b5fb354f83012a438da88b71

2. 0xd20a076a43804ffd392587cfb3a1a8825a482b768c2184beffef71b566c29ed6

That's just a 1-byte difference.

Thanks to this bug, an attacker can aggregate every valid signature that's ever been produced by the victim's group of authorized signers (`EIP-712`on any proxy at any version on Ethereum at least) with an execTransaction function and attempt to "mine" a malicious transaction with parameters that, when erroneously nested in the EIP-191 standard, results in a hash that collides with a legitimately signed TX (wherever it can be found).

When considering the degrees of freedom the attacker has (in crafting a colliding transaction), dozens or hundreds of valid candidates (`H(R_i)`). Which effectively resolves to H(M)' ∈ {H(R_i), H(R_ii)...H(R_n) this is practical as fuck.
Ethereum (ETH) Blockchain Explorer Ethereum Transaction Hash: 0x5bd338eb78... | Etherscan Transfer 60,000 ETH to By bit: Hot Wallet Via Safe | Success | Feb-03-2025 04:40:59 PM (UTC)
  • ❤ 2
Post #30456 359
Two EIP-712 json files that are different yet still produce the same signature when signed with the same private key: https://gist.github.com/FoobarProtocol/7802b5f69fd93f97d3f0eb2aec0c4ca1

^^ Guide on how to reproduce & explanation of why included as well.

Extremely relevant when considering the attack vector I just outlined for Safe contracts.
Gist Two EIP-712 Compliant JSON Files Evoke Same Signature Two EIP-712 Compliant JSON Files Evoke Same Signature - two_eip712_duplicatehash.md
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →