TGViewer
Channel Public Channel
Kubesploit

Kubesploit

@kubesploit

News and links on Kubernetes security curated by the @Learnk8s team
Website: https://kubesploit.io/
Subscribers
2.13K
Photos
953
Videos
206
Links
1.9K

Showing posts older than #1848 · Back to latest

Older Posts 20 shown
Post #1847 349
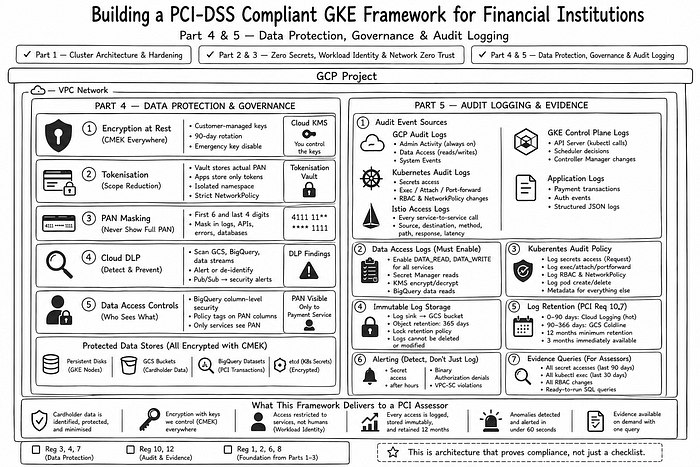
This tutorial explains how to build a PCI-DSS focused GKE security framework using:

- Workload Identity,
- Secret Manager,
- Binary Authorization,
- NetworkPolicy,
- VPC Service Controls,
- Private Service Connect,
- Istio mTLS,
- and audit logging.

More: https://ku.bz/cD6Lg9ppD
Post #1846 237

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 195:

🔍 Practical Detection Engineering for Kubernetes: Baselining Audit Logs
🤖 Building an AI Agent That Runs Your SRE Operations — What I Learned, What Works, and How You Can Do It Too
🛡️ Building an OSS Kubernetes Security Console
🧩 User Namespaces in Kubernetes: The Implementation
🔀 Vlan Migration: Moving a Live Kubernetes Cluster Without Downtime

Read it now: https://kube.today/issues/195

⭐️ This issue is brought to you by daily.dev — where developers discover what's next https://ku.bz/PrzB1cB0K
Post #1845 282
This article explains how Kubernetes user namespaces are implemented through pod UID/GID range allocation, idmap mounts, containerd, runc, and safeguards against privilege escalation.

More: https://ku.bz/z9DNn9t1D
Post #1844 266

Forwarded from KubeFM

The newest tool is not automatically the right architectural choice.

Before evaluating implementations, Fabián Sellés Rosa defined three criteria: flexibility, production maturity, and operational effort. This made it possible to compare Crossplane, a custom controller, and KRO with ACK on the same terms.

You will learn:

- Why KIAM became urgent to replace after years of stable operation
- How to define evaluation criteria before comparing tools
- Why Adevinta selected KRO with ACK for reconciliation
- How Kyverno preserves namespace-level IAM boundaries

Watch (or listen to) it here: https://ku.bz/R_06hwnCn

🌟 This episode is brought to you by LearnKube. Download The Technical Guide to Kubernetes Rightsizing to understand what Prometheus and Grafana cannot tell you about safely reducing requests and limits: https://learnkube.com/kubernetes-rightsizing

With @Birthmarkb
Post #1843 256
This article explains how Falcon Shield extends CrowdStrike security into SaaS applications through posture management, identity governance, OAuth visibility, permission drift detection, and identity threat response.

More: https://ku.bz/XvW_Xp6X0
Post #1842 390
This tutorial explains how to build a PCI-DSS focused GKE security framework using Workload Identity, Secret Manager, NetworkPolicy, zero trust networking, Binary Authorization, audit logging, and secure access patterns.

More: https://ku.bz/XNmQ2X-7T
Post #1841 332

Forwarded from KubeFM

For many edge deployments, sovereign requirements mean the cloud is not the default.

Przemysław Wojtunik explains that customers want to know who stands behind the technology and where their workloads run, which is why his team continues to focus on on-premise installation.

Watch the full interview: https://ku.bz/TJRYGMWV2
Post #1840 317
This tutorial explains how to connect Kubernetes authentication to LDAP through Dex and OIDC.

It covers certificates, OpenLDAP, Dex Helm setup, API server trust, token claims, and RBAC group mapping.

More: https://ku.bz/nN1m_5FXK
Post #1839 291
This article explains how to build a Kubernetes security console that turns CRD-based security findings and runtime events into one MCP-backed triage surface.

More: https://ku.bz/ZHmHZys-n
Post #1838 285

Forwarded from KubeFM

Alessandro Pomponio, Research Software Engineer @ IBM Research, explains how his team used Kyverno policies to solve GPU resource monopolization in their Kubernetes clusters. He describes a common anti-pattern where researchers were creating idle pods with commands like sleep infinity and using SSH to treat them as virtual machines, causing GPU starvation for other users, especially during conference deadlines.

Alessandro walks through their policy-based solution using Kyverno to block pod exec commands while maintaining necessary exceptions for cluster administrators.

Watch the full episode: https://ku.bz/5sK7BFZ-8
Post #1837 182

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 194:

🤖 We're a 3-Person Tech Team Running Production Kubernetes — So We Built an AI SRE
💸 The GPU Bill Was $40,000. Nobody Knew Why.
🔓 Copy Fail in Kubernetes: PSS Restricted and RuntimeDefault Did Not Block AF_ALG
📦 How We Set Up One Private Container Registry for 6 AKS Clusters Across 3 Regions and What Broke Along the Way
⚙️ GitOps with Terraform Using tofu-controller: Grafana and Hashicorp Vault as Code

Read it now: https://kube.today/issues/194

⭐️ This issue is brought to you by Isovalent — enterprise-grade Kubernetes networking and security, built by the creators of Cilium and eBPF https://ku.bz/d6xF7GMzh
Post #1836 266

Forwarded from KubeFM

Security in Kubernetes does not have to be an expert-only discipline.

Abhishek Rao shares a simple mental model for platform security: layer access and isolation step by step, just like physical security in a building. The point is not perfect complexity, but practical controls teams can actually adopt.

When security feels understandable, adoption becomes realistic.


Watch the full interview: https://ku.bz/_q9XBgY2c

This interview is a reaction to Mac Chaffee's episode https://ku.bz/9nFPmG85f
Post #1835 232
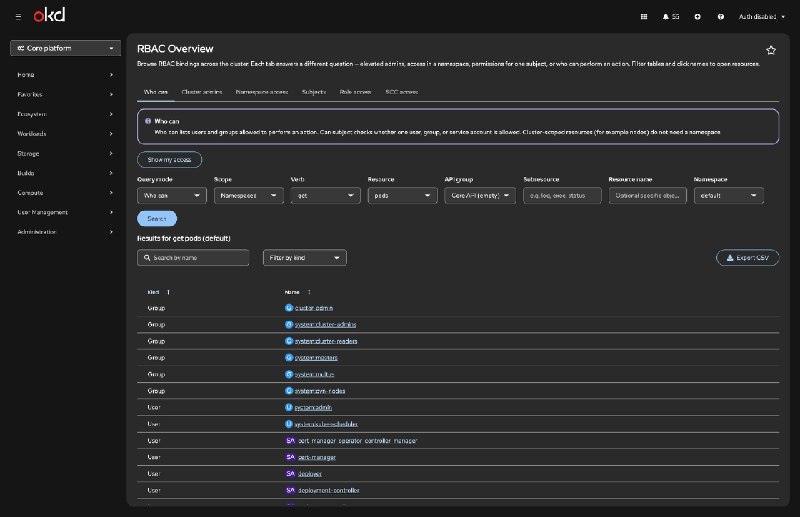
This tutorial shows how to use the RBAC Overview OpenShift console plugin to audit users, service accounts, role bindings, cluster admins, and SCC access.

More: https://ku.bz/gMzL4pXNq
Post #1834 213

Forwarded from KubeFM

Federico Iezzi, Customer Engineer at Google Cloud, explains how his team achieved 1 million output tokens per second using Qwen 3.5 27B, vLLM, GKE Autopilot, and NVIDIA B200 GPUs.

You will learn:

- Why memory bandwidth limits decode performance
- How Federico chose between tensor and data parallelism
- What changed after enabling multi-token prediction and reducing the KV cache footprint with FP8 quantization

Watch (or listen to) it here: https://ku.bz/1xD9Md0mb

🌟 This episode is brought to you by LearnKube. Download the free book, The Technical Guide to Kubernetes Rightsizing, to understand what Prometheus and Grafana cannot tell you about safely reducing requests and limits: https://learnkube.com/kubernetes-rightsizing

With @Birthmarkb
Post #1833 312
Nomos governs AI agent actions for Claude Code, Codex, Cursor, and MCP by enforcing allow, deny, or approval decisions before file, shell, Kubernetes, GitHub, HTTP, or secret access runs.

More: https://ku.bz/DLKSbPlGK
Post #1832 748
This tutorial explains how to sign and verify Docker images in Amazon ECR using Cosign and AWS KMS.

It also shows how trusted image enforcement can fit into EKS and Kyverno-based supply chain security.

More: https://ku.bz/NG8185Rvq
Post #1831 422
This case study explains how a privileged Kubernetes pod with host access can lead to container escape, control plane disruption, service account theft, and cloud resource takeover.

More: https://ku.bz/LXMBJmlKp
Post #1830 397

Forwarded from KubeFM

Container registries are often treated like storage, but they sit in the middle of delivery.

Meg Sarros explains why the registry is part of the CI/CD control plane: teams build an image, push it to a central place, and rely on that same place to manage access, encryption, and auditing.

The key point is that registry choices shape both deployment flow and governance.


Watch the full interview: https://ku.bz/k_r1B0Rwj
Post #1829 317
This article explains why Kubernetes PSS Restricted and RuntimeDefault seccomp did not block AF_ALG access during Copy Fail testing.

It shows why kernel attack surface still matters even when pods follow strict runtime defaults.

More: https://ku.bz/j-pzF0QZb
Post #1828 262

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 193:

🔍 Which of our Containers are Chainguard?
💸 One Forgotten Notebook on an A100. $1,800 a Month.
🔄 How an Admin Cluster Keeps Application Clusters in Sync with GitOps
📉 Cost Optimization of Spark on Kubernetes Batch Workloads on Public Clouds
🚪 ingress-nginx Is Archived: How We Migrated to kgateway (and Didn't Break Prod)

Read it now: https://kube.today/issues/193

⭐️ This newsletter is brought to you by LearnKube — master Kubernetes with hands-on training designed for engineers who want to learn the smart way https://ku.bz/hypSbyc-V
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →