TGViewer
Channel Public Channel
Kubesploit

Kubesploit

@kubesploit

News and links on Kubernetes security curated by the @Learnk8s team
Website: https://kubesploit.io/
Subscribers
2.13K
Photos
961
Videos
207
Links
1.9K

Showing posts older than #1468 · Back to latest

Older Posts 20 shown
Post #1467 251

Forwarded from KubeFM

Alessandro from IBM Research how his team transformed their chaotic bare-metal clusters into a well-governed, self-service platform for AI and scientific workloads.

You will learn:

- How to implement GitOps workflows that reduce administrative burden while maintaining governance and visibility
- Practical policy enforcement strategies using Kyverno to prevent GPU monopolization, block interactive pod usage, and automatically inject scheduling constraints
- Fair resource sharing techniques with Kueue to manage scarce GPU resources across different hardware types

Watch (or listen to) it here: https://ku.bz/5sK7BFZ-8

🌟 This episode is brought to you by Testkube—the ultimate Continuous Testing Platform for Cloud Native applications. Scale fast, test continuously, and ship confidently https://ku.bz/lnxYK3s0L

With @Birthmarkb "Udinese Lead Press Officer" Farrell
Post #1466 365
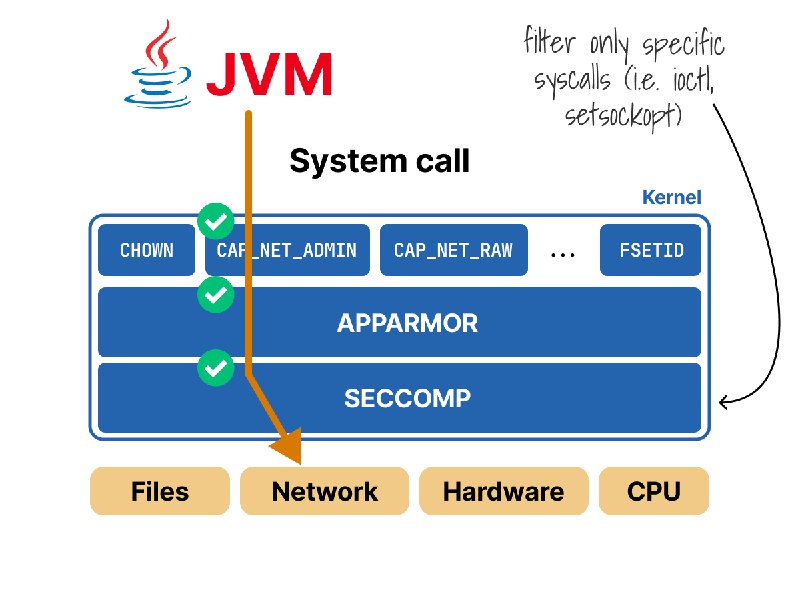
This article explains how to use offensive container security techniques for Docker and Kubernetes, covering misconfigurations, attack paths, and defenses.

More: https://ku.bz/WKmQXwcMN
Post #1465 297

Forwarded from LearnKube news

In Kubernetes, containers typically start with root privileges.

This happens because, by default, container processes run as UID 0 unless overridden. While convenient during development, it introduces unnecessary risk in production environments.

If an attacker compromises the container, root access increases the likelihood of privilege escalation to the host.

Our latest article "From Linux Primitives to Kubernetes Security Contexts" demystifies these concepts.

Read the full article: https://learnkube.com/security-contexts
Post #1463 454
This guide will teach you how to integrate HashiCorp Vault with Kubernetes Secrets CSI Driver, configure Kubernetes authentication, and create SecretProviderClass resources for secure secret management.

More: https://ku.bz/FSg9XsTZc
Post #1462 1.41K
argocd-vault-plugin is an Argo CD plugin that retrieves secrets from Secret Management tools and injects them into Kubernetes.

More: https://ku.bz/0Gz8zfVch
Post #1461 385

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 143:

🤔 Can a Simple 4-Core, 16 GB RAM Machine Reach 1000 TPS?
🧢 Cap or no cap
🔙 Reclaiming Idle GPUs in Kubernetes: A Practical Approach (and a Call for Ideas!)
💰 How We Saved $1.22 Million Annually on GCP Costs in a Few Simple Steps
🕰️ Inside Kubernetes Scheduler: What really happens before your pod lands on a node

Read it now: https://learnkube.com/issues/143

⭐️ This newsletter is brought to you by LearnKube — get started on your Kubernetes journey through comprehensive online, in-person, or remote training https://learnkube.com/training
Post #1460 371

Forwarded from Kube Architect

Sveltos installs as a controller in a management cluster, deploying add-ons and policies (Helm charts, Kustomize, raw YAML) to target clusters by label selectors and sync rules, automating multi-cluster resource management and compliance.

More: https://ku.bz/RgJVTPtfJ
Post #1459 402
ToolHive secures Model Context Protocol (MCP) servers in Kubernetes using native features like RBAC, network policies, and StatefulSets.

It isolates servers via a proxy, blocking direct network access for enterprise-grade security.

More: https://ku.bz/cJ4HXTrnS
Post #1458 1.48K
Reflector is a Kubernetes addon designed to monitor changes to resources (Secrets and ConfigMaps) and reflect changes to mirror resources in the same or other namespaces.

More: https://ku.bz/wPZw27PGH
Post #1457 458

Forwarded from KubeFM

Hillai Ben-Sasson and Ronen Shustin, Security Researchers at Wiz, explain how gaining code execution on a node can allow attackers to exploit kubelet credentials to access sensitive cluster resources.

This issue highlights the risks of overly powerful service accounts, even on isolated nodes, as they can inadvertently expose sensitive data from other customers.

Watch the full episode: https://ku.bz/yr16qNTFx
Post #1456 472
KSOPS is a kustomize exec plugin for SOPS encrypted resources.

KSOPS can be used to decrypt any Kubernetes resource, but is most commonly used to decrypt encrypted Kubernetes Secrets and ConfigMaps.

More: https://ku.bz/615H3TNYJ
Post #1455 445

Forwarded from Kube Architect

Learn how UiPath replaced mutating webhooks with a Helm library solution, enabling flexible cross-service configuration management in Kubernetes without cluster-wide permissions.

More: https://ku.bz/frf79NxRC
Post #1454 492
This article explains how Kubernetes handles Linux capability names inconsistently, with behavior differing between container runtimes like containerd and CRI-O.

More: https://ku.bz/Fk3B8xWbr
Post #1453 1.44K
Kyverno is a policy engine designed for Kubernetes.

It can validate, mutate, and generate configurations using admission controls and background scans.

Kyverno policies are Kubernetes resources and do not require learning a new language.

More: https://ku.bz/swJ_5DtbJ
Post #1452 398

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 142:

🐳 How Kubernetes Runs Containers: A Practical Deep Dive
0️⃣ Why Scale to Zero?
💰 How We Saved 80% on Our Observability Bill!
📝 Kubernetes configuration and infrastructure as code taxonomy
🏎️ Kubernetes performance tuning: eviction thresholds

Read it now: https://learnkube.com/issues/142

⭐️ This newsletter is brought to you by LearnKube — get started on your Kubernetes journey through comprehensive online, in-person, or remote training https://learnkube.com/training
Post #1451 458
This tutorial covers east-west routing configuration utilizing CoreDNS, Traefik, cert-manager, and trust-manager for domain resolution and secure certificate management.

More: https://ku.bz/QfzB7zPcf
Post #1450 449
The ClusterSecret operator keeps matching namespaces updated with secrets:

- New matching namespaces receive the secret automatically. - Changes to the ClusterSecret update all related secrets, and deleting it also removes all cloned secrets.

More: https://ku.bz/L452YC-Mp
Post #1449 551
The tutorial explains how to securely integrate AWS Secrets Manager with Kubernetes using the External Secrets Operator (ESO), automating secret synchronization via YAML configurations and IAM credentials to eliminate hardcoded secrets.

More: https://ku.bz/TR1h6vSwl
Post #1448 605
k8s-remix is an operator to compose secrets with the same flexibility as a pod env spec field.

It monitors changes to configmaps and secrets mentioned in the dataFrom field, and triggers an update whenever these resources are updated.

More: https://ku.bz/vpTfmB6mP
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →