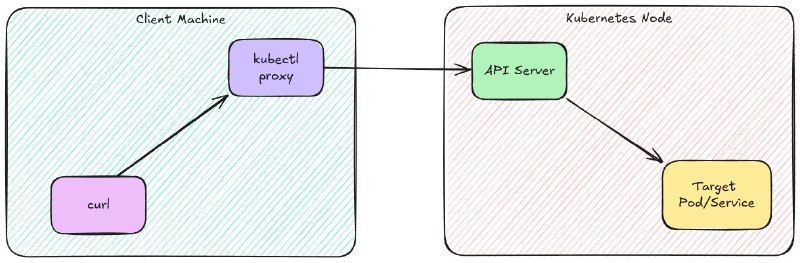
The Kubernetes API server includes an HTTP proxy that allows authorized users to access pods, nodes, and external hosts from the cluster network.
With proxy and node rights, attackers can SSRF into the API server or override pod IPs to exfiltrate data.
More: https://ku.bz/r70-_Vww0
Post #1373
958