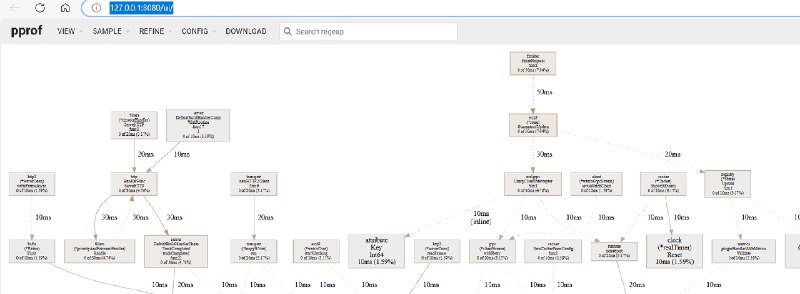
Kubernetes profiling, enabled by default in the API server, scheduler, controller-manager, etc., can pose a security risk if not properly managed.
While the information is gated behind authz & authn, certain clusters can still be vulnerable to attacks.
More: https://raesene.github.io/blog/2024/06/18/Taking-A-Look-At-Kubernetes-Profiling
Post #1128
1.15K