TGViewer
Channel Public Channel
Inside Casual

Inside Casual

@insidecasual

Hi! I’m Casual. Jack of all trades, master of none. That’s my personal blog.

Telegram mirror of - https://inside.ca.sual.in/
Subscribers
7
Photos
10
Videos
0
Links
15
Recent Posts 16 shown
Post #27 90
TUI To-Do app (WebDAV)

If you are using To-Do apps with syncronization with WebDAV (e.g. Nextcloud), you can use Tempus:

It shows today’s tasks, sort them by time and priority, you can create/complete tasks.

via Inside Casual
Post #24 75
HowIs STANDOFFxBCS meetup

Hi, I was at BCS meetup at Positive Technologies office.
“Tuesday’s evening starts with beer. *POP*”
It was small presentation by security/triage team from company, they shared experience how they were creating bugbounty program and insights how they traige bugs and what can be expected from their program.

Currently BCS focus on server-side bugs and decide payout based on practical impact, so no sourcemaps from dead services XD

It was fun and confusing getting to the correct floor :)

There were 10-ish hackers, it was fun talking with all participants.

Overall it was short event. Based on dedicated time I was expecting some kind of activity, but there wasn’t any. I was thinking to stay longer anyway, but friends invited to do more fun stuff :)

Thanks Standoff team for arranging event!

via Inside Casual
Post #23 63
HowIs (Awards Ceremony) Bugs Zone 6.0

Hi! I was at Awards Ceremony of Bugs Zone 6.0. It’s bugbounty private event!


# Activities

There was one short presentation - it revealed interesting common bug that I’ve been missing.

After that there was game - Jeopardy but about bugbounty and community. It was fun and for correct answer you would get plushie of BI.ZONE Bug Bounty mascot.

And of course there were vendors who presented awards for cool hackers! Unfortunately half of the hunters weren’t present. Anyway I’ve seen familiar faces and I liked to talk with them!

There was ‘secret’ activity which would require to bring laptop. But when it was revealed I wasn’t interested in it.

There were more games: air hockey and beer pong. Also tasty food and drinks.

And in the end there was karaoke!


# What I didn’t like

● Chairs at presentation hall was quite spine breaking.
● Place was a bit overcrowded for my taste
● Bringing laptop for ‘secret’ activity
● Air hockey table wasn’t providing enough air


# What I liked

● Presentation with common bug
● Jeopardy
● Talking with friends (and learning more interesting bugs))0)
● Food - one of the most tender meat
● Drinks - wanna save that energy drink can, ha-ha
● Disgracing myself at karaoke :)


# Conclusion

I would like more games and probably more social interaction activities. But I was having fun talking anyway.

It wasn’t as epic as Standoff Hacks Ahmedabad, but still fun! I would like to participate in main bugbounty event but their invitation system is unclear and anyway I would need to hunt on BI.ZONE platform, but I currently hunting on Standoff (and trying to compete on their scoreboard).

via Inside Casual

Invalid media: image
Post #22 46
The Internet Is Ending

As experts predicted: more signs of sovereign intranet appear all over the world. Few more steps to ‘I Have No Mouth, and I Must Scream’.

Datahoard data you love while you can!

via Inside Casual
Post #21 62
How is Standoff Talks (2025)

Hi! I was at Standoff Talks 2025! It’s a bugbounty(?) conference.


## Presentations

This time I’ve seen all presentations! They are good, however I was expecting that all presentations would be about bugbounty, but in fact, 50% of them wasn’t (they were about blue/red team stuff). And from bugbounty ones I was expecting more interesting bugbounty tips.


## Socializing

This time I was socializing more, but still feel that I could do better next time.

After-party was great! We had table-top games, drinks (thou variaty of drinks on previous Talks was better), pizza and other tasty stuff… It was fun!

I really like afterparties on Talks, they are really fun! I want to thank all people with which I enjoyed this evening.


# Conclusion

Amazing event organization (thou place was too crowded for my taste) - PT are really great at orginizing small events.

Presentations are good, but unfortunately there wasn’t anything groundbreaking for me.
Here I want to mention acquaintance of mine, which I wasn’t expected to meet there at all, the point is - he wasn’t interested in bugbounty before! Maybe event is more focused not on bugbounty but as entrypoint into cybersec career than private event for bughunters.

via Inside Casual

Invalid media: image
Post #18 835
HowIs Standoff Hacks Ahmedabad

Hi! I was at Standoff Hacks Ahmedabad. It’s a priv8 bugbounty event for cool hackers!


# How it worked

Some recognized hackers got direct invite and other could participate in a competition (bugbounty on specific vendors). I was directly invited, but also participated in competition and would win.

Then we had 2 weeks for bugbounty hacking few private programs with great payouts.

After that we flew to B-Sides conference in Ahmedabad to celebrate end of the event (almost every expense was covered)


# Experience

Mostly it was good experience, though due to lack of time among all parties hackers didn’t have enough time to get feedback from vendors to understand if they will accept such reports later on.

Also, I would encourage all vendors to reach hackers directly in messenger/in-person to clarify why/how some decisions happen. Communication online can be quite confusing and draining if you don’t understand emotions of interlocutor.

I’m really glad that I was here, it is one of the most productive hacking weeks in my life, thou I was virtually mentally destroyed at the end (add to that lack of sleep). After hacking we got a trip to Ahmedabad. And oh boy, it was exhausting.

So after mental and physical death I was in Ahmedabad just to catch cold in a first taxi right after landing :)

Despite all odds, I’m glad that I was there. The party was amazing. Other hackers really are sweethearts and so easygoing to talk with. It’s a shame that I wasn’t in the best condintion to socialize.

By the way, I scored top-5!!!
Though I believe I didn’t performe well enough. (special thanks to Masha, Orwa, Alexander, Elizavetta, Nastya)


# Thanks

I want to thank a lot of people who made it possible, it is really one of my most valuable memories, even if I wasn’t feeling like it at that moment. Thanks everyone!!! &LT3

Hopefully I will create more memories like those without feeling that I’m at my limits.

Folks, see you all in the next PHD/Hacks :)

----------------------

P.S. After the trip I was sleeping better and partying hard only to get more ill and prolong recovery time. XD

via Inside Casual

Invalid media: image
Post #13 1K
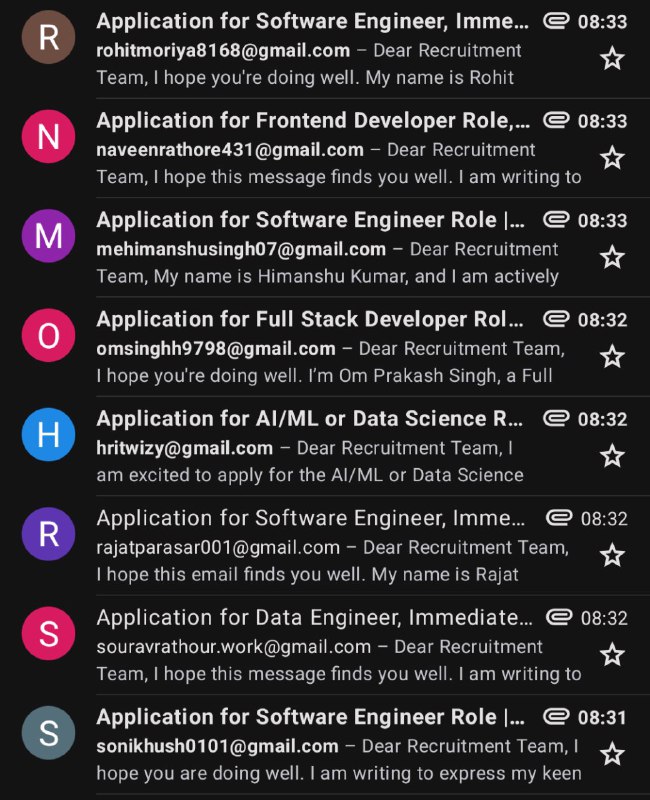
My "Company" got attacked!

Ladies and gentlemen, this is just amazing!
My “company” is being attacked by some hackers pretending to be Indians.

“Company”? Indians? You might ask

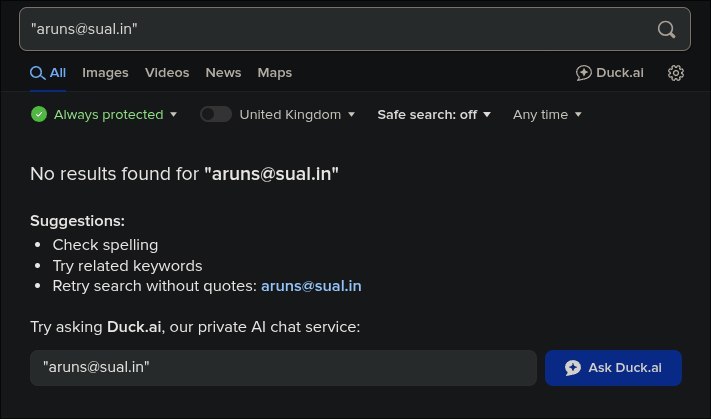
It’s simple, my domain is sual.in (the joke is - c@sual.in email) (.in - Indian TLD).
And here’s what I’m seeing now:

I’m curious how they came up with this email and why are they so dumb to send a bunch of emails at the same time…

So, I expect a Korean-style attack, where they “apply” for a job and either steal money through salaries or hack the infrastructure with subsequent data extraction

Of course, the resumes and PDFs are AI-generated (there are even empty 500KB PDFs, maybe they contain exploits), and the links don’t work (they’re just text).

----------------------

What are your suggestions on what I should do about this? Contact me!

I mean, they have used real Gmail accounts, they’re not just here to drop a payload and leave, they spent money to buy accounts, make it look real. It’s not a lot per account, but still, they’re consumables.

via Inside Casual
Post #11 110
UK pushes one step forward to a dystopian world of showing to nearly everyone your ID anywhere where user uploaded content may be.

Worst they would do is allow some specific Giga-corporation app which is known to selling user data to verify your age… oh…

And guess what? You can’t use Wallet on custom Android. So now you should have a phone which Google approves. Or potentially do facial recognition, or show your credit card, or show your bank account. Nobody would ever-ever do anything bad with your PII.

Brave New World.

----------------------
Sources
● https://www.ofcom.org.uk/online-safety/protecting-children/age-checks-for-online-safety--what-you-need-to-know-as-a-user

via Inside Casual
Post #10 88
I'm not dead

Hi, blog isn’t dead!

I’ve been doing few projects recently, so expect more posts about them!

----------------------

Tip of a day: Technology shouldn’t be complicated, they should make your life easier. Try to simplify your life!
Return to monkey

via Inside Casual
Post #4 100
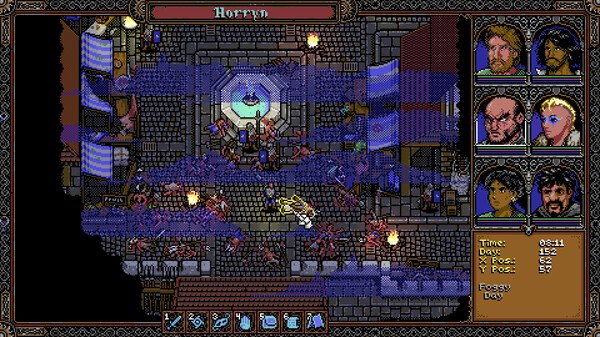
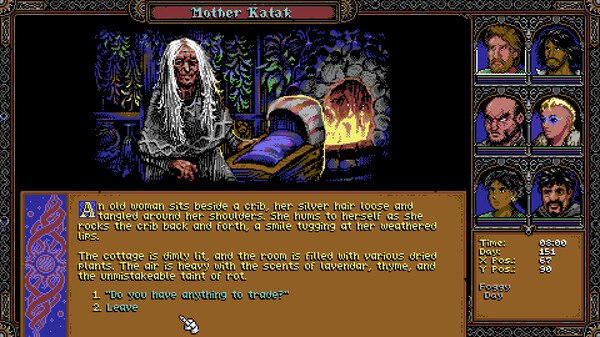
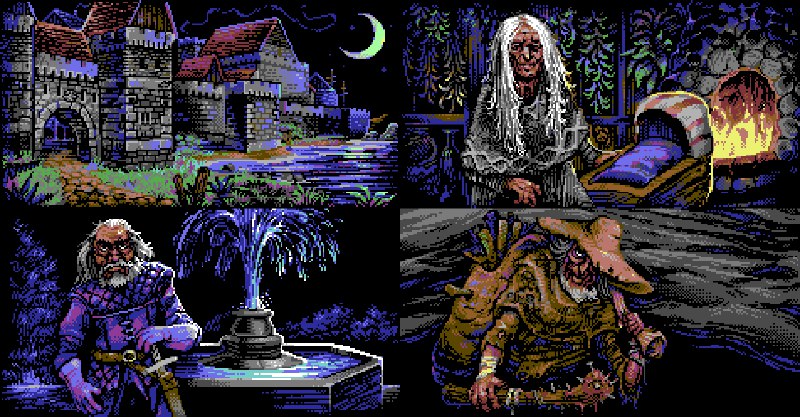
GameRev: SKALD: Against the Black Priory

‘GameRev’ - Game Review
Today I will recommend you this:

● Cool
● Retro
● Grim-dark
● Lovecraftian
● Fantasy
● CRPG

If you like DnD and classical RPGs - try it out. NOW.

If you didn’t get a thing about what I’m talking about but you like screenshots artstyle - try it out, game is good for people who never played CRPGs before .

And if you would like to be a DnD Dungeon Master yourself - there is mod support, so you can cretae your own story! (mods hosted on mod.io, no steam-workshop needed)

Steam

via Inside Casual
Older posts →

About this channel

How can I read @insidecasual without a Telegram account?
TGViewer shows the public web preview Telegram publishes for Inside Casual: recent posts, photos, videos and the subscriber count, with no app, login or account.
How many subscribers does Inside Casual have?
Inside Casual (@insidecasual) has 7 subscribers on Telegram, refreshed roughly every 30 minutes.
Does Inside Casual know I viewed it here?
No. Public channel previews carry no viewer identity, and TGViewer has no accounts or tracking of what you look up.
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →