
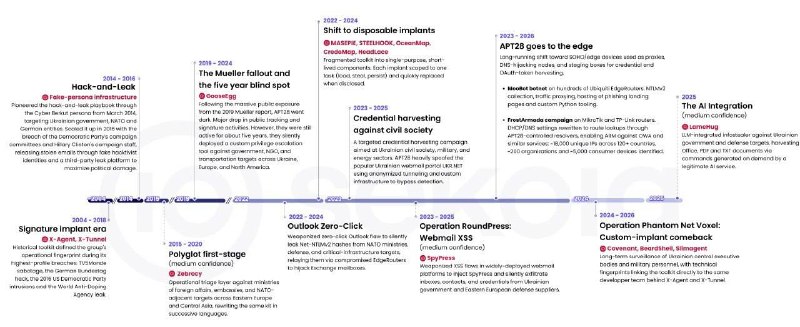
Давно не видел от вендоров ретроспективы о группах, с отсылками на исследования разделенными по годам 🦔
Третхантерам полезно почитать историю/эволюцию используемых инструментов, это как стиль действий ну или любимый тулкит 😃
Sekoia’s Threat Detection & Research (TDR) team has been tracking APT28 for several years. The intrusion set, also known as Fancy Bear, Forest Blizzard, Sofacy, Pawn Storm or Sednit and publicly attributed to the GRU’s Unit 26165, is one of the most prolific and persistent state-sponsored actors we monitor. Its operations span in two decades and consistently target government, defence, diplomatic and critical infrastructure entities, with a focus on NATO members and Ukraine.
Given its relentless activity, this intrusion-set has been extensively documented by government agencies, private cybersecurity vendors, and independent researchers. The scale of this collective coverage is reflected in the list of aliases we have compiled: That’s 33 names for one adversary.
🔗 https://blog.sekoia.io/apt28-an-evolution-of-tradecraft/