TGViewer
Channel Public Channel
Elcomsoft

Elcomsoft

@elcomsoft

Elcomsoft official channel is the place where you can find news, events and the latest updates of our products.

website: elcomsoft.com
twitter: twitter.com/elcomsoft
youtube: youtube.com/c/ElcomsoftCompany
blog: blog.elcomsoft.com
t.me/elcomsoftru
Subscribers
548
Photos
573
Videos
1
Links
458

Showing posts older than #547 · Back to latest

Older Posts 20 shown
Post #546 416
HomePod Forensics I: Pwning the HomePod

In this article, we will discuss how to access the hidden port of the first-generation HomePod and extract its file system image. Note that this process requires disassembly, voids the HomePod warranty, and requires specific tools, including a custom 3D-printable USB adapter, a set of screws, and a breakout cable. Therefore, this method is not recommended for casual users and should only be used by professionals who have a thorough understanding of the process.

🧑‍💻 https://blog.elcomsoft.com/2023/03/homepod-forensics-i-pwning-the-homepod/

#checkm8 #EIFT #HomePod #IoT #forensics
Post #545 377
A Word About Dictionaries

Dictionary attacks are among the most effective ones because they rely on the human nature. It is human nature to select passwords that are easily memoizable, like their pet names, dates of birth, football teams or whatever. BBC counted 171,146 words in the English dictionary, while a typical native speaker (of any language) knows 15,000 to 20,000 word families (lemmas, or root words and inflections). Whatever the attack speed is, it will not take too much time to check all the English words.

👉🏻 https://blog.elcomsoft.com/2023/03/a-word-about-dictionaries/

#passwords #EDPR #dictionary #password #dfir
Post #544 468
Building a Password Recovery Queue

In the previous article we discussed the different methods available for gaining access to encrypted information, placing password recovery attacks at the bottom of the list. Password recovery attacks are one of the methods used to gain access to encrypted information. In this article we’ll discuss the process of building a password recovery queue. Learn how to choose the appropriate workflow for the attack, the first prioritizing files with weaker protection, the second prioritizing faster and shorter attacks, and the third being a combination of the two. For your reference, we built a table to compare the relative strength of different file formats and encryption methods, helping users prioritize their attack queues.

🧑‍💻 https://blog.elcomsoft.com/2023/03/building-a-password-recovery-queue/

#password #dfir #EDPR
Post #543 463
Right Method, Wrong Order

In today’s digital age, extracting data from mobile devices is an essential aspect of forensic investigations. However, it must be done carefully and correctly to ensure the highest possible level of accuracy and reliability. To accomplish this, the appropriate extraction methods should be used in the right order, considering all available options for a given device running a specific version of the operating system. So what is the best order of extraction methods when acquiring an iPhone? Read along to find out.

🧑‍💻 https://blog.elcomsoft.com/2023/02/right-method-wrong-order/

#apple #ios #checkm8 #EIFT #EPB #EPV #mobileforensics #dfir
Post #540 466
Forensically Sound checkm8 Extraction: Repeatable, Verifiable and Safe

What does “forensically sound extraction” mean? The classic definition of forensically sound extraction means both repeatable and verifiable results. However, there is more to it. We believe that forensically sound extractions should not only be verifiable and repeatable, but verifiable in a safe, error-proof manner, so we tweaked our product to deliver just that.

🧑‍💻 https://blog.elcomsoft.com/2023/02/forensically-sound-checkm8-extraction-repeatable-verifiable-and-safe/

 #Apple #checkm8 #iOS #EIFT #dfir #mobileforensics
Post #539 481
Apple Releases iOS 12.5.7, iOS 15.7.3. What About Low-Level Extraction?

Apple is known for a very long time they support their devices. On January 23, 2023, alongside with iOS 16.3 the company rolled out security patches to older devices, releasing iOS 12.5.7, iOS 15.7.3 and iPadOS 15.7.3. iOS 12 was the last major version of iOS supported on Apple A7, A8, and A8X devices, which includes the iPhone 5s and iPhone 6 and 6 Plus generations along with several iPad models. We tested low-level extraction with these security-patched builds, and made several discoveries.

🧑‍💻 https://blog.elcomsoft.com/2023/01/apple-releases-ios-12-5-7-ios-15-7-3-what-about-low-level-extraction/

#ios #checkm8 #eift #agentextractor
Post #538 524
Advanced PDF Password Recovery and Archive Password Recovery updates

We released Advanced Archive Password Recovery 4.66 and Advanced PDF Password Recovery 5.11 with multiple bugfixes and enhancements. The archive recovery tool update brought support for RAR5 archives protected with passwords longer than 16 characters, and improved compatibility with self-extracting archives.

🧑‍💻 https://www.elcomsoft.com/news/828.html

#7Zip #Zip #Rar #Rar5 #PDF #passwordrecovery
Post #537 506
iOS 15.5 Low-Level Keychain Extraction

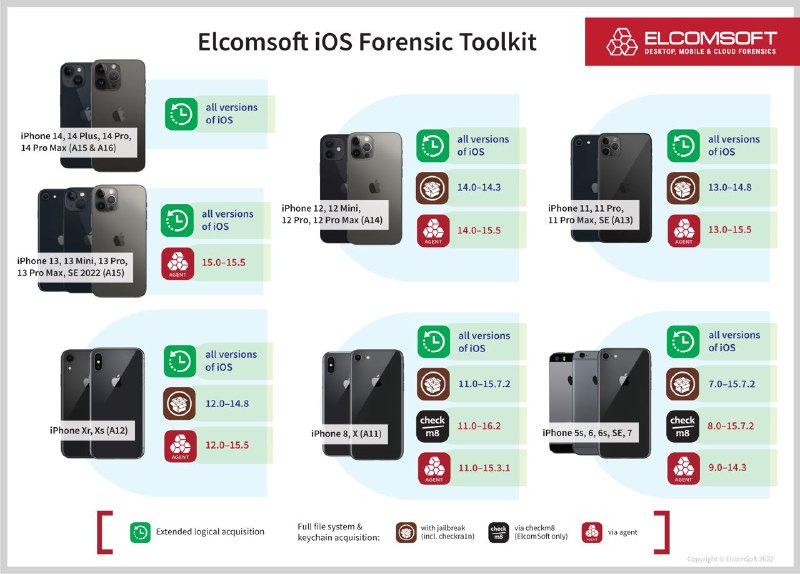
The updated iOS Forensic Toolkit 8.11 brings keychain decryption support to devices running iOS/iPadOS versions up to and including the 15.5 by using the extraction agent. The tool supports recent models that can run iOS 15 , which includes devices based on the Apple A12 through A15 Bionic, as well as Apple Silicon based devices built on the M1 SoC.

🧑‍💻 https://blog.elcomsoft.com/2023/01/ios-15-5-low-level-keychain-extraction/

#ios #EIFT #mobileforensics #keychain #ios15 #ipad #agent
Post #536 417
Use The Brute Force, Luke

There are several methods for recovering the original password ranging from brute force to very complex rule-based attacks. Brute-force attacks are a last resort when all other options are exhausted. What can you reasonably expect of a brute-force attack, what is the chance of success, and how does it depend on the password and the data? Or just “how long will it take you to break it”? Let’s try to find out.

🧑‍💻 https://blog.elcomsoft.com/2023/01/use-the-brute-force-luke/

#passwordrecovery #bruteforce #edpr
Post #535 371
Elcomsoft iOS Forensic Toolkit 8.11 decrypts iOS 15.5 keychain

Elcomsoft iOS Forensic Toolkit 8.11 adds the ability to extract and decrypt the keychain from devices running all versions of iOS/iPadOS up to and including 15.5. The Windows edition is currently available in iOS Forensic Toolkit 7.71, which receives the same update.

🧑‍💻 https://www.elcomsoft.com/news/827.html

#ios #EIFT #mobileforensics #keychain #ios15
Post #534 504
checkm8 for iOS 16.2 and Windows-based iOS Low-Level Extraction

Just before the turn of the year, we’ve made an important update to Elcomsoft iOS Forensic Toolkit, a low-level iOS file system extraction and keychain decryption tool. The update brings checkm8 support to iOS, iPadOS and tvOS 16.2 devices, and enables agent-based low-level extraction of iOS 15.5. We’ve also fixed what’s been long broken: the ability to sideload the extraction agent from Windows PCs, yet the two updates are delivered in different branches. Sounds confusing? We’re here to solve it for you.

🧑‍💻 https://blog.elcomsoft.com/2022/12/checkm8-for-ios-16-2-and-windows-based-ios-low-level-extraction/

#EIFT #ios16 #checkm8 #DFIR #mobileforensics #agentextractor
Post #533 424
Elcomsoft iOS Forensic Toolkit 8.10 adds checkm8 extraction for iOS 16.2, fixes extraction agent signing

Elcomsoft iOS Forensic Toolkit 8.10 adds forensically sound checkm8 extraction support for iOS, iPadOS and tvOS 16.2. We are also bumping agent-based extraction support to iOS 15.5, and updating Elcomsoft iOS Forensic Toolkit 7.70 to fix the extraction agent installation issues in the Windows edition.

🧑‍💻 https://www.elcomsoft.com/news/826.html

#EIFT #ios16 #agentextractor #DFIR #mobileforensics #checkm8
Post #532 445
Elcomsoft Phone Viewer 5.40 updated for iOS 16

Elcomsoft Phone Viewer gains full support for the updated local and cloud backup formats introduced in iOS 16. The tool can now display the content of iTunes and iCloud backups and synchronized data produced by devices running the new OS. In addition, Elcomsoft Phone Viewer 5.40 adds support for file system images obtained from devices running iOS 16.

👉 https://www.elcomsoft.com/news/825.html

#EPV #iCloud #iOS16 #dfir #mobileforensics
Post #531 447
Windows Account Passwords: Why and How to Break NTLM Credentials

Windows account passwords, or NTLM passwords, are among the easiest to recover due to their relatively low cryptographic strength. At the same time, NTLM passwords can be used to unlock DPAPI-protected data such as the user’s passwords stored in Web browsers, encrypted chats, EFS-protected files and folders, and a lot more. In this article we argue about prioritizing the recovery of NTLM hashes over any other types of encrypted data.

👉 https://blog.elcomsoft.com/2022/12/windows-account-passwords-why-and-how-to-break-ntlm-credentials/

#windows #ntlm #password #edpr #dpapi #microsoftaccount
Post #530 472
iOS Forensic Toolkit 8: Apple TV 3, 4, and 4K checkm8 Extraction Cheat Sheet

Several generations of Apple TV devices have a bootloader vulnerability that can be exploited with checkm8 to extract information from the device. The vulnerability exists in the Apple TV 3 (2012 and 2013), Apple TV HD (formerly Apple TV 4) 2015 and 2021, and Apple TV 4K (2017). Newer generations of Apple TV do not have the vulnerability. This guide lists the tools and steps required to fully extract a compatible Apple TV device.

👉 https://blog.elcomsoft.com/2022/12/ios-forensic-toolkit-8-apple-tv-3-4-and-4k-checkm8-extraction-cheat-sheet/

#EIFT #appleTV #checkm8 #dfir
Post #529 444
iOS Forensic Toolkit 8 Apple Watch S3 checkm8 Extraction Cheat Sheet

checkm8 is the only extraction method available for the Apple Watch S3 allowing full access to essential evidence stored in the device. In this guide, we will talk about connecting the Apple Watch S3 to the computer, placing the watch into DFU mode, applying the checkm8 exploit and extracting the file system from the device with iOS Forensic Toolkit 8.0.

👉 https://blog.elcomsoft.com/2022/11/ios-forensic-toolkit-8-apple-watch-s3-checkm8-extraction-cheat-sheet/

#applewatch #checkm8 #eift #dfir
Post #528 458
Approaching iOS Extractions: Choosing the Right Acquisition Method

The extraction method or methods available for a particular iOS device depend on the device’s hardware platform and the installed version of iOS. While logical acquisition is available for all iOS and iPadOS devices, more advanced extraction methods are available for older platforms and versions of iOS. But what if more than one way to extract the data is available for a given device? In this guide, we’ll discuss the applicable acquisition methods as well as the order in which they should be used.

👉 https://blog.elcomsoft.com/2022/11/approaching-ios-extractions-choosing-the-right-acquisition-method/

#ios #checkm8 #agent #edpr #eift #toolkit #dfir #mobileforensics #dataextraction
Post #527 394
iOS Forensic Toolkit 8 Extraction Agent Cheat Sheet

iOS Forensic Toolkit 8 brings new powerful user experience based on the command line. While this approach offers experts full control over the extraction process, mastering the right workflow may become a challenge for those unfamiliar with command-line tools. In this quick-start guide we will lay out the steps required to extract the file system and decrypt the keychain of a compatible iPhone or iPad device.

👉 https://blog.elcomsoft.com/2022/11/ios-forensic-toolkit-8-extraction-agent-cheat-sheet/

#ios #eift #extractionagent #dfir #mobileforensics
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →