TGViewer
Channel Public Channel
Elcomsoft

Elcomsoft

@elcomsoft

Elcomsoft official channel is the place where you can find news, events and the latest updates of our products.

website: elcomsoft.com
twitter: twitter.com/elcomsoft
youtube: youtube.com/c/ElcomsoftCompany
blog: blog.elcomsoft.com
t.me/elcomsoftru
Subscribers
547
Photos
573
Videos
1
Links
458

Showing posts older than #440 · Back to latest

Older Posts 14 shown
Post #439 361
iOS Forensic Toolkit 8.0 beta 2 brings forensically-sound checkm8 extraction and iOS 15 support

The second beta of Elcomsoft iOS Forensic Toolkit 8.0 for Mac is released, bringing forensically sound checkm8 extraction to iOS 15 devices and delivering a host of under-the-hood improvements and enhancements.

👉 https://www.elcomsoft.com/news/797.html

#checkm8 #ios15 #dfir #mobileforensics
Post #438 388
checkm8, checkra1n and USB hubs

If you ever used the checkra1n jailbreak or the checkm8 acquisition method available in some mobile forensic products like iOS Forensic Toolkit, you know that the trickiest parts of the process are the first two: entering DFU, and using the exploit itself. Even if you have the right cables and enough experience, sometimes you may still bump into a weird issue or two. The device may not enter DFU whatever you do, or the exploit fails. How can you increase your success rate?

👉 https://blog.elcomsoft.com/2021/11/checkm8-checkra1n-and-usb-hubs/

#checkm8 #checkra1n #mobileforensics
Post #437 341
iPhone Acquisition Methods Compared

Our mobile acquisition tools, Elcomsoft iOS Forensic Toolkit and Elcomsoft Phone Breaker, support a number of different extraction options. While many of our readers know the differences between logical and physical acquisition in general better than most, there are some things in our software making the logical/physical dilemma somewhat different. In this article, we laid out the differences between the extraction methods as implemented in our tools.

👉 https://blog.elcomsoft.com/2021/11/iphone-acquisition-methods-compared/

#dfir #mobileforensics #checkm8
Post #436 405
Apple Watch Forensics: More on Adapters

If you are doing Apple Watch forensics, I’ve got some bad news for you. The latest model of Apple Watch, the Series 7, does not have a hidden diagnostics port anymore, which was replaced with a wireless 60.5GHz module (and the corresponding dock, which is nowhere to be found). What does that mean for the mobile forensics, and does it make the extraction more difficult? Let’s shed some light on it.

👉 https://blog.elcomsoft.com/2021/11/apple-watch-forensics-more-on-adapters/

#applewatch #ios #cloudsecurity #cloudforensics
Post #435 429
The Five Ways to Recover iPhone Deleted Data

iOS security model offers very are few possibilities to recover anything unless you have a backup, either local or one from the cloud. There are also tricks allowing to recover some bits and pieces even if you don’t. In this article we’ll talk about what you can and what you cannot recover in modern iOS devices.

Before we begin, I highly recommend reading our previous article aimed at demystifying bogus claims made by some unscrupulous vendors of data recovery tools: The iPhone Data Recovery Myth: What You Can and Cannot Recover. Below are the types of data you can actually recover.

👉 https://blog.elcomsoft.com/2021/11/the-five-ways-to-recover-iphone-deleted-data/

#ios #icloud #iphone #backup #syncedfiles #deletedrecords
Post #434 343
Digital Triage Forensics: Write-Blocking, Verifiable Disk Imaging

When accessing a locked system during an in-field investigation, speed is often the most important factor. However, maintaining digital chain of custody is just as if not more important in order to produce court admissible evidence. We are introducing new features in Elcomsoft System Recovery, our forensic triage tool, to help establish and maintain digital chain of custody throughout the investigation.

👉 https://blog.elcomsoft.com/2021/11/digital-triage-forensics-write-blocking-verifiable-disk-imaging/

#passwords #dfir #cybersecurity #datasecurity #passwordrecovery #digitalforensics
Post #430 355
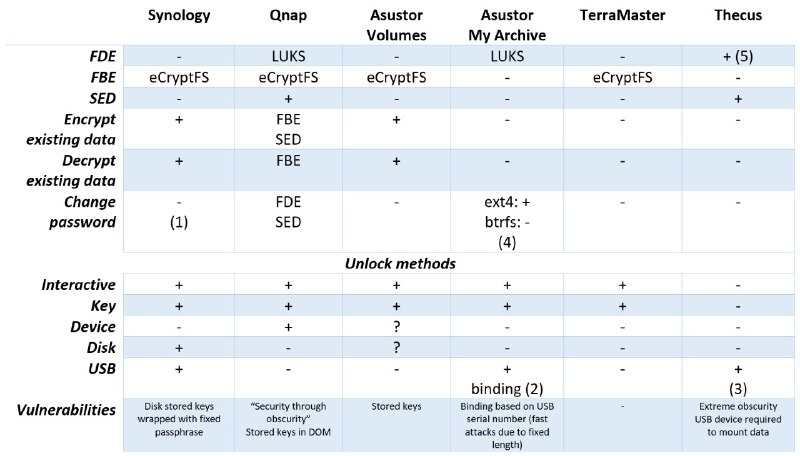
Protecting Linux and NAS Devices: LUKS, eCryptFS and Native ZFS Encryption Compared

Many Linux distributions including those used in off the shelf Network Attached Storage (NAS) devices have the ability to protect users’ data with one or more types of encryption. Full-disk and folder-based encryption options are commonly available, each with its own set of pros and contras. The new native ZFS encryption made available in OpenZFS 2.0 is designed to combine the benefits of full-disk and folder-based encryption without the associated drawbacks. In this article, we’ll compare the strengths and weaknesses of LUKS, eCryptFS and ZFS encryption.

👉 https://blog.elcomsoft.com/2021/11/protecting-linux-and-nas-devices-luks-ecryptfs-and-native-zfs-encryption-compared/

#encryption #linux #luks #ecryptfs #nas #zfs
Post #426 403
Using a Trusted Device for iCloud Authentication

To perform an iCloud extraction, a valid password is generally required, followed by solving the two-factor authentication challenge. If the user’s iPhone is everything that you have, the iCloud password may not be available. By using a trusted device, one can gain unrestricted access to everything that is stored in the user’s iCloud account. This article gives a comprehensive walkthrough on this alternative authentication method.

👉 https://blog.elcomsoft.com/2021/10/using-a-trusted-device-for-icloud-authentication/

#dfir #ios #cloudsecurity #cloudforensics
Post #425 373
iCloud Extractions Without Passwords and Tokens: When a Trusted Device is Enough

A lot of folks (and even some law enforcement experts) are looking for a one-click solution for mobile extractions and data decryption. Unfortunately, in today’s day and age there are no ‘silver bullet’ solutions. In the days of high-tech mobile devices and end-to-end encryption one must clearly understand the available options, and plan their actions accordingly. The time of ‘snake oil’ exploits is long gone. The modern world of mobile forensics is complex, and your actions will depend on a lot of factors. Today, we’re going to make your life a notch more complex by introducing a new iCloud authentication option you’ve never heard of before.

👉 https://blog.elcomsoft.com/2021/10/icloud-extractions-without-passwords-and-tokens-when-a-trusted-device-is-enough/

#ios #icloud #2fa #dfir #cloudsecurity #cloudforensics
Post #424 342
ElcomSoft Phone Breaker 10 adds device-based iCloud authentication

Elcomsoft Phone Breaker 10 adds the ability to use a trusted iOS device to authenticate iCloud extraction. Every type of data becomes extractable including end-to-end encrypted data, and no password is required.

👉 https://www.elcomsoft.com/news/795.html

#ios #dfir #cloudforensics #2fa #cloudsecurity
Post #423 455
Cloud Forensics: the New Reality

The majority of mobile devices today are encrypted throughout, making extractions difficult or even impossible for major platforms. Traditional attack vectors are becoming a thing of the past with encryption being moved into dedicated security chips, and encryption keys generated on first unlock based on the user’s screen lock passwords. Cloud forensics is a great alternative, often returning as much or even more data compared to what is stored on the device itself.

👉 https://blog.elcomsoft.com/2021/09/cloud-forensics-the-new-reality/

#icloud #iphone #cloudforensics #iossecurity #mobileforensics
Post #422 450
How to Put an iOS Device with Broken Buttons in DFU Mode

Switching the iPhone into DFU mode is frequently required during the investigation, especially for older devices that are susceptible to checkm8 exploit. For newer devices that are locked with an unknown passcode or disabled one can still learn something about the device through DFU (in particular, the bootloader version, which points to the version of iOS installed on the device). However, switching to DFU requires a sequence of key presses on the device with precise timings. If the device is damaged and one or more keys are not working correctly, entering DFU may be difficult or impossible. In this guide, we offer an alternative.

👉 https://blog.elcomsoft.com/2021/09/how-to-put-an-ios-device-with-broken-buttons-in-dfu-mode/

#apple #dfir #iphone
Post #421 391
Forensic Implications of Sleep, Hybrid Sleep, Hibernation, and Fast Startup in Windows 10

When analyzing connected computers, one may be tempted to pull the plug and bring the PC to the lab for in-depth research. This strategy carries risks that may overweigh the benefits. In this article we’ll discuss what exactly you may be losing when pulling the plug.

👉 https://blog.elcomsoft.com/2021/09/forensic-implications-of-sleep-hybrid-sleep-hibernation-and-fast-startup-in-windows-10/

#windows10 #bitlocker #diskencryption #truecrypt
Post #420 450
Elcomsoft iOS Forensic Toolkit 7.03 simplifies agent sideloading in macOS, improves support for legacy devices

In this build, we have made significant improvements to the handling of legacy (32-bit) iOS devices such as the iPhone 5 and 5c. Most importantly, we have nailed all the iPhone 5c physical acquisition issues. This model features a slightly different encryption method compared to that used in the iPhone 5. In addition, we’ve encountered some rare cases where the keychain header manifests a non-standard version number, and so iOS Forensic Toolkit would fail to decrypt the keychain. This has been fixed as well.

Next, we have improved jailbreak detection and handling for legacy models, which is particularly relevant for the iPhone 4s extraction. Since the iPhone 4s is still missing a working checkm8 implementation, the extraction options are currently limited to jailbreaking with subsequent file system and keychain extraction.

👉 https://www.elcomsoft.com/news/792.html

#ios #mobileforensics #macOS
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →