TGViewer
Channel Public Channel
Elcomsoft

Elcomsoft

@elcomsoft

Elcomsoft official channel is the place where you can find news, events and the latest updates of our products.

website: elcomsoft.com
twitter: twitter.com/elcomsoft
youtube: youtube.com/c/ElcomsoftCompany
blog: blog.elcomsoft.com
t.me/elcomsoftru
Subscribers
547
Photos
573
Videos
1
Links
458

Showing posts older than #400 · Back to latest

Older Posts 18 shown
Post #397 458
Breaking VeraCrypt: Obtaining and Extracting On-The-Fly Encryption Keys

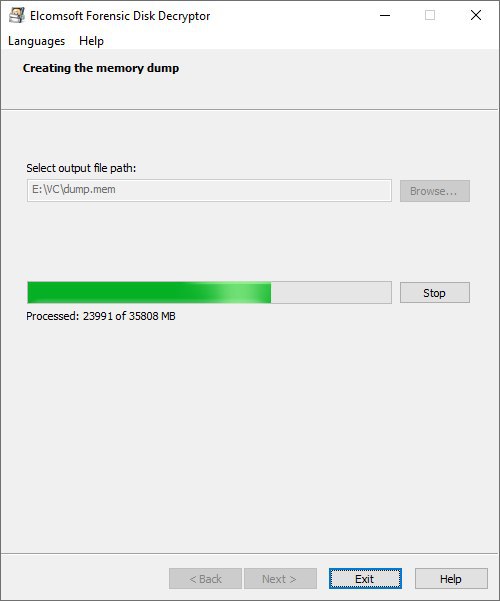
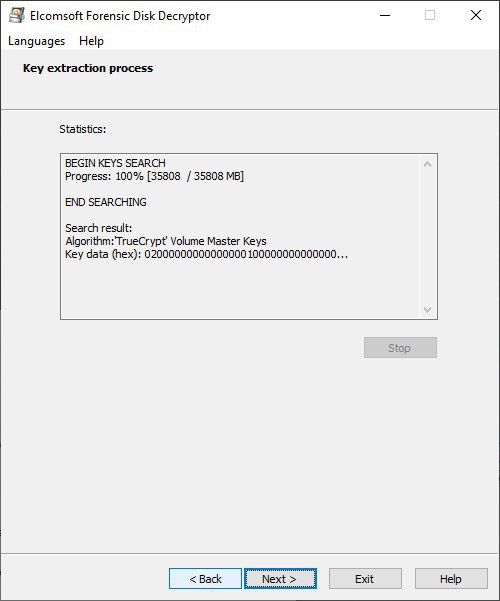
Released back in 2013, VeraCrypt picks up where TrueCrypt left off. Supporting more encryption algorithms, more hash functions and a variable number of hash iterations, VeraCrypt is the default choice for the security conscious. VeraCrypt has no known weaknesses except one: once the encrypted disk is mounted, the symmetric, on-the-fly encryption key must be kept in the computer’s RAM in order to read and write encrypted data. A recent change in VeraCrypt made OTF key extraction harder, while the latest update to Elcomsoft Forensic Disk Decryptor attempts to counter the effect of the change. Who is going to win this round?

👉 https://blog.elcomsoft.com/2021/06/breaking-veracrypt-obtaining-and-extracting-on-the-fly-encryption-keys/

#veracrypt #diskencryption #fde #otfekeys #truecrypt
Post #396 393
Forensic Disk Decryptor 2.18 extracts VeraCrypt on-the-fly encryption keys

Elcomsoft Forensic Disk Decryptor is updated to support RAM imaging and extraction of on-the-fly encryption keys in recent versions of VeraCrypt, the most popular TrueCrypt successor. The keys are extracted for all encryption configurations.

👉 https://www.elcomsoft.com/news/787.html

📝 Release Notes (PDF)

#veracrypt #diskencryption #desktopforensic #digitalsecurity
Post #395 398
Password Crackers’ Gold Mine: Browser Passwords

How to break ‘strong’ passwords? Is there a methodology, a step by step approach? What shall you start from if your time is limited but you desperately need to decrypt critical evidence? We want to share some tips with you, this time about the passwords saved in the Web browsers on most popular platforms.

👉 https://blog.elcomsoft.com/2021/06/password-crackers-gold-mine-browser-passwords/

#browser #passwords #passwordbreaker #cybersecurity #itsecurity #digitalforensics
Post #393 393
The Inception of Elcomsoft Phone Breaker

It’s been 10 years since we have released one of our flagship products, Elcomsoft Phone Breaker. The first version appeared in April 2011, and was named “iPhone Password Breaker”. Since then, we made tons of improvements. The tool lost the “iPhone” designation, and the “Password” part was dropped from its name because it was no longer limited to iPhones or passwords. Today, the tool can offer unmatched features for the mobile forensic specialists.

👉 https://blog.elcomsoft.com/2021/05/the-inception-of-elcomsoft-phone-breaker/

#iphone #ios #icloud #mobileforensics
Post #392 410
Forensically Sound checkm8 Based Extraction of iPhone 5s, 6, 6s and SE

Back in 2019, independent researcher axi0mX has developed a ground-breaking exploit. Targeting a vulnerability in the bootloader of several generations of iOS devices, checkm8 made it possible to obtain BootROM code execution and perform forensic analysis on a long list of devices running a wide range of iOS versions. In this article, we’ll talk about the forensic use of checkm8 with iOS Forensic Toolkit.

checkm8 is widely accepted in the mobile forensic community. Multiple solutions exist, but none of them are perfect, and most aren’t even trying. Our solution works entirely in RAM; it does not boot the OS installed on the device, and does not touch the system partition. There won’t be a trace left on the iPhone extracted with iOS Forensic Toolkit, not a single log entry and not even a changed timestamp.

👉 https://blog.elcomsoft.com/2021/05/checkm8-based-extraction-of-iphone-5s-6-6s-and-se/

#iphone #ios #checkm8 #dfir #EIFT
Post #391 354
Guide: Forensically Sound Extraction of iPhone 5s, 6, 6s and SE with checkm8 Exploit

The previous publication talks about the basics of using the bootloader-level exploit for extracting iOS devices. In this article, we are posting a comprehensive step-by-step guide of using the new checkm8 capability of iOS Forensic Toolkit for performing forensically sound extractions of a range of Apple devices.

👉 https://blog.elcomsoft.com/2021/05/guide-forensically-sound-extraction-of-iphone-5s-6-6s-and-se-with-checkm8-exploit/

#iphone #ios #mobileforensics #checkm8 #dfir #EIFT
Post #390 310
The File System Dirty Bit

In older iPhones, the ‘file system dirty’ flag indicates unclean device shutdown, which affects the ability to perform bootloader-level extractions of Apple devices running legacy versions of iOS (prior to iOS 10.3 released in March 2017). As such, the “file system dirty” flag must be cleared before the extraction. In this article we discuss the very different forensic implications of this flag if it is set on the Data or System partitions.

👉 https://blog.elcomsoft.com/2021/05/the-file-system-dirty-bit/

#iphone #ios #mobileforensics #filesystem
Post #389 326
iOS Forensic Toolkit 8.0 beta brings forensically-sound checkm8 extraction for select iPhone & iPad models

Elcomsoft iOS Forensic Toolkit 8.0 beta for Mac brings support for forensically sound, RAM-based checkm8 extraction, enabling full file system extraction and keychain decryption from a wide range of Apple devices.

Elcomsoft iOS Forensic Toolkit 8.0 beta for Mac offers forensically sound extraction of iPhone 5s, iPhone 6, 6 Plus, 6s, 6s Plus, and iPhone SE (1.Gen) devices with a known or empty screen lock passcode. Instead of deriving from the base offered by the checkra1n jailbreak, our solution is derived directly from the checkm8 exploit. The patching of the device is performed completely in the RAM, and the operating system installed on the device is left untouched and is not used during the boot process.

👉 https://www.elcomsoft.com/news/786.html

#iphone #checkm8 #ios #mobileforensics #EIFT #ipad
Post #388 324
A Tale of One iPhone Backup Password

Have an iPhone backup but cannot get around the password protection? I have a story to share. I was recently contacted by an old partner from the other side of the world who asked for assistance in an urgent case. He had an iTunes-style backup of a device full of critical evidence, but the password locked him out of the data.

👉 https://blog.elcomsoft.com/2021/05/iphone-backup-password-the-story/

#passwords #passwordsecurity #cybersecurity #ios #iphone #mobileforensics #dfir #iphonebackup
Post #387 408
Our Guidelines For The World Password Day

There was a 3-fold increase in identity theft and more than 2-fold increase in phishing attacks registered in 2020 compared to 2019 according to IC3 report. A whopping 50 – 81% of attacks (depending on who you read) are targeting both corporate and private sectors to steal users’ login credentials; that is, passwords. No matter what changes happen in data security, passwords remain the most wide-spread means of protection.

Today we would like to share our list of must-dos when using password protection. So, here are our recommendations for better password habits – not that we are going to discover America here, but it will help you to brush up your current security habits.

👉 https://blog.elcomsoft.com/2021/05/our-guidelines-for-the-world-password-day/

#worldpasswordday #passwords #passwordsecurity #cybersecurity
Post #386 468
Elcomsoft blog turns 12

Our blog is 12 years old. Twelve years back, we launched our blog as a tool to keep our customers updated about the new releases of our tools and give insight information about the technologies empowering our products under the hood. Today, we want to share the articles that gained the most attention in the last 365 days.

👉 https://www.elcomsoft.com/news/785.html

🏆 We also encourage you to nominate our blog in the Forensic 4:cast Awards 2021, in the category DFIR Blog of the Year: https://forensic4cast.com/2021/03/2021-forensic-4cast-awards-nominations-are-open/

#infosecurity #anniversary
Post #385 418
Elcomsoft Wireless Security Auditor supports NVIDIA Ampere boards

Wireless Security Auditor 7.40 adds support for NVIDIA’s latest RTX 3000-series boards based on the Ampere architecture. By using the latest NVIDIA cards, the new release greatly speeds up the recovery process, improving the chance of successful attacks.

📝 Release notes (in PDF)

👉 https://www.elcomsoft.com/news/784.html

#nvidia #wifi #passwords #passwordsecurity #pentest
Post #384 432
ElcomSoft extracts passwords from instant messengers

Advanced IM Password Recovery received an update, adding support for the latest versions of a large number of instant messaging apps. Version 4.91 can now extract account passwords from the newest releases of PalTalk, Pigin, Psi Jabber client, Gadu-Gadu, Gajim, Trillian, BigAnt, and Brosix instant messengers, as well as backup and restore Skype passwords.

👉 https://www.elcomsoft.com/news/783.html

#skype #paltalk #trillian #passwords #authentication #messengers
Post #383 414
Elcomsoft breaks RAR5 and 7Zip passwords

We updated Elcomsoft Advanced Archive Password Recovery 4.60 with support for additional formats, and implemented a new, faster engine for dictionary attacks. The update brought compatibility with RAR5 and 7Zip formats, and enabled multithreaded dictionary attacks.

👉 https://www.elcomsoft.com/news/782.html

#passwords #zip #7zip #rar #rar5 #archive #passwordrecovery
Post #381 470
Supporting Sage 50 Accounting and Sage 50cloud Accounts

Advanced Sage Password Recovery (ASAPR) received an update, adding support for the latest versions of the apps. The tool can now instantly recover or reset passwords to the latest versions of Sage 50 (Peachtree) Accounting 2021 and Sage 50cloud Accounts.

👉 https://www.elcomsoft.com/news/781.html

#sage #peachtree #password #passwordreset
Post #380 530
Breaking the iPhone 12: Forensic Extraction of iOS 14 Devices

iOS Forensic Toolkit 7.0 brings low-level extraction support for the latest generation of Apple devices. This includes the entire range of iPhone 12 models as well as all other devices capable of running iOS 14.0 to 14.3. Learn how to image the latest iPhone models without a jailbreak.

👉 https://blog.elcomsoft.com/2021/03/breaking-the-iphone-12-forensic-extraction-of-ios-14-devices/

#mobileforensics #ios14 #iphone12 #agent #eift #toolkit
Post #379 448
Elcomsoft iOS Forensic Toolkit 7.0: low-level extraction without a jailbreak for iPhone 12, iOS 14

The new Elcomsoft iOS Forensic Toolkit 7.0 brings the ability to perform low-level, jailbreak-free extraction of all iPhone models running iOS 14 through 14.3, including the newest range of iPhone 12 devices. Using an Apple Developer account is strongly recommended.

📝 Release notes (PDF)

👉 https://www.elcomsoft.com/news/780.html

#mobileforensics #ios14 #iphone12 #agent #eift
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →