TGViewer
Channel Public Channel
Elcomsoft

Elcomsoft

@elcomsoft

Elcomsoft official channel is the place where you can find news, events and the latest updates of our products.

website: elcomsoft.com
twitter: twitter.com/elcomsoft
youtube: youtube.com/c/ElcomsoftCompany
blog: blog.elcomsoft.com
t.me/elcomsoftru
Subscribers
547
Photos
573
Videos
1
Links
458

Showing posts older than #359 · Back to latest

Older Posts 20 shown
Post #358 298
Elcomsoft vs. Hashcat Part 4: Case Studies

This is the final part of the series of articles comparing Elcomsoft Distributed Password Recovery with Hashcat. We’ve already compared the features, the price and performance of the two tools. In this study, we tried breaking passwords to several common formats, including Word document, an encrypted ZIP archive, and a VeraCrypt container. We summarized our experiences below.

👉 https://blog.elcomsoft.com/2020/12/elcomsoft-vs-hashcat-part-4-case-studies/

#gpu #passwords #passwordrecovery #veracrypt #zip #hashcat
Post #357 344
How to Remove The iPhone Passcode You Cannot Remove

From time to time, we stumble upon a weird issue that interferes with the ability to install a jailbreak. One of such problems appearing literally out of the blue is the issue of being unable to remove the screen lock password on some iPhone devices. What could be the reason and how to work around the issue? Read along to find out!

👉 https://blog.elcomsoft.com/2020/12/how-to-remove-the-iphone-passcode-you-cannot-remove/

#iphone #passcode #screenlock #eift #jailbreak #mobileforensics
Post #356 334
iOS Extraction Without a Jailbreak: iOS 9 through iOS 13.7 on All Devices

After adding jailbreak-free extraction for iOS 13.5.1 through 13.7, we now support every Apple device running any version of iOS from 9.0 through 13.7 with no gaps or exclusions. For the first time, full file system extraction and keychain decryption are possible on all devices running these iOS versions.

👉 https://blog.elcomsoft.com/2020/12/ios-extraction-without-a-jailbreak-ios-9-through-ios-13-7-on-all-devices/

#ios #iphone #dfir #EIFTagent #mobileforensics #nojailbreak
Post #355 289
The Evolution of iOS Acquisition: Jailbreaks, Exploits and Extraction Agent

The past two years have become a turning point in iOS acquisition. The release of a bootrom-based exploit and the corresponding jailbreak made BFU acquisition possible on multiple devices regardless of security patches. Another exploit covers the entire iOS 13 range on all devices regardless of their hardware revision. ElcomSoft developed a jailbreak-free extraction method for the entire iOS 9.0-13.7 range. Let’s see what low-level acquisition options are available today, and when to use what.

👉 https://blog.elcomsoft.com/2020/12/the-evolution-of-ios-acquisition-jailbreaks-exploits-and-extraction-agent/

#ios #iphone #mobileforensics #dfir #EIFTagent #dataextraction #jailbreak
Post #354 250
iOS Forensic Toolkit 6.60: jailbreak-free extraction for iOS 9.0 through 13.7

Elcomsoft iOS Forensic Toolkit 6.60 extends the coverage for jailbreak-free extraction from iOS 9.0 all the way through iOS 13.7, adding support to the last versions of iOS 13 ever released. The new release expands the availability of the extraction agent, adding full file system and keychain decryption support for previously unsupported versions of iOS 13.5.1 to 13.7 on all compatible iPhone and iPad devices.

📝 Release Notes (PDF)

👉 https://www.elcomsoft.com/news/774.html

#ios #iphone #mobileforensics #dfir #cybersecurity #EIFTagent #dataextraction
Post #353 240
Elcomsoft vs. Hashcat Part 3: Attacks, Costs, Performance and Extra Features

Elcomsoft Distributed Password Recovery and Hashcat support a number of different attacks ranging from brute-force all the way to scriptable, dictionary-based attacks. The costs and performance are extremely important factors. We charge several hundred dollars for what, in the end, can be done with a free tool. Which tool has better performance, and are the extra features worth the price premium? Let’s check it out.

👉 https://blog.elcomsoft.com/2020/12/elcomsoft-vs-hashcat-part-3-attacks-costs-performance-and-extra-features/

#passwords #dfir #cybersecurity #datasecurity #passwordrecovery
Post #352 227
Forensically Sound Cold System Analysis

As opposed to live system analysis, experts performing the cold analysis are not dealing with authenticated user sessions. Instead, cold analysis can be viewed as an intermediary measure with live system analysis on the one end and the examination of a forensic disk image on another. Why and when would you use cold system analysis, what can you do and what benefits does it bring compared to the traditional approach? Read along to find out.

👉 https://blog.elcomsoft.com/2020/12/forensically-sound-cold-system-analysis/

#dfir #datasecurity #encryption #windows #itsecurity
Post #351 246
The ABC’s of Password Cracking: The True Meaning of Speed

When adding a new encryption format or comparing the performance of different password recovery tools, we routinely quote the recovery speed expressed in the number of passwords per second. But what is the true meaning of password recovery speeds? Do the speeds depend solely, or at all, on the encryption algorithm? What’s “military grade” encryption, and does it guarantee the security of your data? And why on Earth breaking AES-256 encryption takes so vastly different effort in different file formats? Read along to find out.

👉 https://blog.elcomsoft.com/2020/11/the-abcs-of-password-cracking-the-true-meaning-of-speed/

#passwords #passwordrecovery #dfir #digitalforensics #datasecurity #dataaccess
Post #350 274
Elcomsoft System Recovery: a Swiss Army Knife of Desktop Forensics

Accessing a locked system is always a challenge. Encrypted disks and encrypted virtual machines, encrypted files and passwords are just a few things to mention. In this article we are proposing a straightforward workflow for investigating computers in the field.

Note: you may be able to perform live system analysis if the computer being investigated is turned on. Our scenario assumes that the computer is initially powered off, or powered on and locked/inaccessible.

👉 https://blog.elcomsoft.com/2020/11/elcomsoft-system-recovery-a-swiss-army-knife-of-desktop-forensics/

#encrypteddisks #virtualmachines #passwords #livesystemanalysis
Post #349 252
Elcomsoft System Recovery update: a Swiss army knife in desktop forensics

We updated Elcomsoft System Recovery, a Windows PE-based tool to recover or reset passwords to local Windows accounts and Microsoft accounts in all versions of Windows. In this release, we offer more options for recovering the original passwords as opposed to resetting while adding a multitude of other improvements.

👉 https://www.elcomsoft.com/news/772.html

📝 Release Notes (PDF)

#encryption #virtualmachines #diskimage #passwords #dataaccess #passwordrecovery
Post #348 234
Elcomsoft vs. Hashcat Part 2: Workflow, Distributed and Cloud Attacks

The user interface is a major advantage of Elcomsoft tools. Setting up attacks in Elcomsoft Distributed Password Recovery is simpler and more straightforward compared to the command-line tool. In this article, we’ll talk about the general workflow, the use and configuration of distributed and cloud attacks in both products.

👉 https://blog.elcomsoft.com/2020/11/elcomsoft-vs-hashcat-part-2-workflow-distributed-and-cloud-attacks/

#dfir #edpr #hashcat #passwordrecovery #datadecryption
Post #347 222
Elcomsoft vs. Hashcat: Addressing Feedback

After publishing the first article in the series, we received numerous comments challenging our claims. We carefully reviewed every comment, reread and reevaluated our original article. Elcomsoft vs. Hashcat Rev.1.1 is here.

👉 https://blog.elcomsoft.com/2020/11/elcomsoft-vs-hashcat-addressing-feedback/

#passwords #hashcat #cybersecurity #passwordcracking #dfir #gpu
Post #346 276
Extracting Evidence from iPhone Devices: Do I (Still) Need a Jailbreak?

by Vladimir Katalov

If you are familiar with iOS acquisition methods, you know that the best results can be obtained with a full file system acquisition. However, extracting the file system may require jailbreaking, which is a risky and not always permitted. Are there any reasons to use jailbreaks for extracting evidence from Apple devices?

👉 https://blog.elcomsoft.com/2020/11/extracting-evidence-from-iphone-devices-do-i-still-need-a-jailbreak/

#jailbreak #ios #mobilesecurity #dfir #iphone #checkra1n
Post #345 298
Elcomsoft vs. Hashcat Part 1: Hardware Acceleration, Supported Formats and Initial Configuration

Hashcat is a great, free tool competing head to head with the tools we make. We charge several hundred dollars for what, in the end, can be done with a free tool. What are the reasons for our customers to choose ElcomSoft products instead of Hashcat, and is the expense justified? We did our best to compare the two tools to help you make the informed decision.

👉 https://blog.elcomsoft.com/2020/11/elcomsoft-vs-hashcat-part-1-hardware-acceleration-supported-formats-and-initial-configuration/

#encryption #passwords #gpucomputing #hashcat #bruteforce
Post #344 754
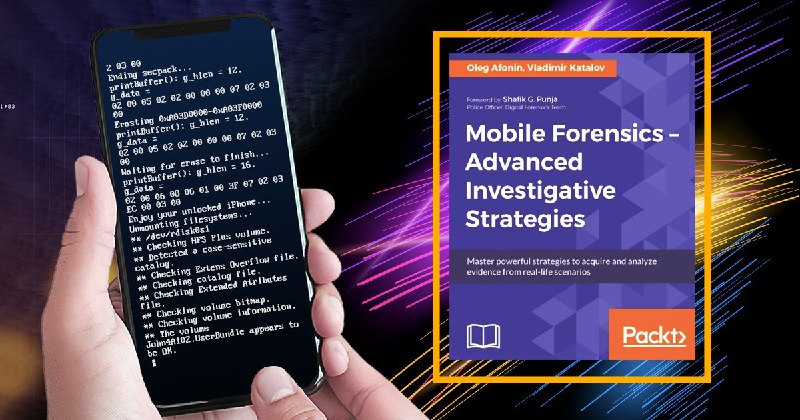
Mobile Forensics – Advanced Investigative Strategies

Four years ago, we published our first book: Mobile Forensics – Advanced Investigative Strategies. We are really proud of this achievement. Do you want to know the story behind it and what’s changed since then in mobile and cloud forensics? Here are some insides (but please do not tell anyone!)

👉 https://blog.elcomsoft.com/2020/11/mobile-forensics-advanced-investigative-strategies/

#dfir #mobileforensics #cybersecurity #book #digitalforensics
Post #343 302
Apple Watch Forensics Reloaded

Is it possible to extract any data from an Apple Watch? It’s relatively easy if you have access to the iPhone the device is paired to, or if you have a backup of that iPhone. But what if the watch is all you have? If there is no paired iPhone, no backup and no iCloud credentials, how can you connect the Apple Watch to the computer, and can you backup the watch?

👉 https://blog.elcomsoft.com/2020/11/apple-watch-forensics-reloaded/

#ios #mobilesecurity #dfir #mobileforensics #applewatch
Post #342 279
Elcomsoft and The Case of the Apple iPad

For almost a decade, if not longer, I have collaborated with Vladimir Katalov on various digital forensics research topics. He has always been a great source of guidance, especially on iOS related challenges. When he offered me a standing invitation to post on the Elcomsoft Blog, I felt very humbled and honored to be given the opportunity to post on the ElcomSoft Blog, and I would like to thank the ElcomSoft team. This article has also been prepared together, with Vladimir Katalov.

👉 https://blog.elcomsoft.com/2020/11/elcomsoft-and-the-case-of-the-apple-ipad/

#ios #ipad #mobileforensics #dfir #elcomsoft_agent
Post #341 304
iOS 14.2, iOS 12.4.9, the Updated checkra1n 0.12 Jailbreak and File System Extraction

It’s been a week since Apple has released iOS 14.2 as well as iOS 12.4.9 for older devices. Just a few days later, the developers updated the checkra1n jailbreak with support for new devices and iOS versions. What does that mean for iOS forensics? Let’s have a look; we have done some testing, and our discoveries were somewhat unexpected.

👉 https://blog.elcomsoft.com/2020/11/ios-14-2-ios-12-4-9-the-updated-checkra1n-0-12-jailbreak-and-file-system-extraction/

#mobilesecurity #dfir #checkra1n #jailbreak #ios14 #elcomsoftiosforensictoolkit
Post #340 307
Protecting iMessage Communications

How secure are your chats in your favorite instant messenger? Can someone intercept and read your secret conversations, and can you do something about it? Apple users have access to the highly popular instant messaging system, the iMessage. But how secure it really is? Let’s find out.

👉 https://blog.elcomsoft.com/2020/11/protecting-imessage-communications/

#mobilesecurity #chats #dfir #imessage #icloud
Post #339 316
Breaking Intuit Quicken and QuickBooks Passwords in 2021

Intuit Quicken is one of the oldest tools of its kind. Over the years, Quicken had become the de facto standard for accounting, tax reporting and personal finance management in North America.

Finances is an extremely sensitive area that demands adequate protection of the user data. However, prior to 2003, Quicken employed a weak protection scheme that allowed the intruder to break in instantly even if the password was set. Since Quicken 2003, the tool gained the ability to encrypt data. From now on, the password must be brute-forced in order to gain access to the encrypted data.

👉 https://blog.elcomsoft.com/2020/11/breaking-intuit-quicken-and-quickbooks-passwords-in-2021/

#quicken2020 #intuit #quickbooks #passwordrecovery #passwordsecurity
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →