TGViewer
Channel Public Channel
Elcomsoft

Elcomsoft

@elcomsoft

Elcomsoft official channel is the place where you can find news, events and the latest updates of our products.

website: elcomsoft.com
twitter: twitter.com/elcomsoft
youtube: youtube.com/c/ElcomsoftCompany
blog: blog.elcomsoft.com
t.me/elcomsoftru
Subscribers
547
Photos
574
Videos
1
Links
459

Showing posts older than #279 · Back to latest

Older Posts 20 shown
Post #278 224
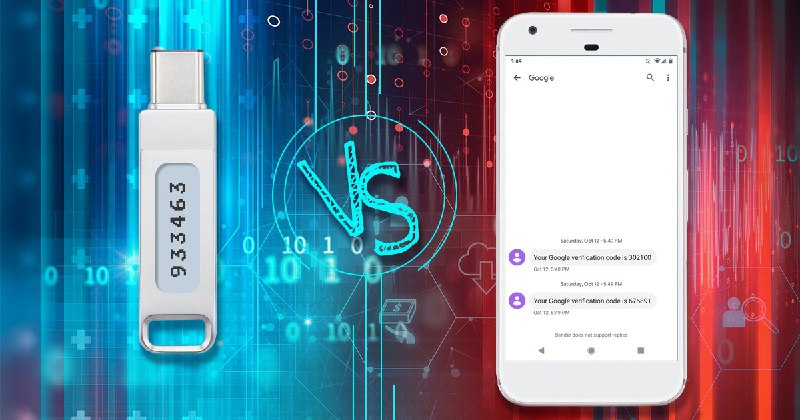
Apple Two-Factor Authentication: SMS vs. Trusted Devices

Multi-factor authentication is the new reality. A password alone is no longer considered sufficient. Phishing attacks, frequent leaks of password databases and the ubiquitous issue of reusing passwords make password protection unsafe. Adding “something that you have” to “something that you know” improves the security considerably, having the potential of cutting a chain attack early even in worst case scenarios. However, not all types of two-factor authentication are equally secure.

Let’s talk about the most commonly used type of two-factor authentication: the one based on text messages (SMS) delivered to a trusted phone number.

👉 https://blog.elcomsoft.com/2020/06/apple-two-factor-authentication-sms-vs-trusted-devices/

#2fa #itsecurity #cybersecurity #authentication #clouds #mobilesecurity #smartphone
Post #277 212
Elcomsoft iOS Forensic Toolkit 6.10: jailbreaking all the way

Elcomsoft iOS Forensic Toolkit 6.10 delivers major improvements to jailbreak-based extraction, now offering keychain acquisition and file system extraction for iOS 13.5, 13.4.1, 13.4 and 13.3.1 with unc0ver v5, as well as keychain acquisition and file system extraction for iOS 13.5 and 13.5.1 with checkra1n. Jailbreak-based acquisition engine received a major overhaul, now offering greater than ever speed and stability.

👉 https://www.elcomsoft.com/news/749.html

#jailbreak #iphone #itsecurity #unc0ver #checkra1n #keychain #mobilesecurity #dfir #mobileforensics
Post #276 208
Researching Confide Messenger Encryption

iPhone users have access to literally hundreds of instant messaging apps. These apps range all the way from the built-in iMessage app to the highly secure Signal messengers, with all stops in between. Many of the messaging apps are marketed as ‘secure’ or ‘protected’ messengers, touting end-to-end encryption and zero retention policies. We routinely verify such claims by analyzing the security of various instant messaging apps. It turned out that the degree of protection can vary greatly, having little to do with the developers’ claims. Today we’ll check out Confide, a tool advertising unprecedented level of security.

👉 https://blog.elcomsoft.com/2020/06/researching-confide-messenger-encryption/

#confide #cybersec #mobileforensics #dfir #smartphone #iphone #messenger #datasecurity
Post #275 248
checkra1n & unc0ver: How Would You Like to Jailbreak Today?

Extracting the fullest amount of information from the iPhone, which includes a file system image and decrypted keychain records, often requires installing a jailbreak. Even though forensically sound acquisition methods that work without jailbreaking do exist, they may not be available depending on the tools you use. A particular combination of iOS hardware and software may also render those tools ineffective, requiring a fallback to jailbreak. Today, the two most popular and most reliable jailbreaks are checkra1n and unc0ver. How do they fare against each other, and when would you want to use each?

👉 https://blog.elcomsoft.com/2020/06/checkra1n-unc0ver-jailbreak-today/

#checkra1n #unc0ver #jailbreak #smartphone #mobileforensics #iOS #iPhone
Post #274 269
Forensic Disk Decryptor 2.12 and System Recovery 7.04 Display File System Data, Expand VeraCrypt Support

Elcomsoft releases two product updates. Forensic Disk Decryptor 2.12 can display file system data and adds VeraCrypt support for GPT partitions, while System Recovery 7.04 can discover plaintext passwords for cached domain credentials and also shows file system data.

👉 https://www.elcomsoft.com/news/748.html

#fde #veracrypt #encryption #truecrypt #desktopforensic #cybersecurity
Post #273 248
Full File System and Keychain Acquisition with unc0ver jailbreak: iOS 13.1 to 13.5

The unc0ver v5 jailbreak has been available for a while now. It supports the newest versions of iOS up to and including iOS 13.5, and this is fantastic news for DFIR community, as it allows extracting the full file system and the keychain when acquiring the newest latest iPhone models such as the iPhone 11 and 11 Pro, and SE 2020. In this article, I’ll talk about the unc0ver jailbreak, the installation and usage for the purpose of file system extraction, and discuss the differences between jailbreak-based and jailbreak-free extraction.

👉 https://blog.elcomsoft.com/2020/05/full-file-system-and-keychain-acquisition-with-unc0ver-jailbreak-ios-13-1-to-13-5/

By Vladimir Katalov

#uncover #ios #iphone #iOS135 #cybersecurity #itsecurity #mobileforensics
Post #272 206
Clearing Confusion About our Password Recovery Tools

There is a bit of confusion about our software designed to allow breaking into password-protected systems, files, documents, and encrypted containers. We have as many as three products (and five different tools) dealing with the matter: Elcomsoft Forensic Disk Decryptor (with an unnamed memory dumping tool), Elcomsoft System Recovery and Elcomsoft Distributed Password Recovery, which also includes Elcomsoft Hash Extractor as part of the package. Let’s briefly go through all of them. Hopefully it will help you select the right product for your needs and save time in your investigation.

👉 https://blog.elcomsoft.com/2020/05/clearing-confusion-about-our-password-recovery-tools/

By Oleg Afonin

#password #passwordrecovery #encryption #itsecurity #cybersecurity #dataaccess #dfir #difitalforensics
Post #271 206
iOS Jailbreaks, SSH, and root Password

Modern jailbreaks, in addition to removing several iOS restrictions (for example, disabling signature verification, escalating privileges or bypassing the sandbox), allow obtaining low-level access to the device’s file system. This allows connecting to an iOS device via SSH and gaining almost unlimited access to the system. Some jailbreaks install an OpenSSH (or dropbear) server immediately as they are installed. If not, then SSH can be installed manually from the Cydia repository (OpenSSH package). In this article, I’ll discuss several issues related to SSH, including the following.

- How to understand if SSH is installed and working on the device?
- How to change the root password?
- How to reset the root password to its default value if one is unknown?

👉 https://blog.elcomsoft.com/2020/05/ios-jailbreaks-ssh-and-root-password/

#mobileforensics #ios #iphone #smartphone #jailbreak #password #ssh
Post #270 197
iOS Forensic Toolkit 6.0: jailbreak-free extraction for iOS 11 through 13.4.1

Elcomsoft iOS Forensic Toolkit 6.0 offers direct, forensically sound extraction for Apple devices running all versions of iOS from iOS 11 through iOS 13.4.1 without a jailbreak. This release adds full file system extraction support for the latest iOS builds including iOS 13.3.1, 13.4, and 13.4.1 for the iPhone 6s, 7, 8, X, Xr/Xs, 11, and 11 Pro generation devices (including the corresponding Plus and Max versions), as well as latest iPhone SE.

👉 https://www.elcomsoft.com/news/747.html

📝 Release Notes (PDF)

#ios #iphone #mobileforensics #dfir #mobilesecurity #itsecurity #dataextraction
Post #269 191
Full File System Extraction for iOS 13.3.1, 13.4 and 13.4.1

Elcomsoft iOS Forensic Toolkit 6.0 is out, adding direct, forensically sound extraction for Apple devices running some of the latest versions of iOS including iOS 13.3.1, 13.4 and 13.4.1. Supported devices include the entire iPhone 6s, 7, 8, X, Xr/Xs, 11, and 11 Pro (including Plus and Max versions) range, the iPhone SE, and corresponding iPad models. Let’s review the changes and talk about the new acquisition method in general.

Agent-based extraction: the technology

For a long time, we relied on publicly available jailbreaks to perform full file system and keychain acquisition. That is not a forensically sound method as there are risks (though minimal) to brick the device. Even if you are using the rootless jailbreak, some significant changes to the system are still being made, and they cannot be always rolled back.

👉 https://blog.elcomsoft.com/2020/05/full-file-system-acquisition-for-ios-13-3-1-13-4-and-13-4-1/

#ios #iphone #dfir
Post #268 235
Tighter Control over Personal Information with Attacks on Encryption Metadata


When attacking a password, the traditional forensic workflow requires uploading the entire encrypted file or document into a password recovery tool. This approach, while simple and intuitive, has one major drawback if you are using remote computers or cloud instances to perform an attack. If the remote computer is compromised, the entire file or document is leaked complete with its (still encrypted) contents. Learn how to overcome this issue and perform remote attacks without the reason of leaking personal information.

Encryption Metadata

The solution to the problem is obvious: use just the required minimum of information to run the attack. In the case of document passwords, this means...

👉 https://blog.elcomsoft.com/2020/05/tighter-control-over-personal-information-with-attacks-on-encryption-metadata/

#hashextractor #passwords #itsecurity #computersecurity #datasecurity #digitalforensics #dfir #cloudcomputing
Post #267 223
Unlocking BitLocker: Can You Break That Password?

BitLocker is one of the most advanced and most commonly used volume encryption solutions. BitLocker is well-studied and extensively documented solution with few known vulnerabilities and a limited number of possible vectors of attack. BitLocker volumes may be protected with one or more protectors such as the hardware-bound TPM, user-selectable password, USB key, or combination thereof. Attacking the password is only possible in one of these cases, while other protectors require a very different set of attacks. Learn how to approach BitLocker volumes depending on the type of protector.

👉 https://blog.elcomsoft.com/2020/05/unlocking-bitlocker-can-you-break-that-password/

#bitlocker #computersecurity #datadecryption #password #hash #hashextrctor #diskecnryption #cybersecurity
Post #266 222
Elcomsoft Distributed Password Recovery 4.21 updated with stronger privacy control, breaks Mozilla Firefox master password

Elcomsoft Distributed Password Recovery 4.21 adds support for Mozilla Firefox master passwords, enabling accelerated attacks on the Firefox password storage database. In addition, we offer stricter privacy control, enabling EDPR to perform attacks on tiny files that only contain encryption metadata extracted from Microsoft Office, Open Document, Apple iWork, Hancom and Adobe Acrobat documents without any of the actual content.

👉 https://www.elcomsoft.com/news/746.html

📝 Release notes (PDF)

#firefox #hash #hashextractor #cloudcomputing #microsoftoffice #openoffice #hancom #adobe #passwordcracking #itsecurity #digitalforensics
Post #265 227
All mobile and cloud forensic practitioners are welcome to refresh their skills and get another professional overview of the current situation in iOS, Android, and Windows forensics allowing you to effectively retrieve and analyze mobile and cloud data. Learn the latest forensic techniques to investigate mobile devices across various mobile platforms with the help of both open source and paid solutions. The fourth edition of Practical Mobile Forensics written by our colleagues offers to explore the real-life scenarios. Thank you guys for using our tools in it!

👉 https://www.amazon.com/dp/183864752X/

#iOS #security #iphone #mobileforensics #macos #informationtechnology #digitalforensics #dfir #cloudsecurity
Post #264 247
Apple vs. Law Enforcement: poker face?

“We shouldn’t ask our customers to make a tradeoff between privacy and security. We need to offer them the best of both. Ultimately, protecting someone else’s data protects all of us.” Guess who said that? The answer is at the end of the article. In the meantime, we keep talking of iPhone and iOS security, following up the Apple vs. Law Enforcement – iOS 4 through 13.5 article. This time we are about to discuss some other aspects of iOS security.

The Exploits

I think you know about the renewed Apple Security Bounty program. Participants can earn up to $100,000 for a new lock screen bypass, and up to $250,000 for user data extraction.

👉 https://blog.elcomsoft.com/2020/05/apple-vs-law-enforcement-poker-face/

#mobileforensics #apple #lawenforcement #encryption #privacy #exploits #grayshift #cellebrite
Post #263 215
Apple vs. Law Enforcement – iOS 4 through 13.5

Today’s smartphones are a forensic goldmine. Your smartphone learns and knows about your daily life more than everything and everyone else. It tracks your location and counts your footsteps, AI’s your pictures and takes care of your payments. With that much data concentrated in a single device, it is reasonable to expect the highest level of protection. In this article, we’ll review the timeline of Apple’s measures to protect their users’ data and the countermeasures used by the law enforcement. This time no cloud, just pure device forensics.

👉 https://blog.elcomsoft.com/2020/05/apple-vs-law-enforcement-ios-4-through-13-5/

#ios #iphone #apple #encryption #protection #itsecurity #cybersecurity #mobileforensics #dfir #mobilesecurity
Post #262 223
Working Around the iPhone USB Restricted Mode

The USB restricted mode was introduced in iOS 11.4.1, improved in iOS 12 and further strengthened in iOS 13. The USB restrictions are a real headache for iPhone investigators. We’ve discovered a simple yet effective trick to fool it in some cases, but currently it securely protects the iPhones from passcode cracking and BFU (Before First Unlock) extractions. However, there is a trick allowing you to obtain some information from devices with disabled USB interface. Learn how to use this trick with the recently updated iOS Forensic Toolkit.

👉 https://blog.elcomsoft.com/2020/05/iphone-usb-restricted-mode-workaround/

#ios #iphone #ecx #dataextraction #mobileforensics #dfir #usbrestrictedmode #mobilesecurity
Post #261 210
iOS Acquisition Reloaded

The new build of iOS Forensic Toolkit is out. This time around, most of the changes are “internal” and do not add much functionality, but there is a lot going on behind the scenes. In this article, we will describe in details what is new and important, and how it’s going to affect you. We’ll share some tips on how to use the software in the most effective way, making sure that you extract all the data from iOS devices in the most forensically sound possible.

👉 https://blog.elcomsoft.com/2020/05/ios-acquisition-reloaded/

#eift #iphone #ios #mobilesecurity #mobileforensics #dfir #itsecurity #smartphone #dataextraction #ElcomsoftAgent #decryption
Post #260 208
iOS Forensic Toolkit 5.50: iPhone extraction simplified

Elcomsoft iOS Forensic Toolkit 5.50 features a new communication channel empowering the tool’s acquisition engine. The newly designed communication channel offers faster and more robust extractions and simplifies the acquisition process by removing the need of disabling wireless connectivity.

👉 https://www.elcomsoft.com/news/745.html

📝 EIFT Release Notes

#iphone #ios #dataextraction #elcomsoftagent #toolkit #iOS13.5 #mobileforensics #mobilesecurity #filesystem #keychain
Post #259 255
Google Account Access Without a Password

Cloud acquisition is one of the most common ways to obtain valuable evidence. When it comes to Google, the Google Account analysis may return significantly more data compared to the extraction of a physical Android device. However, there is one feature that is often overlooked: the ability to extract data stored in the user’s Google Account without the login and password. Let’s talk about Google authentication tokens and what they bring for the mobile forensics.

👉 https://blog.elcomsoft.com/2020/05/google-account-access-without-a-password/

#google #password #token #authentication #dataaccess #datasecurity #itsecurity #mobileforensics #cloudsecurity
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →