TGViewer
Channel Public Channel
Elcomsoft

Elcomsoft

@elcomsoft

Elcomsoft official channel is the place where you can find news, events and the latest updates of our products.

website: elcomsoft.com
twitter: twitter.com/elcomsoft
youtube: youtube.com/c/ElcomsoftCompany
blog: blog.elcomsoft.com
t.me/elcomsoftru
Subscribers
548
Photos
574
Videos
1
Links
459

Showing posts older than #171 · Back to latest

Older Posts 20 shown
Post #170 238
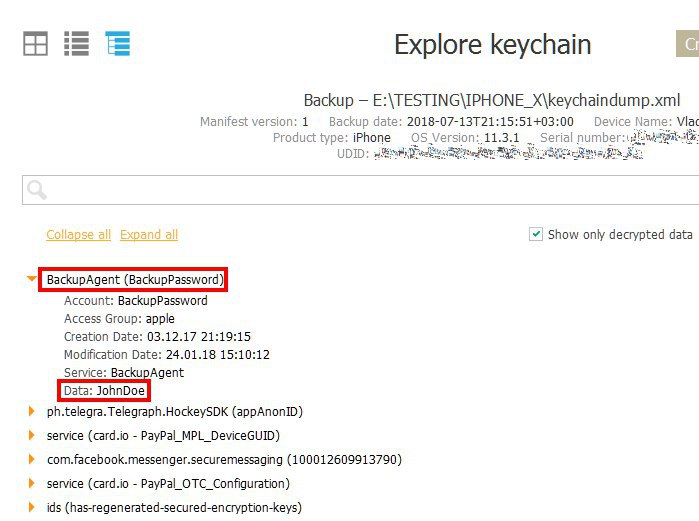
Step by Step Guide to iOS Jailbreaking and Physical Acquisition

The procedure of installing a jailbreak for the purpose of physical extraction is vastly different from jailbreaking for research or other purposes. In particular, forensic experts are struggling to keep devices offline in order to prevent data leaks, unwanted synchronization and issues with remote device management.

👉 https://blog.elcomsoft.com/2019/05/step-by-step-guide-to-ios-jailbreaking-and-physical-acquisition/

#jb #jailbreak #ios #mobileforensics #dataextraction #iphone #keychain #forensictoolkit #password #filesystem #elcomsoft #ios12 #grayshift
Post #169 226
Meet with us at DMI NATIONAL Spring Conference & Exhibition by The Investigator in Oxford, 21-22 May 2019. Our talk on Day 2, Session 1, 9.50am-10.30am: #Forensic implications of iPhone #jailbreaking, Vladimir Katalov. 👉 the-investigator.co.uk/dmi-spring-2019 #dfir #investigation #cybercrime #jb
Post #168 244
Elcomsoft Phone Viewer 4.50 adds data export support, allows evidence analysis in external tools

Elcomsoft Phone Viewer is updated to enable the exporting of digital evidence collected from iOS device backups, iCloud and file system images to Microsoft Excel. The ability to export data enables experts to continue the investigation in their forensic product of choice.

👉 https://www.elcomsoft.com/news/720.html

#dfir #iphone #ios #security #decryption #2fa #report #evidence #investigation #dataextraction
Post #167 257
You Lost Your Second Authentication Factor. Now What? What if you do know your password and your passcode but lost access to the only physical iOS device using your Apple ID and your SIM card at the same time? This could easily happen if you travel abroad and your phone is stolen together with the SIM card.

👉 https://blog.elcomsoft.com/2019/04/you-lost-your-second-authentication-factor-now-what/

#iphone #2fa #authentication #apple #iforgot #icloud #password #dataaccess #ios #verification
Post #165 270
Elcomsoft System Recovery 6.0 Extracts Hibernation Files and Data to Break Full Disk Encryption Passwords For BitLocker, PGP, TrueCrypt and VeraCrypt

The update makes it easy to process full-disk encryption by simply booting from a flash drive. The tool automatically detects full-disk encryption, extracting and saving information required to brute-force passwords to encrypted volumes. In addition, the tool can save the system’s hibernation file to the flash drive for subsequent extraction of decryption keys for accessing encrypted volumes. More 👉 https://www.elcomsoft.com/news/719.html

#BitLocker #PGP #TrueCrypt #VeraCrypt #passwords #encryption #windows #hiddendisks #crypto #code #encryptionkey
Post #164 295
Elcomsoft Explorer for WhatsApp 2.70 supports iOS 12, new Google Drive backups, gains the ability to use one-time codes delivered via an SMS or generated offline from the device Settings app. In addition, the processing time of encrypted iTunes backups is cut 4 to 5 times.

👉 https://www.elcomsoft.com/news/718.html

#whatsapp #googledrive #sms #mobileforensics #cloudforensics #backup #encryption #authentication
Post #163 298
We strive to deliver products of the best quality for desktop, mobile and cloud forensics. Vote for us and make us happy!

Vote for us at the Forensic 4:cast Awards. Nominate ElcomSoft in categories:
» DFIR Commercial Tool of the Year - Elcomsoft Phone Breaker
» DFIR Blog of the Year - Elcomsoft Blog
» DFIR Team of the Year - ELCOMSOFT

👉 https://forensic4cast.com/forensic-4cast-awards/

#digitalforensics #dfir #phonebreaker #jailbreak #rootlessjb #mobileforensics #cloudforensics #elcomsoft
Post #162 247
Achtung! 😎

Meet with us at GPEC Digital 2019, stand #D02 in CityCube Berlin, Messe Berlin, Germany, 13-14 March.

Come and learn our news! The expo is open for visitors from national and international security authorities 👮‍♂️

👉 https://www.elcomsoft.com/events.html

#police #cyber #cybersecurity #digitalforensics #cloudforensics #decryption
Post #160 250
Let’s chat at FE215, Forensics Europe Expo, London 5-6 March. We would love to share latest #elcomsoft #news!
Post #159 274
Elcomsoft Phone Viewer 4.40 shows trusted devices, adds local Apple Health support

Elcomsoft Phone Viewer receives an update to support local Apple Health data extracted from iOS local backups and file system images. In addition, the tool can now display the list of trusted devices as downloaded from Apple iCloud with Elcomsoft Phone Breaker. A passcode or system password from any trusted device can be used to decrypt iCloud Keychain and access Health data and iCloud Messages. Finally, the speed of opening encrypted iTunes backups has been significantly improved thanks to the new multi-threaded decryption engine.

https://www.elcomsoft.com/news/717.html
#crypto #decryption #iCloud #iPhone
Post #157 249
There has been a lot of noise regarding GrayKey news recently. GrayKey is an excellent appliance for iOS data extraction. As always, the devil is in the detail.

A couple of quotes first, from the company who now partners with GrayShift to bundle their mobile forensic software (one of the best on the market) with GrayKey. They do support GrayKey-extracted data as well, and here is what they say:

“From the first iPhone extraction from GrayKey we were blown away with the amount of data they recovered”

Actually, this is not exactly the case. Speaking of full file system acquisition, it’s been us who were the first on the market some 3 years ago, see Physical Acquisition for 64-bit Devices, iOS 9 Support.

Since then, we’ve been actively developing and updating iOS Forensic Toolkit, adding support for newer versions of iOS. https://blog.elcomsoft.com/2019/02/technical-and-legal-implications-of-ios-file-system-acquisition/ #iosforensics #jailbreak #iphone
Post #156 416
Physical Extraction and File System Imaging of iOS 12 Devices

The new generation of jailbreaks has arrived for iPhones and iPads running iOS 12. Rootless jailbreaks offer experts the same low-level access to the file system as classic jailbreaks – but without their drawbacks.
Learn how to install a rootless jailbreak and how to perform physical extraction with Elcomsoft iOS Forensic Toolkit.

https://goo.gl/k7EB22

#iOS #iOS12 #Apple #JailBreak #iPhone #iPad #RootlessJailBreak
Post #155 204
Elcomsoft iOS Forensic Toolkit 5.0 is a major update adding support for physical acquisition of Apple devices running iOS 12.
The tool extracts the content of the file system and decrypts passwords and authentication credentials stored in the iOS keychain.
https://goo.gl/awgqub
#iOS #iOS12 #apple #mobilesecurity
Post #152 243
Elcomsoft iOS Forensic Toolkit supports the entire range of iOS 11 devices with iOS 11.4 and 11.4.1 jailbreak 👉 https://www.elcomsoft.com/news/714.html #mobileforensics #ios #jailbreak #dataextraction
Post #150 212
New Advanced PDF Password Recovery with updated Device Manager and new Advanced Office Password Recovery with support for NVIDIA CUDA 10 and AMD using OpenCL 👉 https://www.elcomsoft.com/news/713.html #password #passwordrecovery #news
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →