


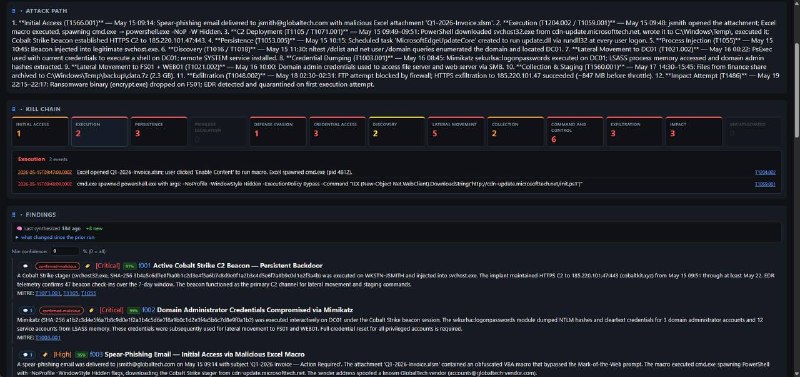


A localhost digital-forensics / incident-response companion. A browser extension captures screenshots of your investigation (Velociraptor, EDR/SIEM dashboards, Security Onion, Splunk4DFIR, VolWeb, VirusTotal, etc.) as evidence; a local server stores them, runs windowed AI vision analysis into an accumulating per-case investigation state, and serves a live dashboard plus exportable reports.
Everything runs on your machine - the companion binds to 127.0.0.1 only, evidence stays on disk, and the AI provider is yours to choose.
https://github.com/hasamba/DFIR-Companion
Post #68
521