TGViewer
Channel Public Channel
DevOps & SRE notes

DevOps & SRE notes

@devops_sre_notes

Helpful articles and tools for DevOps&SRE

youtube: https://www.youtube.com/@DevOpsAndSRENotes
Subscribers
13.3K
Photos
59
Videos
1
Links
2.6K

Showing posts older than #2041 · Back to latest

Older Posts 20 shown
Post #2039 2.03K
The article delves into the intricacies of Kubernetes resource management, specifically focusing on requests and limits. It explains how these settings impact pod scheduling, resource allocation, and performance, highlighting the importance of correctly configuring them to ensure efficient use of cluster resources and prevent overcommitting or underutilization. Understanding these concepts is crucial for optimizing application performance and reliability in Kubernetes environments.

https://thenewstack.io/how-kubernetes-requests-and-limits-really-work/
The New Stack How Kubernetes Requests and Limits Really Work A wizard's journey through the technical inner workings of Kubernetes resource management — Chapter 1.
  • 👍 6
Post #2038 1.99K
The author discusses strategies for significantly reducing the startup time of AWS EKS Windows nodes. The author achieved this by using Karpenter for dynamic node provisioning, optimizing PowerShell scripts, and pre-caching images with AWS Image Builder. Key optimizations included uninstalling unnecessary PowerShell modules and rewriting the bootstrap script in C# for better performance, resulting in startup times under 90 seconds


https://hackernoon.com/how-i-reduced-eks-windows-node-start-time-from-5-min-to-90s
Hackernoon How I Reduced EKS Windows Node Start Time From 5 Min to ~90s Learn how to reduce AWS EKS Windows node startup times to < 90 secs using Karpenter, optimized scripts, and pre-cached images. Boost your cluster's performance!
  • 👍 3
  • ❤ 1
Post #2037 2.17K
🔥 Critical vulnarabliiity in ingress-nginx controlller

9.8/10 🔥 https://github.com/advisories/GHSA-mgvx-rpfc-9mpv

If you're running Kubernetes with the ingress-nginx controller and are affected by the vulnerability described in GHSA-mgvx-rpfc-9mpv (CVE-2025-1974), you face several serious security risks:

Critical Security Risks

This vulnerability, published on March 25, 2025, is part of a set of critical flaws collectively named "IngressNightmare" with a CVSS score of 9.8[6]. The specific issues include:

- Unauthenticated Remote Code Execution (RCE): An attacker with access to the pod network can execute arbitrary code in the context of the ingress-nginx controller without authentication[1][2].

- Cluster-wide Secret Exposure: The vulnerability allows attackers to access and steal all secrets accessible to the controller. In default installations, the controller can access all secrets across all namespaces in the cluster[1][3].

- Complete Cluster Takeover: Due to the elevated privileges of the admission controller, successful exploitation could lead to full compromise of your Kubernetes environment[3][6].

- Public Exposure Risk: Over 6,500 clusters with publicly accessible admission controllers are at immediate risk, including those operated by Fortune 500 companies[8].

How the Vulnerability Works

The attack targets the admission controller component of the ingress-nginx controller:

1. The vulnerability allows attackers to inject arbitrary NGINX configuration remotely by sending a malicious ingress object directly to the admission controller[3].

2. When the controller processes this malicious object during validation, it causes the NGINX validator to execute malicious code[6][8].

3. The admission controller's elevated privileges and network accessibility create a critical escalation path, allowing an attacker to access sensitive resources across the entire cluster[3].

Required Action

To mitigate this issue, you should:

- Update immediately to one of the patched versions: 1.12.1, 1.11.5, or 1.10.7[6].

- Ensure your admission webhook endpoint is not exposed externally[6].

- Limit access to the admission controller to only the Kubernetes API Server[6].

- Temporarily disable the admission controller component if it's not needed[6].

This vulnerability affects approximately 43% of cloud environments, making it a widespread and serious threat to Kubernetes deployments[6].
GitHub CVE-2025-1974 - GitHub Advisory Database ingress-nginx admission controller RCE escalation
  • 😱 7
  • 👍 5
  • 🔥 4
Post #2034 2.16K
The article focuses on the importance of handling termination signals gracefully in applications deployed in orchestrated environments like Kubernetes. Graceful shutdowns are crucial to prevent data loss and system instability that can occur with abrupt terminations, ensuring that applications can exit cleanly and maintain consistency even when they are stopped or scaled down.

https://packagemain.tech/p/graceful-shutdowns-k8s-go
packagemain.tech Terminating elegantly: a guide to graceful shutdowns Let's dive into the world of graceful shutdowns, specifically for Go applications running on Kubernetes.
  • 👍 4
Post #2030 2.09K
This article provides a comprehensive guide on setting up a WireGuard VPN server on AWS using Terraform. It likely covers the step-by-step process of deploying a secure and scalable VPN solution, leveraging AWS infrastructure and Terraform's infrastructure-as-code capabilities.


https://vladkens.cc/aws-wireguard-vpn-terraform/
vladkens.cc Setting up WireGuard VPN at AWS with Terraform All resources in AWS work inside private VPC. Sometimes you may need to access these resources from local computer (e.g. to interact with database). Some resour…
  • 👍 6
Post #2029 2.1K
Post #2026 2.05K
This article explores how observability, particularly tracing, serves as a powerful tool for debugging and optimizing software systems at incident.io. It delves into the concept of traces and spans, explaining how they provide detailed insights into application performance and behavior, enabling developers to quickly identify and resolve issues

https://incident.io/blog/observability-as-a-superpower
incident.io Observability as a superpower | Blog At incident.io, tracing is our secret weapon for catching bugs before customers do. This blog unpacks how traces and spans are built, showcasing their role in debugging and performance tuning. From span creation to integrating traces with logs and error reports…
Post #2025 2.02K
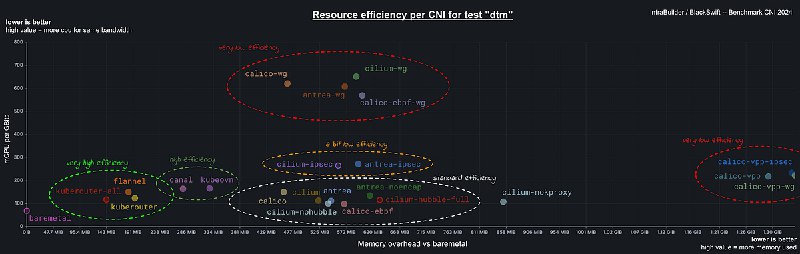
This blogpost presents a comprehensive benchmark of Kubernetes Container Network Interfaces (CNIs) over a 40Gbit/s network, conducted in early 2024. The study evaluates seven CNIs with 21 different configurations, focusing on performance, efficiency, and resource consumption.

https://itnext.io/benchmark-results-of-kubernetes-network-plugins-cni-over-40gbit-s-network-2024-156f085a5e4e
Medium Benchmark results of Kubernetes network plugins (CNI) over 40Gbit/s network [2024] This article is a new run of my previous benchmark (2020, 2019 and 2018), now running Kubernetes 1.26 and Ubuntu 22.04 with CNI version…
  • 👍 2
Post #2022 2.05K
This article explores the key areas of responsibility for engineering managers, providing insights into their multifaceted role within an organization. It likely delves into topics such as team leadership, project management, technical guidance, and strategic planning, offering valuable perspectives for both aspiring and current engineering managers.

https://levelup.gitconnected.com/the-engineering-managers-areas-of-responsibility-e25fe6c6fbb7
Medium The Engineering Manager’s Areas of Responsibility What exactly do they have to do?
  • 👍 6
Post #2021 1.99K
This author explores how Otterize simplifies workload IAM integration in Kubernetes on Azure. It demonstrates how developers can manage IAM changes directly from within the cluster, using Otterize's open-source solution to automate managed identity and policy creation

https://itnext.io/kubernetes-automate-workload-iam-on-azure-with-otterize-860faa221eac
Medium Kubernetes — Automate workload IAM on Azure with Otterize Simplifying Network and Workload IAM Integration in Kubernetes with Otterize
  • 👍 3
Post #2020 1.99K
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →