TGViewer
Channel Public Channel
๐Ÿ›ก Cybersecurity & Privacy ๐Ÿ›ก - News

๐Ÿ›ก Cybersecurity & Privacy ๐Ÿ›ก - News

@cibsecurity

๐Ÿ—ž The finest daily news on cybersecurity and privacy.

๐Ÿ”” Daily releases.

๐Ÿ’ป Is your online life secure?

๐Ÿ“ฉ lalilolalo.dev@gmail.com
Subscribers
28.6K
Photos
0
Videos
0
Links
91.2K

Showing posts older than #90373 ยท Back to latest

Older Posts 20 shown
Post #90372 335
๐Ÿ–‹๏ธ Zoom Annotation Flaws Could Let a Meeting Participant Hijack Another Attendee's Client ๐Ÿ–‹๏ธ

Anyone sharing their screen on a Zoom call could have taken over the computers of everyone watching, and anyone watching could have taken over the presenter's. The flaw sat in the annotation tool, the feature that lets participants draw and type on a shared screen, and it asked nothing of the victim beyond being in the meeting. No click, no download, no prompt, and nothing on screen to show it.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90371 272
๐Ÿ–‹๏ธ Zoom Annotation Flaws Could Let a Meeting Participant Hijack Another Attendee's Client ๐Ÿ–‹๏ธ

Anyone sharing their screen on a Zoom call could have taken over the computers of everyone watching, and anyone watching could have taken over the presenter's. The flaw sat in the annotation tool, the feature that lets participants draw and type on a shared screen, and it asked nothing of the victim beyond being in the meeting. No click, no download, no prompt, and nothing on screen to show it.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90370 249
๐Ÿ–‹๏ธ Kimwolf v7 Android Botnet Makes HTTP/2 DDoS Traffic Look Like Legitimate Browsing ๐Ÿ–‹๏ธ

Cybersecurity researchers have discovered a new version of the KimwolfAISURU Android and Internet of Things IoT botnet that comes with significant improvements to improve its operational resilience and conduct distributed denialofservice DDoS attacks. The new version, tracked as Kimwolf v7, was discovered by Palo Alto Networks Unit 42 in February 2026. "Kimwolf v7 adds an HTTP2based.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90369 204
๐Ÿ–‹๏ธ Kimwolf v7 Android Botnet Makes HTTP/2 DDoS Traffic Look Like Legitimate Browsing ๐Ÿ–‹๏ธ

Cybersecurity researchers have discovered a new version of the KimwolfAISURU Android and Internet of Things IoT botnet that comes with significant improvements to improve its operational resilience and conduct distributed denialofservice DDoS attacks. The new version, tracked as Kimwolf v7, was discovered by Palo Alto Networks Unit 42 in February 2026. "Kimwolf v7 adds an HTTP2based.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90368 198
๐Ÿ–‹๏ธ Microsoft Patches 398 Flaws Including a Windows Driver Zero-Day Under Active Attack ๐Ÿ–‹๏ธ

Microsoft released its monthly security updates on Tuesday, and one of the flaws it closed is already being used in attacks. The bug sits in a core Windows kernel driver that handles network socket operations. An attacker with code already running on a machine can use it to escalate to SYSTEM. That patch goes out first. The flaw is tracked as CVE202668820 CVSS score 7.0 and is the only.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90367 190
๐Ÿ–‹๏ธ Microsoft Patches 398 Flaws Including a Windows Driver Zero-Day Under Active Attack ๐Ÿ–‹๏ธ

Microsoft released its monthly security updates on Tuesday, and one of the flaws it closed is already being used in attacks. The bug sits in a core Windows kernel driver that handles network socket operations. An attacker with code already running on a machine can use it to escalate to SYSTEM. That patch goes out first. The flaw is tracked as CVE202668820 CVSS score 7.0 and is the only.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90366 202
โ™Ÿ๏ธ Microsoft Plugs Nearly 400 Security Holes โ™Ÿ๏ธ

Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.

๐Ÿ“– Read more.

๐Ÿ”— Via "Krebs on Security"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Krebs on Security Microsoft Plugs Nearly 400 Security Holes โ€“ Krebs on Security Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.
Post #90365 298
๐Ÿ•ต๏ธโ€โ™‚๏ธ Gunra Ransomware Gang Exploits Fortinet Flaws, Bypasses MFA ๐Ÿ•ต๏ธโ€โ™‚๏ธ

The ransomwareasaservice operation is finding success against critical infrastructure targets with leaked Conti code and old flaws in firewalls and VPN appliances.

๐Ÿ“– Read more.

๐Ÿ”— Via "Dark Reading"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Dark Reading Gunra Ransomware Gang Exploits Fortinet Flaws, Bypasses MFA The ransomware-as-a-service operation is finding success with leaked Conti code and old flaws in firewalls and VPN appliances.
Post #90364 319
๐Ÿ•ต๏ธโ€โ™‚๏ธ Microsoft's Patch Tuesday Deluge Continues With August Updates ๐Ÿ•ต๏ธโ€โ™‚๏ธ

Security experts say prioritization should be the main focus for the August updates, not the massive CVE volume.

๐Ÿ“– Read more.

๐Ÿ”— Via "Dark Reading"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Dark Reading Microsoft's Patch Tuesday Deluge Continues With August Updates The most concerning bug is CVE-2026-62878 (CVSS: 9.8), a remote code execution (RCE) vulnerability in Windows DNS Server requiring no user interaction.
Post #90363 450
๐Ÿ–‹๏ธ DeadLock Ransomware Uses Polygon Smart Contracts to Make Extortion Infra Harder to Disrupt ๐Ÿ–‹๏ธ

The ransomware group known as DeadLock has been observed using decentralized infrastructure to facilitate victim communications and data leak operations in a bid to improve operational resilience. "Its recovery ecosystem combines the Session messaging network with blockchainbacked services that store and deliver resources used throughout the extortion process," the Microsoft Threat.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
  • โค 1
Post #90362 394
๐Ÿ–‹๏ธ Researchers Disclose AI-Assisted SharePoint Exploit Chain Reaching Unauthenticated RCE ๐Ÿ–‹๏ธ

Security researchers found a way to enter Microsoft SharePoint servers as any user, including an administrator, with no valid account. A significant part of the work that found it was done through an AI agent. The flaw, tracked as CVE202655040 CVSS 9.1, affects SharePoint Server Subscription Edition, SharePoint Server 2019, and SharePoint Server 2016. Microsoft's.

๐Ÿ“– Read more.

๐Ÿ”— Via "The Hacker News"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
  • ๐Ÿ‘ 1
Post #90360 384
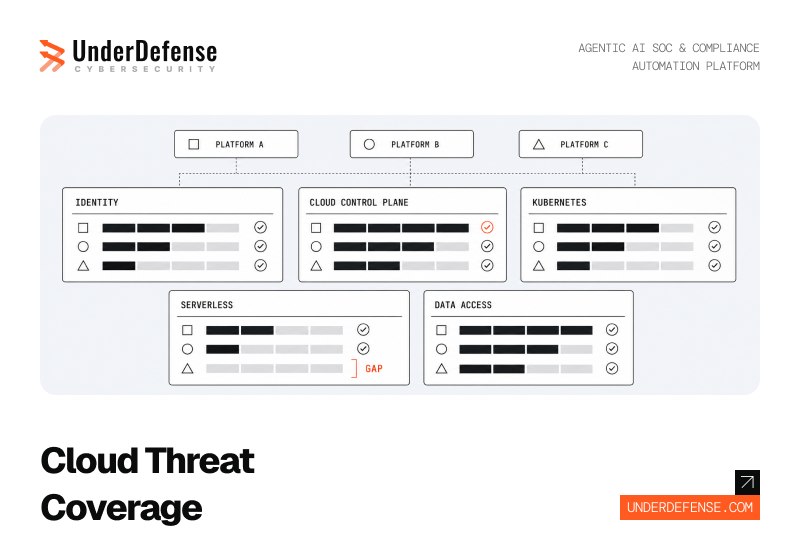
๐ŸŒŠ AI SOC Cloud Threat Coverage: MITRE ATT&CK Cloud Techniques Compared Across Leading Platforms in 2026 ๐ŸŒŠ

Discover how to validate MITRE ATTCK cloud coverage claims, prioritize identity techniques, and pick an AI SOC that responds in minutes. The post AI SOC Cloud Threat Coverage MITRE ATTCK Cloud Techniques Compared Across Leading Platforms in 2026 appeared first on UnderDefense.

๐Ÿ“– Read more.

๐Ÿ”— Via "UnderDefense"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
UnderDefense AI SOC MITRE ATT&CK Cloud Coverage Compared Across Leading Platforms 2026 Discover how to validate MITRE ATT&CK cloud coverage claims, prioritize identity techniques, and pick an AI SOC that responds in minutes.
Post #90359 247
๐Ÿ“” Only Half of UK Manufacturers Have a Cyber Incident Response Plan ๐Ÿ“”

Make UK reveals major cyber resilience gaps as 30 of UK manufacturers report recent cyber incidents.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Post #90358 283
๐Ÿ“” OpenAI Pauses Some Development of Astra Model on Security Concerns ๐Ÿ“”

OpenAI is tightening restrictions on testing of its upcoming Astra model due to security concerns.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Infosecurity Magazine OpenAI Pauses Some Development of Astra Model on Security Concerns OpenAI is tightening restrictions on testing of its upcoming Astra model due to security concerns
Post #90357 225
๐Ÿ“” Logistics Giant Ceva Suffers Data Breach Impacting European Clients ๐Ÿ“”

Supply chain attack and data breach at Ceva Logistics appears to have a large blast radius.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Infosecurity Magazine Logistics Giant Ceva Suffers Data Breach Impacting European Clients Supply chain attack and data breach at Ceva Logistics appears to have a large blast radius
Post #90356 191
๐Ÿ“” OpenAI Launches Two-Tier Security Access Program Alongside GPT 5.6 Cyber ๐Ÿ“”

Daybreak Blue removes some OpenAImade guardrails while Daybreak Red grants the use of cyberfocused frontier AI models.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Infosecurity Magazine OpenAI Launches Two-Tier Access Program Alongside GPT 5.6 Cyber Daybreak Blue removes some OpenAI-made guardrails while Daybreak Red grants the use of cyber-focused frontier AI models
Post #90355 191
๐Ÿ“” Suisan City, California, Responds to Cyber Incident Amid Wave of US Local Government Attacks ๐Ÿ“”

Police and fire response has been impacted by the attack on Suisan City, while two other local authorities have been hit by cyber incidents in the past week also.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Infosecurity Magazine Suisan City, California, Responds to Cyber Incident Amid Wave of US Lo Police and fire response has been impacted by the attack on Suisan City, while two other local authorities have been hit by cyber incidents in the past week also
Post #90354 171
๐Ÿ“” Cursor Security Bug Allowed Repositories to Execute Commands Before Trust Verification ๐Ÿ“”

Cursor fixed a pretrust code execution path in three days then closed the report as informative.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Infosecurity Magazine Cursor Security Bug Allowed Repositories to Execute Commands Pre Trust Cursor fixed a pre-trust code execution path in three days then closed the report as informative
Post #90353 160
๐Ÿ“” Six npm Packages Read C2 Addresses From Ethereum Wallet ๐Ÿ“”

Six npm packages queried an Ethereum wallet to locate C2 infrastructure.

๐Ÿ“– Read more.

๐Ÿ”— Via "Infosecurity Magazine"

----------
๐Ÿ‘๏ธ Seen on @cibsecurity
Older posts โ†’
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook โ†’Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 โ†’