APTPetitPotam PoC tool to coerce Windows hosts to authenticate to other machines via MS-EFSRPC EfsRpcOpenFileRaw function. https://github.com/topotam/PetitPotam #pentest #PetitPotam #rcp
Top 25 Penetration Testing Skills and Competencies (Detailed)
What soft skills and technical competencies does it take to became a professional penetration tester or ethical hacker? In this article we will discuss in detail what are the top 25 areas every pentester should be familiar with and what skills you should focus on if you want to become a professional penetration tester.
— Open Source Intelligence (OSINT) — Web Pentest — Network — Shells methods — Windows Systems — Linux Systems — Other Systems — Passcracking Hash & Files — Phishing, RedTeam and SE — Wireless — Cryptography — Pwn — External Resources
3/n - You can also build Jar from the command line with these commands.
Code location -> cd usercode loc for *.class files -> mkdir build location for jar -> mkdir bin Compile code -> javac -d build src/burp/*.java Build Jar -> jar cf bin/burpextender.jar -C build burp
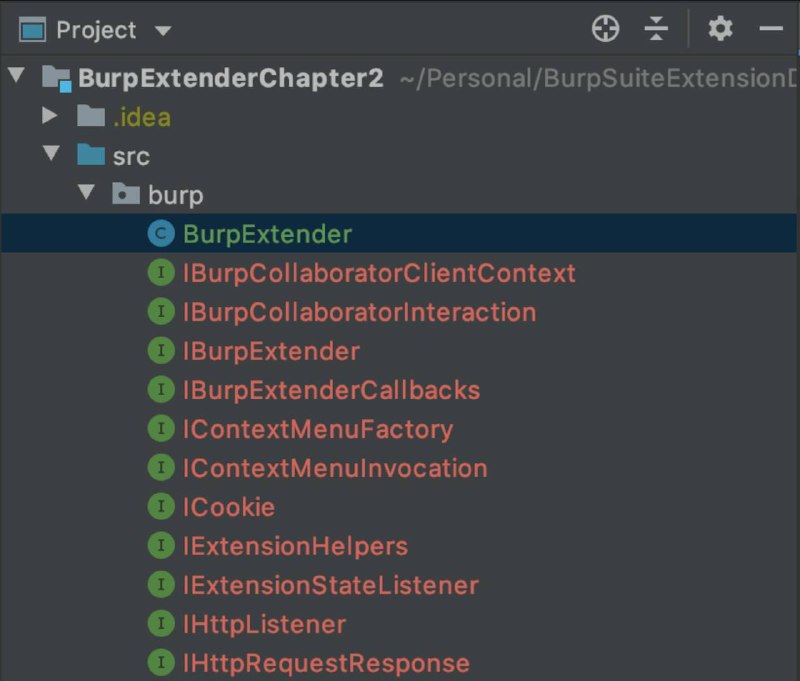
2/n - File name Burp Extender will be an entry point for your plugin, Extending interface registers this in Burp on loading. All logic for the plugin goes here. - Build Jar - Load Jar in Burp.
1/n [JAVA] - Download API interfaces from Burp -> Extender -> APIs -> Save Interface files. - Create a package name burp and save files there, you can choose any IDE of your choice. - Make IDE ready to build JAR. - Create file name BurpExtender and add the following code.