TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.6K
Photos
565
Videos
28
Links
909

Showing posts older than #1159 · Back to latest

Older Posts 20 shown
Post #1158 6.43K

Forwarded from Just Security

Открыли прием заявок на Pentest award 2025!

💡Каждый год мы зажигаем новые яркие лампочки в гирлянде отечественного рынка кибербезопасности — компетентных специалистов, которые остаются за кадром большой работы по поиску уязвимостей.

Участие все еще бесплатное, а прием заявок продлиться до 30 июня. В этом году появились новые номинации от спонсоров проекта: Совкомбанк Технологии и BI.ZONE Bug Bounty.

🥇Главный приз за победу — стеклянная именная статуэтка и макбук!
🥈🥉За вторые и третьи места призеры получат айфоны и смарт-часы.
🎬OFFZONE подарит финалистам билеты на свою конференцию 2025.
✏️А учебный центр CyberEd гранты на обучения.
Ну и конечно, самая ценная награда за участие — почет и уважение сообщества этичных хакеров.

Отправляйте заявки на сайте, участвуйте и побеждайте!
  • 👎 11
  • ❤ 4
  • 🔥 2
  • 👍 1
Post #1153 12.8K
🔑 lsassStealer

lsassStealer is a tool designed to dump the memory of the Windows process "lsass.exe". The dump is performed entirely in RAM, then compressed using the zlib library and fragmented for transmission via UDP packets disguised as NTP packets. This method helps reduce detection by security solutions such as Windows Defender and advanced Endpoint Detection and Response (EDR) tools.

🔗 Source:
https://github.com/Aur3ns/lsassStealer

#windows #lsass #edr #bypass
GitHub GitHub - Aur3ns/LsassStealer: Morpheus is an lsass stealer that extracts lsass.exe in RAM and exfiltrates it via forged and crypted… Morpheus is an lsass stealer that extracts lsass.exe in RAM and exfiltrates it via forged and crypted NTP packets. For authorized testing only! - Aur3ns/LsassStealer
  • 🔥 18
  • 🤯 4
  • 👍 3
  • ❤ 1
Post #1152 10.7K
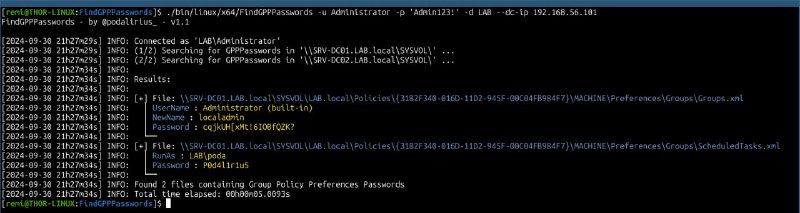
🔑 FindGPPPasswords

A cross-platforms tool to find and decrypt Group Policy Preferences passwords from the SYSVOL share using low-privileged domain accounts.

🚀 Features:
— Only requires a low privileges domain user account.
— Automatically gets the list of all domain controllers from the LDAP.
— Finds all the Group Policy Preferences Passwords present in SYSVOL share on each domain controller.
— Decrypts the passwords and prints them in cleartext.
— Outputs to a Excel file.

🔗 Source:
https://github.com/p0dalirius/FindGPPPasswords

#ad #windows #gpo #credentials
  • 🔥 15
  • 👍 5
  • ❤ 4
  • 🤔 1
Post #1151 6.78K

Forwarded from SecuriXy.kz

Обнаружена SQLi уязвимость CVE-2025-26794 в #Exim версии 4.98 при использовании сериализации ETRN.


ETRN #',1); ## INSERT SQL HERE ## /*


Для устранения проблемы рекомендуется обновиться до версии 4.98.1.

Подробности и эксплойт в контейнере доступны по ссылке https://github.com/OscarBataille/CVE-2025-26794
  • 🔥 9
  • 👍 8
Post #1150 8.24K
🦡 Technical Analysis of Brute Ratel C4 Payloads

This post provides a technical analysis of a Brute Ratel C4 badger/agent, a Red Team tool. The analysis includes API hashing, memory injection, encrypted C2 communications, and the first 20 C2 commands for remote control.

🔗 Source:
https://cybergeeks.tech/a-deep-dive-into-brute-ratel-c4-payloads/

#analysis #brc4 #redteam #blueteam
  • 🔥 13
  • 👍 4
  • ❤‍🔥 1
Post #1149 21.6K
🔍 Exploring NTDS.dit

This blog post examines the structure of the NTDS.dit file, which stores data for Active Directory. It also introduces DIT Explorer, a new open-source tool designed for analyzing NTDS.dit, demonstrating how it interprets the database to provide a structured view of the directory.

🔗 Research:
https://trustedsec.com/blog/exploring-ntds-dit-part-1-cracking-the-surface-with-dit-explorer

🔗 Source:
https://github.com/trustedsec/DitExplorer

#ad #windows #ntds #dnt
  • 👍 12
  • 🔥 7
  • 👏 2
  • ❤ 1
Post #1148 11.9K
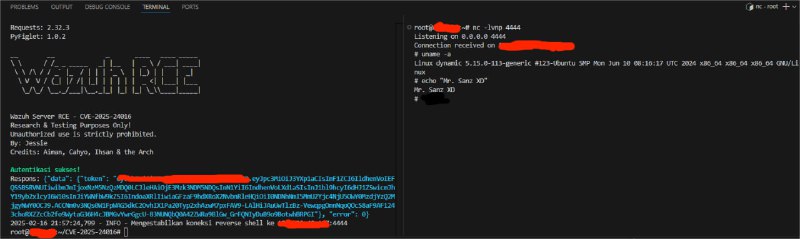
⚙️ Wazuh — Unsafe Deserialization RCE (CVE-2025-24016)

An unsafe deserialization vulnerability in Wazuh servers allows remote code execution through unsanitized dictionary injection in DAPI requests/responses. If an attacker injects an unsanitized dictionary into a DAPI request or response, they can craft an unhandled exception, allowing arbitrary Python code execution.

🔗 Source:
https://github.com/0xjessie21/CVE-2025-24016

#wazuh #deserialization #rce #cve
  • 🔥 15
  • ❤ 5
  • 👍 3
Post #1147 9.19K
🛠 PsExeSVC - Remote Execution via Python

PsExeSVC is a Python-based tool that interacts with the PsExec service to execute remote commands without relying on Windows binaries. It enables privilege escalation, remote shell access, and user authentication via primary tokens, mimicking legitimate PsExec.exe behavior while bypassing security controls like EDR detection.

🔗 Research:
https://sensepost.com/blog/2025/psexecing-the-right-way-and-why-zero-trust-is-mandatory/

🔗 Source:
https://github.com/sensepost/susinternals

#windows #ad #psexec #edr #bypass
  • 👍 7
  • 🔥 4
  • ❤ 2
Post #1146 7.08K

Forwarded from RedTeam brazzers (Миша)

Всем привет!

Недавно вышел интересный разбор LPE-уязвимости CVE-2024-12754 через AnyDesk. Разбор подробный, однако без POC. Поэтому надо исправлять :)

Сам механизм повышения привилегий основывается на возможности контроля целевого файла, который копируется в доступную для чтения низкопривилегированного пользователя директорию.

Нам остается лишь заставить AnyDesk, работающий от лица системы, прочитать файл, недоступный нам. Автор в статье использует чтение SAM из Shadow Copy.

Разработку, тестирование и отладку я проводил на AnyDesk версии 8.0.10, которую качал отсюда.

Вы можете сами попробовать POCнуть эту уязвимость, используя набор инструментов от Google Project Zero.

Моя реализация доступна здесь. Она осуществляет чтение произвольного файла, после чего копирует его содержимое на рабочий стол текущему пользователю.

Хоть Windows и активно продвигает механизм защиты, именуемый RedirectionTrust, предотвращающий переход по ссылкам, созданными не администраторами, однако эта митигация зачастую не распространяется на службы, которые были разработаны сторонними компаниями. Причина проста: разработчики не знают о ней и забывают применить, отсюда и появляется возможность LPE.

Демо можно посмотреть здесь
  • 🔥 12
  • 👍 8
  • ❤ 1
Post #1145 34.9K
🖼 AnyDesk — Local Privilege Escalation (CVE-2024-12754)

A vulnerability in AnyDesk allows low-privileged users to perform arbitrary file read and copy operations with NT AUTHORITY\SYSTEM privileges. Exploitation is possible by manipulating the background image, creating symbolic links, and leveraging ShadowCopy, granting access to SAM, SYSTEM, and SECURITY files, ultimately leading to privilege escalation to administrator.

🔗 Source:
https://mansk1es.gitbook.io/AnyDesk_CVE-2024-12754

#windows #anydesk #lpe #cve
  • 🔥 22
  • 👍 3
  • ❤ 1
Post #1144 7.92K
🔑 Windows BitLocker — Screwed without a Screwdriver

A newly discovered vulnerability in BitLocker allows attackers to bypass encryption without physical access. By exploiting flaws in Windows Boot Manager and TPM interaction, attackers can intercept or extract the BitLocker recovery key during the boot process. This makes encrypted data vulnerable even without direct physical access.

🔗 Presentation:
https://media.ccc.de/v/38c3-windows-bitlocker-screwed-without-a-screwdriver

🔗 Research:
https://neodyme.io/en/blog/bitlocker_screwed_without_a_screwdriver/#conclusion

#windows #bitlocker #bitpixie #tpm
  • 🔥 7
  • ❤ 3
  • 👍 2
Post #1143 11K
🖥 Living Off The Tunnels

Living Off The Tunnels a.k.a LOTTunnels Project is community driven project to document digital tunnels that can be abused by threat actors as well by insiders for data exfiltrations, persistence, shell access etc.

🔗 Source:
https://lottunnels.github.io/

#tunnels #persistence #cheatsheet #redteam
  • 👍 11
  • ❤ 7
Post #1142 7.89K
💻 Elevation of Privilege via Network Configuration Operators (CVE-2025-21293)

This article discusses a vulnerability in Active Directory (CVE-2025-21293) related to the Network Configuration Operators group, which has excessive permissions to create subkeys in the registry for DnsCache and NetBT. This allows attackers to leverage Performance Counters to execute code with NT\SYSTEM privileges, potentially leading to privilege escalation.

🔗 Source:
https://birkep.github.io/posts/Windows-LPE/

#ad #network #group #lpe #cve
  • 🔥 13
  • ❤ 2
  • 👍 1
  • 🤔 1
Post #1140 14.7K
🔍 Exploring WinRM plugins for lateral movement

In this blog, the process of leveraging WinRM plugins to perform lateral movement to other systems is explored. Additionally, the use of the CIM_LogicFile WMI class to bypass certain tricky detections by Microsoft Defender is examined. Finally, all the logic is incorporated into a Cobalt Strike BOF.

🔗 Research:
https://falconforce.nl/exploring-winrm-plugins-for-lateral-movement/

🔗 Source:
https://github.com/FalconForceTeam/bof-winrm-plugin-jump

#ad #winrm #cobaltstrike #bof #redteam
FalconForce Exploring WinRM plugins for lateral movement - FalconForce We explore how to leverage WinRM plugins to perform lateral movement to other systems and put all the logic in a Cobalt Strike BOF.
  • 🔥 6
  • ❤ 3
  • 👍 3
  • 🤔 1
Post #1139 7.35K
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →