TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.6K
Photos
565
Videos
28
Links
909

Showing posts older than #1056 · Back to latest

Older Posts 20 shown
Post #1054 11.7K
🔑 RockYou2024: 10 billion passwords leaked in the largest compilation of all time

Researchers discovered what appears to be the largest password compilation with a staggering 9,948,575,739 unique plaintext password

🔗 Source:
https://cybernews.com/security/rockyou2024-largest-password-compilation-leak/

🔗 Source archive:
https://fastupload.io/1824d409732f30be
https://disk.yandex.ru/d/1spMBmxcEnN95g
https://s3.timeweb.cloud/fd51ce25-6f95e3f8-263a-4b13-92af-12bc265adb44/rockyou2024.zip

#wordlist #rockyou #passwords
  • ❤ 21
  • 🔥 6
  • ❤‍🔥 4
  • 👍 2
Post #1053 5.13K
📄 Evading ETW Based Detections

In this post, Event Tracing for Windows (ETW) will be explored along with various evasion techniques used to evade detections based on this Windows event tracking and collection mechanism.

🔗 https://s4dbrd.com/evading-etw-based-detections/

#etw #bypass #windows
  • 👍 5
  • ❤ 2
Post #1052 7.96K
🤖 DojoLoader — Generic PE Loader for Prototyping Evasion Techniques

This is a versatile PE loader designed for prototyping evasion techniques. It supports downloading and executing encrypted shellcode, dynamic IAT hooking, and three Sleep obfuscation methods. Ideal for use with UDRL-less Beacon payloads from Cobalt Strike.

🔗 Blog Post:
https://www.naksyn.com/cobalt%20strike/2024/07/02/raising-beacons-without-UDRLs-teaching-how-to-sleep.html

🔗 Source:
https://github.com/naksyn/DojoLoader

#cobaltstrike #udrl #memory #evasion
  • 🔥 9
  • ❤ 2
  • 👍 1
Post #1051 38.3K
🖼️ RegreSSHion — OpenSSH Unauthenticated RCE

The Qualys Threat Research Unit has discovered a Remote Unauthenticated Code Execution vulnerability in OpenSSH’s server (sshd) in glibc-based Linux systems. CVE assigned to this vulnerability is CVE-2024-6387.

The vulnerability, which is a signal handler race condition in OpenSSH’s server (sshd), allows unauthenticated remote code execution (RCE) as root on glibc-based Linux systems.

🔗 Research:
https://blog.qualys.com/vulnerabilities-threat-research/2024/07/01/regresshion-remote-unauthenticated-code-execution-vulnerability-in-openssh-server

🔗 PoC:
https://github.com/7etsuo/cve-2024-6387-poc
https://github.com/acrono/cve-2024-6387-poc

#openssh #glibc #rce #cve
  • 🔥 22
  • ❤ 1
  • 👍 1
Post #1050 5.17K
🪞 Smoke and Mirrors — Driver Signatures Are Optional

ItsNotASecurityBoundary is an exploit that leverages False File Immutability assumptions in Windows Code Integrity (ci.dll) to trick it into accepting an improperly-signed security catalog containing fraudulent authentihashes. With attacker-controlled authentihashes loaded and trusted by CI, the kernel will load any driver of the attacker's choosing, even unsigned ones.

🔗 https://github.com/gabriellandau/ItsNotASecurityBoundary

#driver #signature #bypass #ffi #windows
  • 👍 7
Post #1047 8.8K
💻 TREVORproxy

This is a simple SOCKS proxy that helps avoid Smart Lockout by load-balancing your requests between multiple IP addresses. It accomplishes this with built-in Linux features -- no complex OpenVPN setups or strange firewall configurations.
There are two techniques that TREVORproxy can use to spread your requests across multiple IP addresses: an SSH Proxy and a Subnet Proxy.

SSH Proxy
You give TREVORproxy some hosts that support SSH, and it sends your traffic through them, making sure to balance equally between all the hosts.

Subnet Proxy
If you have access to a /64 IPv6 subnet (Linode is perfect for this), TREVORproxy will load-balance your requests across eighteen quintillion (18,446,744,073,709,551,616) unique source addresses.

🔗 Source:
https://github.com/blacklanternsecurity/TREVORproxy

#ip #ssh #rotation #waf #bypass
  • 🔥 12
  • 👍 2
  • 👎 2
  • ❤ 1
Post #1046 3.78K

Forwarded from RedTeam brazzers (Миша)

Всем доброго вторника! Помните, друзья, как круто было, когда вышел KrbRelay , a за ним KrbrelayUp? Казалось, что в тот день эксплуатация AD перевернулась с ног на голову. Или с головы на ноги.... :)) Не суть!)

Недавно я выкладывал статью, в которой постарался максимально просто описать процесс ретрансляции керберос аутентификации. Но ещё раньше появились интересные атаки: CertifiedDCOM и SilverPotato . Была лишь одна проблема - нет POCов. А что делают студенты, когда нет POCов? Правильно! Их пишут :))

Поэтому хочу вам с радостью представить тулзу RemoteKrbRelay, которая не просто совмещает в себе и SilverPotato и CertifiedDCOM, а является полноценным фреймворком для обнаружения уязвимых DCOM-обьектов!

Я добавил чекер, который выводит абсолютно всю информацию о DCOM-объектах системы в удобно читаемом виде (csv / xlsx). Помимо этого, присутствует встроенный функционал кросс-сессионной активации.

Представляете? Есть два компьютера. На одном вы, а на втором ДА. И вы можете со своего компьютера триггерить керберос аутентификацию ДА, абсолютно удаленно!) 🙂

Что ж, отмечу, что это лишь minimal POC и ему ещё есть куда расти :) Например, я пока не допилил функционал по релею керберос аутентификации из OXID Initial Resolution Request (а там вообще-то RPC_C_IMP_LEVEL_IMPERSONATE🤫). Впрочем, я готов принимать PR :))
  • 🔥 8
  • 👍 4
Post #1044 4.99K
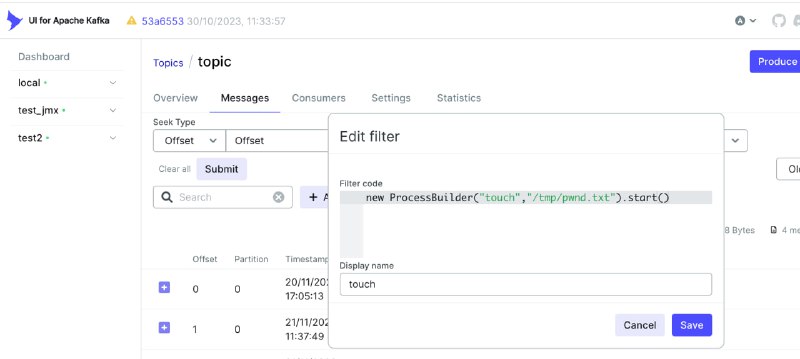
👩‍💻Apache Kafka UI RCE
(CVE-2023-52251, CVE-2024-32030)

Kafka UI is affected by two remote code execution vulnerabilities. The first vulnerability in the message filtering component leads to execution of arbitrary unsandboxed groovy script. The second vulnerability can be exploited by abusing Kafka UI to connect to a malicious JMX server, which leads to RCE via unsafe deserialization. This is particularly dangerous, as Kafka UI does not have authentication enabled by default.

🔗 Source:
https://securitylab.github.com/advisories/GHSL-2023-229_GHSL-2023-230_kafka-ui/

#apache #kafka #ui #rce
  • 🔥 7
  • 👍 2
Post #1042 4K

Forwarded from 1N73LL1G3NC3

LogHunter

Opsec tool for finding user sessions by analyzing event log files through RPC (MS-EVEN)

Youtube POC
  • 👍 12
  • 🔥 4
  • ❤ 2
Post #1041 9.53K
🔥 VMware vCenter Server RCE + PrivEsc

Multiple heap-overflow vulnerabilities in the implementation of the DCE/RPC protocol. They could allow a bad actor with network access to vCenter Server to achieve remote code execution by sending a specially crafted network packet.

CVE-2024-37079: A heap-overflow vulnerability in the DCERPC protocol implementation of vCenter Server that allows a malicious actor with network access to send specially crafted packets, potentially leading to remote code execution. (CVSS v3.1 score: 9.8 "critical");

CVE-2024-37080: Another heap overflow vulnerability in the DCERPC protocol of vCenter Server. Similar to CVE-2024-37079, it allows an attacker with network access to exploit heap overflow by sending crafted packets, potentially resulting in remote code execution. (CVSS v3.1 score: 9.8 "critical");

CVE-2024-37081: This vulnerability arises from a misconfiguration of sudo in vCenter Server, permitting an authenticated local user to exploit this flaw to elevate their privileges to root on the vCenter Server Appliance. (CVSS v3.1 score: 7.8 "high").

Nuclei Template (PoC):
🔗 https://gist.github.com/tothi/0ff034b254aca527c3a1283ff854592a

Shodan
product:"VMware vCenter Server"

FOFA
app="vmware-vCenter"


#vmware #vcenter #rce #lpe #cve
  • 🔥 12
  • 👍 3
  • ❤ 1
Post #1040 3.33K

Forwarded from Just Security

Дедлайн близко 😱

Продолжаем поиск самых выдающихся работ, относящихся к разным стадиям имитации хакерских атак. Браво, всем, кто уже прислал заявки: форма и содержание, креативная подача, мемные иллюстрации и точные метафоры — все это божественно прекрасно. Не зря мы твердим, что пентест самая творческая ИБ-профессия. Гордимся всеми участниками за ум, инициативность и смелость! 

Не упускайте шанс побороться за звание лучшего этичного хакера, получить призы и потусить с единомышленниками в камерной атмосфере на церемонии награждения. 

Делитесь своими наработками — https://award.awillix.ru/ 

#pentestaward
  • 👍 3
  • ❤ 2
  • 👎 2
  • 🔥 2
Post #1039 10.6K
🌀Voidgate

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes by performing on-the-fly decryption of individual encrypted assembly instructions, thus rendering memory scanners useless for that specific memory page.

🔗 Source
https://github.com/vxCrypt0r/Voidgate

#av #edr #evasion #hwbp #cpp
  • ❤ 12
  • 🔥 5
  • 👍 4
  • ❤‍🔥 3
  • 👎 1
Post #1038 6.16K
  • 😁 40
  • ❤‍🔥 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →