TGViewer
Channel Public Channel
ANY.RUN

ANY.RUN

@anyrun_app

Empowering businesses with proactive security solutions: Interactive Sandbox, TI Lookup and TI Feeds.
Official website: https://any.run | Sign up: https://app.any.run/?utm_source=telegram&utm_campaign=bio#register
Subscribers
882
Photos
1.2K
Videos
55
Links
1.1K
Recent Posts 15 shown
Post #1299 65
  • ❤ 2
  • 👏 1
Post #1298 65
⚠️ Everyone's talking about fake CAPTCHAs in phishing. But do you know how fast their use is actually growing?

📋 Take the poll below and see what #ANYRUN's real-world sandbox data shows: the exact number and what your SOC should do about it.
  • 👏 4
  • ❤ 3
  • 🔥 3
Post #1295 179
❗️ Active now: Attackers are mimicking AI tools like Claude, DeepSeek, and ChatGPT to deliver stealers and RATs through fake download pages, malicious installers, ClickFix commands, and even real shared chats that tell users to paste a command.

Full attack chains, behavior data, and IOCs for detection are available in #ANYRUN Sandbox 👇
🔹 Claude Lure + ClickFix
🔹 Claude Lure + Infostealer
🔹 DeepSeek Lure + ValleyRAT
🔹 ChatGPT Lure + Fake Cloudflare CAPTCHA

⚡️ See how ANY.RUN helps SOC teams detect & investigate complex threats faster
#ExploreWithANYRUN
  • ❤ 6
  • 🤯 5
  • 🤗 3
Post #1294 96
🚨 #ANYRUN's data shows phishing exposure across US averages 69.9%

⚠️ Email security alone doesn't cover the full attack surface. Sneaky2FA, EvilProxy, EvilTokens, and ClickFix all depend on post-delivery activity.

Catching them means seeing past the initial email.

👉 See ANY.RUN's phishing exposure data across finance, banking, manufacturing, government, and technology — with mitigation strategies your SOC can apply today.
  • ❤ 8
  • 👍 4
  • 🔥 4
Post #1291 108
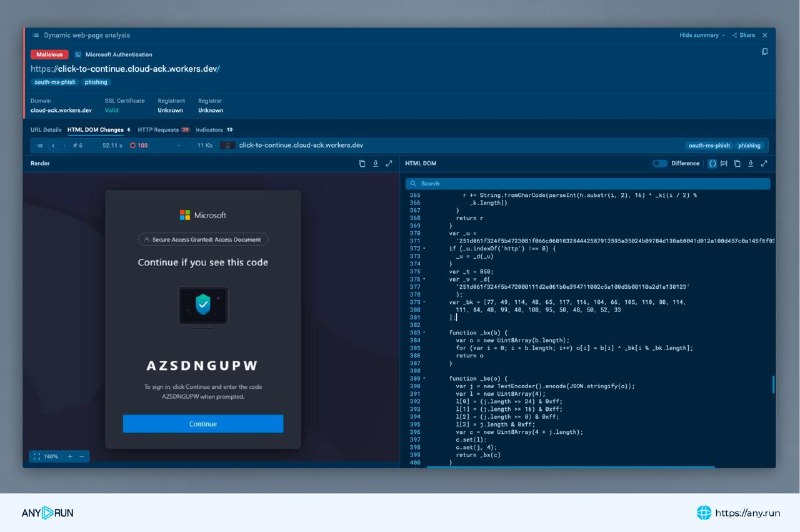
🚨 We identified Mir0Auth, a new phishkit targeting M365 auth tokens, with primary activity observed against US organizations. It starts with DocuSign-themed lures, then moves victims into Device Code phishing through source-code-like endpoints including /task_queue.cs, /context.go, and /window.rs, with XOR-obfuscated C2 URLs and request bodies. 

👉 Review the flow and decoded network logic in ANY.RUN Sandbox
🔍 Track evolving activity using this TI Lookup query: threatName:"mir0auth"

🔹 Network chain: 
Phishing page ➡️ POST /task_queue.cs beacon ➡️ POST /context.go returns a device code ➡️ the code is copied to the clipboard, and the legitimate Microsoft sign-in page at microsoft[.]com/devicelogin opens in a popup ➡️ /window.rs session polling every 3s ➡️ victim signs in ➡️ attacker session receives M365 tokens

🔹 Traffic obfuscation: 
– C2 URLs are hex strings XORed with MiroAuth 
– C2 bodies are JSON XORed with M1r0AuthBinProT0c0l_2024! 
– Data is sent as raw application/octet-stream; responses use the same key

⚡️ Strengthen phishing detection in your SOC with ANY.RUN
  • ❤ 8
  • 🔥 4
  • 👾 2
Post #1290 109
❗️ One phishing URL shouldn’t turn into hours of manual work.

To investigate faster, analysts need to inspect browser and HTTP activity, turn findings into response-ready reports, and use validated IOCs to hunt for related threats.

👉 Explore the full phishing response flow powered by ANY.RUN
  • ❤ 5
  • 🔥 3
  • 👏 2
Post #1289 110
⚡ How to keep IBM QRadar SIEM current with active threat infrastructure? Automate detection with #ANYRUN TI Feeds.

When network logs match real-time IOCs, QRadar generates a high-priority alert automatically — no manual IOC lookups, no delays in initial triage.

🎯 Connect #ANYRUN TI Feeds to IBM QRadar and see how automated correlation changes what your analysts spend time on. How to integrate 👈
  • ❤ 6
  • 👍 5
  • 🔥 4
Post #1288 112
🚨 In September, US & EU orgs faced attacks that put business access, payments, and critical systems at risk.

From session theft and RMM abuse to payment fraud, one compromise can quickly become a wider business incident.

➡️ See the biggest risks and detection gaps
  • ❤ 6
  • 👍 4
  • 🔥 4
Post #1287 114
🔥 Last call! Tomorrow, #ANYRUN and Elastic Security are running a webinar on making threat intelligence work inside SOC workflows.

Fewer manual lookups, faster decisions, fresh IOCs in your SIEM without extra steps.

➡️ Register and bring your team
  • ❤ 8
  • 👍 5
  • 🔥 4
Post #1284 131
🚨 SmartLoader delivers additional payloads while gathering system information, establishing persistence, and maintaining C2 communication on compromised Windows systems.

👉 Explore how to detect and reduce your exposure
  • ❤ 6
  • 🔥 5
  • 👍 2
Post #1283 316
⚠️ Malware pressure increased across the threat landscape last week, with RATs, stealers, and loaders all gaining activity at the same time. AsyncRAT climbed 35%, while Quasar, DonutLoader, and Lumma saw even sharper growth.

📌 Trend to watch: broad growth across established threats can increase investigation pressure across multiple threat types at once. SOC teams may need to rebalance detection and triage priorities as volumes rise.

👉 Monitor the malware driving today’s attacks

#Top10Malware
  • ❤ 7
  • 🤯 4
  • 👾 4
Post #1279 165
🇪🇸 A quick look at RootedCON Valencia 2026 through #ANYRUN's eyes.

From the risks on SOC & MSSP teams’ radar to conversations about interactive sandboxing and threat intelligence, there was plenty to take away. Thanks to everyone who stopped by! 🫶

➡️ Read the full recap
  • ❤ 9
  • 👏 7
  • 🏆 4
Older posts →

About this channel

How can I read @anyrun_app without a Telegram account?
TGViewer shows the public web preview Telegram publishes for ANY.RUN: recent posts, photos, videos and the subscriber count, with no app, login or account.
How many subscribers does ANY.RUN have?
ANY.RUN (@anyrun_app) has 882 subscribers on Telegram, refreshed roughly every 30 minutes.
Does ANY.RUN know I viewed it here?
No. Public channel previews carry no viewer identity, and TGViewer has no accounts or tracking of what you look up.
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →