TGViewer
Channel Public Channel
Android Security & Malware

Android Security & Malware

@androidmalware

Mobile cybersecurity channel
Links: https://linktr.ee/mobilehacker
Contact: mobilehackerofficial@gmail.com
Subscribers
44.8K
Photos
136
Videos
22
Links
2.9K

Showing posts older than #2340 · Back to latest

Older Posts 20 shown
Post #2337 11.4K
Post #2336 9.14K
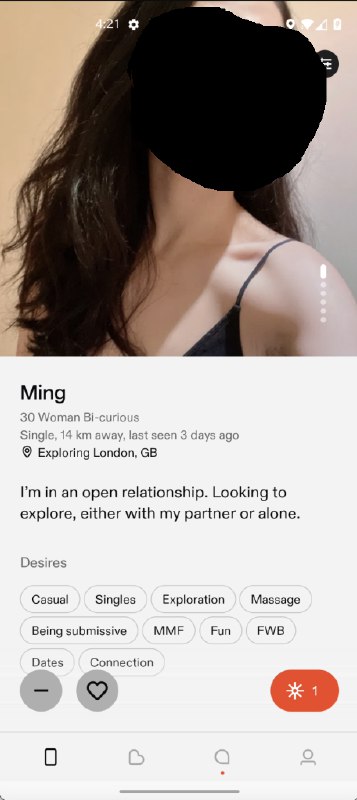
Wild vulnerabilities discovered in mobile dating app - Feeld with 1 Million installs on Google Play
-Disclosure of profile information to non-premium users
-Read other people’s messages
-access to other people’s photos & videos from their chats
-delete, recover and edit other people’s messages
-Update someone else’s profile information
-Send messages in other people’s chat
-Get a ‘Like’ from any user profile
https://fortbridge.co.uk/research/feeld-dating-app-nudes-data-publicly-available/
FORTBRIDGE Feeld dating app - Your nudes and data were publicly available Discover critical Feeld app vulnerabilities from our pentest. See how flaws in security controls expose personal data and learn key fixes.
  • 🔥 9
  • 🌚 5
  • 🤣 5
  • 👍 4
  • ❤ 1
  • 🤮 1
Post #2334 8.54K
Android Vo1d malware infected over a million Android TV boxes
It is a backdoor that puts its components in the system storage and, when commanded by attackers, is capable of secretly downloading and installing third-party software
https://news.drweb.com/show/?i=14900&lng=en
  • 👍 8
  • 🌚 3
  • 👏 1
Post #2332 13.7K
Post #2331 7.91K
Post #2327 8.6K
Post #2326 9.07K
Post #2325 9.21K
GPUAF Using a general GPU exploit tech to attack Pixel 8
We developed an advanced exploit technique capable of transforming a conventional out-of-bounds (OOB) bug into a more potent exploit primitive, specifically a page Use-After-Free (UAF). Utilizing this technique, we successfully exploited a vulnerability in the Pixel series, achieving Kernel Code Execution.
https://www.youtube.com/watch?v=Mw6iCqjOV9Q
YouTube Off-By-One 2024 Day 1 - GPUAF Using a general GPU exploit tech to attack Pixel8 Abstract Last year, we developed an advanced exploit technique capable of transforming a conventional out-of-bounds (OOB) bug into a more potent exploit primitive, specifically a page Use-After-Free (UAF). Utilizing this technique, we successfully exploited…
  • 🔥 14
  • 🌚 3
Post #2324 9.24K
Post #2321 11.1K
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →